
x402 Infrastructure for Charging AI Agents: Building Pay-Per-Use APIs and Digital Services
x402 Infrastructure for Charging AI Agents: Building Pay-Per-Use APIs and Digital Services
Meta Description: Learn the infrastructure layers developers need to charge AI agents for APIs and digital services with x402, including middleware, wallets, verification, and settlement.
Slug: x402-infrastructure-charging-ai-agents
Developers can use x402 infrastructure to make APIs, data services, AI tools, and digital resources payable by machines. The stack normally includes a resource-server integration, a payment verification or facilitator layer, an agent payment capability, merchant operations, and service-delivery logic.
The key point is that x402 is a payment protocol, not a complete business system. A developer still needs to define the paid resource, meter usage, limit spending, verify payment, deliver the result, and reconcile failures.
Reference architecture at a glance
A production stack can be separated into seven contracts. The components may come from one provider or several, but each contract needs an explicit owner.
Layer | Primary responsibility | Output consumed by the next layer |
|---|---|---|
Service discovery | Describe the resource, price basis, input, and delivery semantics | Resource or offer identifier |
Resource server | Validate the request and issue the payment requirement | Bound requirement with amount, asset, network, recipient, and expiry |
Agent wallet and policy | Decide whether the purchase is allowed and authorize it | Payment payload or proof |
Verification or facilitator | Validate the payment and, where applicable, support settlement | Verifiable acceptance or rejection result |
Merchant state | Connect request, payment, and commercial record | Order, usage, balance, or entitlement state |
Service execution | Run the API, model, tool, or digital-service job | Result or recoverable execution state |
Settlement and operations | Reconcile value, delivery, refund, and support evidence | Durable receipt and finance record |
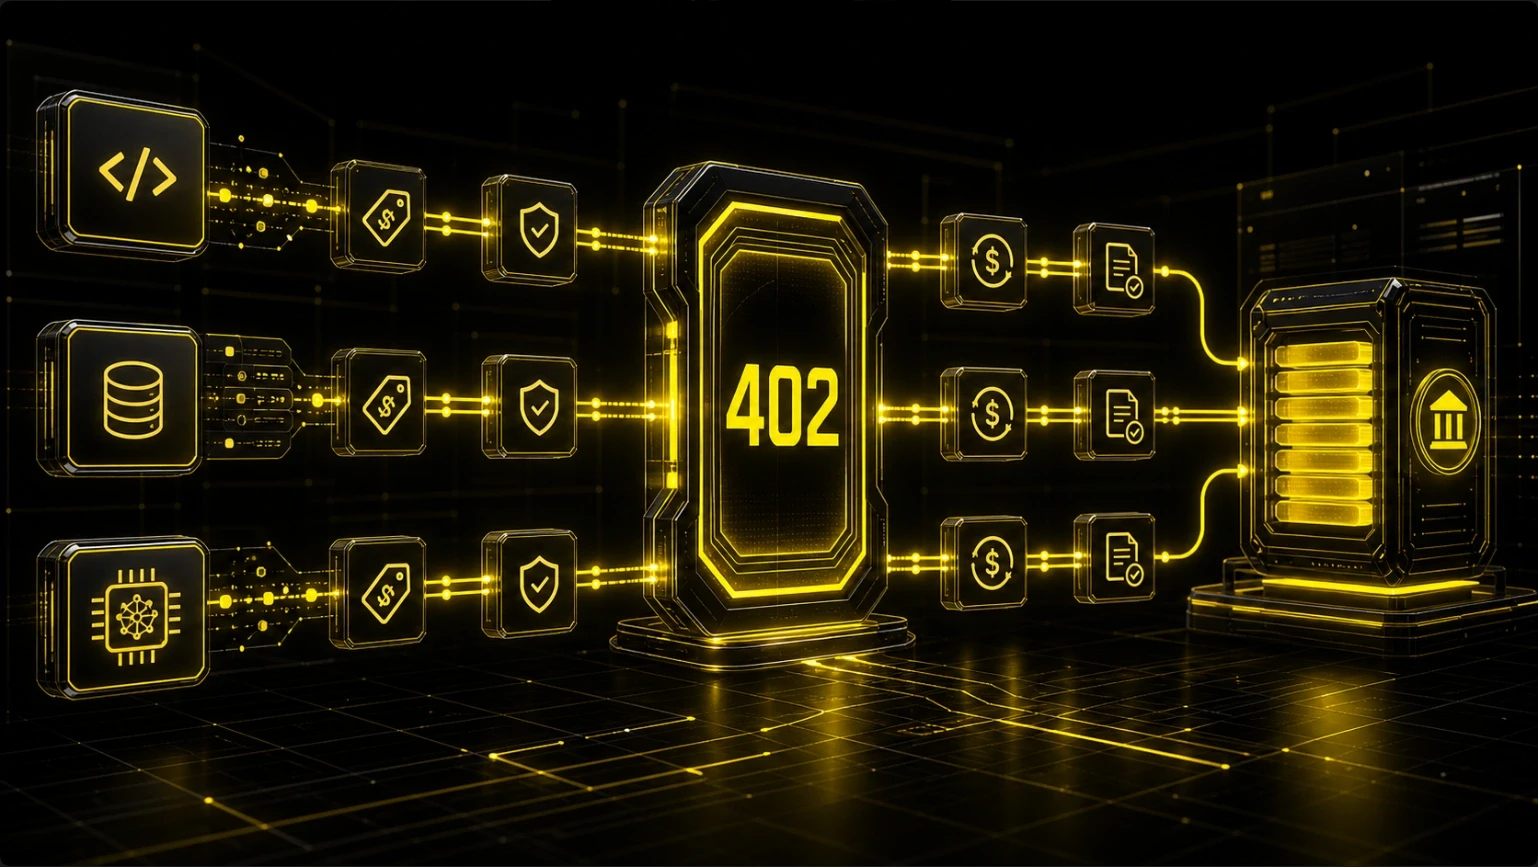
x402 defines an interoperable payment interaction around the HTTP resource. It does not require all seven layers to be bundled. A developer selecting infrastructure should therefore ask both “Can this component speak x402?” and “Which contract will still be ours to operate?”
End-to-end request and state flow
Consider an agent requesting a paid market-data enrichment endpoint.
The agent discovers the endpoint and its input schema.
It sends a request with a unique client request ID.
The resource server validates non-payment fields and creates a short-lived requirement bound to the resource, price, request digest, and merchant recipient.
The server returns HTTP 402 with acceptable payment terms.
The agent compares those terms with its budget, merchant policy, allowed network, and expected output.
The wallet authorizes and submits the chosen payment path.
The agent retries or continues the request with the required payment information.
The server or facilitator verifies payment and records a verification reference.
Merchant state changes from payment_required to paid_pending_execution.
The service executes once, stores the result, and produces delivery evidence.
The server returns the result or a status location for asynchronous execution.
Settlement and reconciliation records connect the request to payment, result, and any later refund.
This sequence separates four facts that are often collapsed: the request is valid, payment is valid, service execution succeeded, and value settled. They can happen at different times and fail independently.
The resource-server layer
The resource server owns the protected route. It decides what is paid, how much it costs, which scheme is accepted, what request or resource the payment binds to, and what response follows successful verification.
For a simple endpoint, middleware can return HTTP 402 when payment proof is missing or invalid. For a longer task, the server may create a job and return a status URL. The payment requirement should not be confused with the result.
Define the billable unit before implementing the challenge. “One request” may mean one response, one attempt, one completed job, or one unit of data. The service terms should tell the agent which interpretation applies.
The facilitator or verification layer
A facilitator can help verify or process payment requirements. This reduces the amount of chain-specific verification logic that every resource server must implement, but it does not remove merchant responsibility. The merchant still needs to confirm that the verified payment refers to the correct request and amount.
The service should maintain a durable record of the payment requirement, request ID, verification result, asset and network, amount, execution status, and delivery result. A facilitator is not automatically the merchant's order system, refund system, or customer identity layer.
Treat a facilitator response as an input to the server's authorization decision. Confirm that it corresponds to the current requirement, not merely that some transaction is valid. Bind the resource, merchant recipient, amount or pricing rule, payment scheme, network, asset, expiry, and a nonce or request-specific value where supported.
If the facilitator is unavailable, use a defined policy: fail closed, queue a submitted payment for later verification, or use another compatible verifier. Do not release a resource based only on an unverified client claim. A fallback must preserve the same requirement semantics so an attacker cannot obtain weaker checks by selecting another path.
The agent wallet and policy layer
On the buyer side, an AI agent needs an authorized way to sign or submit payment. A wallet is only one part of that capability. The agent should apply single-payment limits, task and daily budgets, service and merchant allowlists, accepted assets and networks, expiry and quote checks, retry limits, and human approval thresholds.
“Automatic payment” should mean policy-controlled execution, not unlimited spending. The payment system must be able to stop when a quote changes, a service is unknown, or a workflow exceeds budget.
GOAT Network's AgentKit is relevant to this layer because the public GOAT stack connects agent actions, wallet capabilities, x402 payments, and identity-related tooling. Developers should verify the current SDK surface and supported runtime before treating a particular plugin or action as production-ready.
Merchant operations and fulfillment
An API provider needs more than the payment response. It needs metering, rate limits, request status, retries, refunds or credits, and reconciliation. A digital service needs a delivery record. A tool needs an invocation ID and result state.
This is where GOAT Flow is relevant as a merchant infrastructure product. Its public positioning covers Checkout, QuickPay, API Payments, and merchant operations. It can sit beside a resource-server x402 flow, but it should not be described as the x402 protocol itself. A merchant should map its own offer and service IDs into the active GOAT configuration.
Define durable data contracts before choosing products
Tool names and SDK methods change. A small set of stable records makes the stack understandable and replaceable.
Resource definition. Store a resource ID, route or tool name, version, input constraints, price basis, delivery semantics, and refund rule. For variable usage, state when final quantity becomes known and how the agent approves a maximum.
Payment requirement. Record the requirement ID, resource version, request digest, amount or ceiling, asset, network, recipient, scheme, issue time, expiry, and status. Do not reconstruct old terms from the current price table.
Payment and verification. Store the payment identifier or transaction reference, permitted payer context, verifier result, verification time, and binding to the original requirement. Minimize sensitive wallet or identity data rather than copying it into every log.
Execution and delivery. Store an execution ID, attempt count, status, input digest, output digest or location, delivery time, and failure classification. A receipt can prove which paid request produced which result without exposing a confidential result.
Settlement and recovery. Keep the settlement reference, accounting amount, fees where known, refund or credit record, and reconciliation status. The record should answer whether money moved even when execution did not complete.
These contracts let the merchant replace middleware, facilitator, or execution workers without losing transaction meaning.
Settlement and evidence
Settlement tells the merchant how value was finalized under the chosen rail. It does not prove that a service was delivered. Keep settlement evidence next to order and fulfillment evidence, with correlation IDs that let an operator trace the lifecycle.
Cross-chain or multi-asset support increases the number of states: quote, route, payment, verification, settlement, and refund may each be delayed or fail differently. Do not promise automatic routing or finality without checking the active deployment.
Deployment topologies and their tradeoffs
Minimal direct integration
The API service runs x402 middleware, verifies through one supported path, executes immediately, and writes a compact receipt. This has low latency and few moving parts. It suits one or two stateless routes, but the application team owns every exception.
Facilitator-backed resource service
The server delegates payment verification and settlement-related complexity to a facilitator while retaining usage and delivery records. This reduces network-specific code but adds dependency on facilitator availability, supported schemes, and response semantics.
Merchant-platform architecture
The service connects payment to platform-managed offers, orders, webhooks, balances, and settlement views. This helps with multiple products, delayed delivery, support operations, and finance reconciliation. The tradeoff is a broader provider data model and migration surface.
Modular self-hosted stack
The developer operates the resource server, wallet policy, verifier, order service, event bus, and reconciliation jobs independently. This provides control and custom policy but creates the largest security and reliability burden.
Hybrid architecture
A common choice is to keep resource definition and execution inside the merchant application while using hosted verification and commerce operations. It remains modular when identifiers, receipts, and exports are portable and every authoritative state is documented.
Trust boundaries and security controls
Every boundary should authenticate its caller and minimize authority. The public resource route may expose price and terms, but merchant administration must use separate credentials. A webhook credential should not change prices. An execution worker should not hold unrestricted wallet keys. An agent wallet action should be constrained by policy rather than inherit all permissions of the organization that funded it.
Replay protection is required at payment and service layers. Payment proof should not unlock another resource, and the same paid request should not execute twice unless terms allow repeated use. Use nonces, expiry, requirement binding, and idempotency controls appropriate to the scheme and application.
Logs should avoid secrets and unnecessary personal or wallet data while preserving enough correlation to investigate disputes. Credential rotation, dependency updates, and emergency disable controls also belong in the launch plan. If a verifier, asset, or merchant key is compromised, operators need to stop new requirements without corrupting completed receipts.
Failure matrix for production design
Failure | Required behavior | Evidence to preserve |
|---|---|---|
Requirement expires before payment | Reject or issue a new quote; never apply new terms silently | Old and replacement requirement IDs |
Wrong amount, asset, or network | Fail verification without execution | Verification reason and submitted reference |
Payment valid but request invalid | Do not execute; apply the disclosed refund or credit policy | Validation result and payment binding |
Payment verified, execution fails | Enter paid_pending_recovery; retry, credit, or refund | Execution attempts and recovery decision |
Response lost after execution | Return stored result on idempotent retry | Request ID, output digest, delivery status |
Facilitator timeout | Fail closed or queue under explicit policy | Timeout and later authoritative result |
Duplicate retry | Recover prior state; do not charge or execute twice | Idempotency key and prior record |
Settlement disagrees with merchant state | Quarantine for reconciliation | Order, payment, settlement, and repair audit |
Turn this matrix into automated contract tests. It is more valuable than a success-only demo because it proves which layer owns recovery.
Example: charging for a research API job
Suppose a research endpoint charges a fixed amount for a report that takes up to two minutes. The request is not the completed result, so the server creates a job before issuing a requirement. The requirement binds to job ID, price, report type, and expiry.
After verification, the order moves to paid_pending_execution and a worker starts once. The API returns a status location rather than holding the connection open. On success, it stores the report, output digest, and download authorization. On failure, the order moves to recoverable_failure and applies the published retry or refund policy.
An agent retry with the same idempotency key receives the existing job. Support can search by job ID, payment reference, or agent request ID. Finance can match verified payment and settlement to the delivered report. This example needs more than route middleware, but still uses x402 at the payment boundary.
Where GOAT components can fit
GOAT Network is relevant when developers want to connect several parts of this stack. AgentKit is positioned around agent wallet and action capabilities, including x402-related and identity-oriented tooling. GOAT Flow is positioned around merchant payment and commerce surfaces such as Checkout, QuickPay, API Payments, and merchant operations.
That does not mean every deployment requires GOAT, that x402 is exclusive to GOAT, or that all capabilities are enabled in every environment. Map each required contract to the current documented SDK or product surface, verify active configuration, and keep application-owned fulfillment and policy explicit.
The useful question is whether selected GOAT components reduce real operating work while preserving identifiers and evidence across the architecture.
A production checklist
Before charging live agents, test unpaid requests, expired requirements, wrong amounts or assets, valid payment with duplicate retry, payment verified but service failed, facilitator or webhook timeout, refund or credit recovery, and reconciliation against the settlement record.
The infrastructure is ready when the developer can explain not only how the agent pays, but also how the service knows what to deliver and what happens when delivery fails.
Version the commercial interface
An agent may cache a route description or payment requirement. When a response schema, price unit, asset, or delivery guarantee changes, the provider should tell agents whether it is a new resource or a new revision. Versioning is not only a developer convenience; it preserves the meaning of payment receipts and support records.
The resource server should expose status that distinguishes a declined payment, pending verification, completed execution, and recoverable delivery failure. Those are different outcomes for a buyer agent. A single error code or generic success flag makes safe orchestration harder.
Start with one resource and one supported payment scheme. Test unpaid access, a valid payment, an expired requirement, a replay, a duplicate retry, service failure, and reconciliation. Add a second network or asset only after the first route has an operational record and a clear recovery path.
The infrastructure is mature when the protocol response, merchant order, service result, and settlement evidence can be correlated by an operator who was not present during the original request.
The operator should expose enough status to distinguish a declined payment, pending verification, completed execution, and recoverable delivery failure. Those are different outcomes for a buyer agent. A single error code or generic success flag makes safe orchestration harder.
Distinguish the protocol path from the revenue path
The protocol path is short: the resource server creates a requirement, the agent supplies payment proof, and the verifier returns a decision. The revenue path includes pricing, metering, customer or agent policy, accounting, service execution, support, and recovery.
Store request and payment IDs, preserve the accepted price, and record whether a result was actually delivered. These fields are inexpensive compared with reconstructing them after an incident. A data API should distinguish a paid request rejected for invalid parameters from a request that consumed compute but failed during delivery.
Keep the merchant surface narrow
Expose only the resources the provider can price and fulfill predictably. Start with a few endpoints and explicit limits. Add more routes when the same verification, metering, and recovery pattern can be applied safely. If a response schema, price unit, asset, or delivery guarantee changes, tell agents whether it is a new resource or a new revision.
The developer should separate public resource metadata from private merchant administration. A public agent can read that a route costs a defined amount, but it should not receive merchant API keys, balance controls, refund permissions, or internal settlement credentials. This boundary is part of x402 infrastructure even though it is not represented by the 402 status itself.
The result is a stack that protects both the resource and the merchant's operating boundary.
Implementation note
A minimal production route should have a resource ID, quote or payment requirement ID, request ID, verification result, execution state, and delivery receipt. Test the route with no payment, an expired requirement, wrong asset, duplicate retry, and service failure. Store each outcome so an operator can inspect it without reading application logs.
If the provider later adds another network or asset, repeat the same test set. A new rail adds settlement and reconciliation states even when the HTTP middleware remains unchanged. The stack should grow only when the merchant can explain those new states.
Final review checklist
Before opening the flow to more agents, review the offer, request, payment, and delivery records together. Confirm that the price or terms are current, the buyer policy can reject an out-of-scope action, the payment proof is bound to the right resource, and the service can return a result or a recoverable status. Confirm that retries do not create duplicate orders or duplicate charges.
Also review the human boundary. A merchant may require approval for an unusual quantity, a sensitive product, a high amount, a new network, or a delivery condition that the agent cannot validate. The agent should receive a clear escalation response, not a generic error. This is especially important when the merchant supports both humans and machines: the machine path should be automated where the business is comfortable, but it should not erase the controls that make the human path supportable.
Document the active configuration and revisit it when the product, payment scheme, or fulfillment system changes. A repository example or protocol capability is not proof that every option is enabled for the current merchant deployment.
The same discipline applies to pricing changes, SDK upgrades, and facilitator changes. Record the effective version, run the negative tests again, and verify that old receipts remain interpretable. An x402 route becomes dependable when a developer can explain its behavior across versions, not only when the first request succeeds.
Selection and rollout plan
Begin with the billable unit and delivery promise. Assign an owner to each of the seven architecture contracts, then select components. This order prevents a product name from hiding an unowned responsibility.
Implement one resource, one payment scheme, one network, and one asset first. Add structured records and idempotency before expanding. Run the failure matrix, measure verification and total delivery latency, and reconcile a complete test period. Introduce another route only when the first can be recovered by an operator who did not build it.
During provider evaluation, request the exact requirement, verification, webhook, order, and export objects. Confirm credential scopes, retry behavior, status lookup, and replacement options. Treat repository examples as implementation evidence, not proof that production enables every option.
The target is an architecture in which agents pay within explicit policy, merchants deliver exactly once or recover visibly, and finance can explain where value settled. That is the difference between adding a 402 response and operating x402 infrastructure for paid services.
FAQ
Can x402 charge for any API?
It can protect HTTP resources that have a clear payment requirement. The developer still needs to design metering, authorization, rate limits, and delivery.
Is a facilitator mandatory?
The exact architecture varies. A facilitator can simplify verification and settlement, while a developer may implement more logic directly. The merchant must still validate the payment-resource relationship.
Is GOAT Network only a facilitator?
No. GOAT Network positions GOAT Flow as a commerce and payment product and AgentKit as an agent action and runtime layer. x402 is the broader protocol used by relevant machine-payment surfaces.
What is the minimum production stack for a paid API?
At minimum, define the resource and price, issue a bound requirement, authorize and verify payment, execute idempotently, preserve delivery evidence, and reconcile payment with settlement. Components can be combined, but none of these responsibilities should be unowned.
Does payment verification prove service delivery?
No. Verification proves that payment met the checked requirement. Service execution and delivery need separate state and evidence.