
Selling API and Data Access to AI Agents With Pay-Per-Request x402 Payments
Selling API and Data Access to AI Agents With Pay-Per-Request x402 Payments
Meta Description: Learn how to sell API and data access to AI agents per request with x402 payment requirements, verification, metering, retries, and delivery records.
Slug: sell-api-data-access-ai-agents-x402
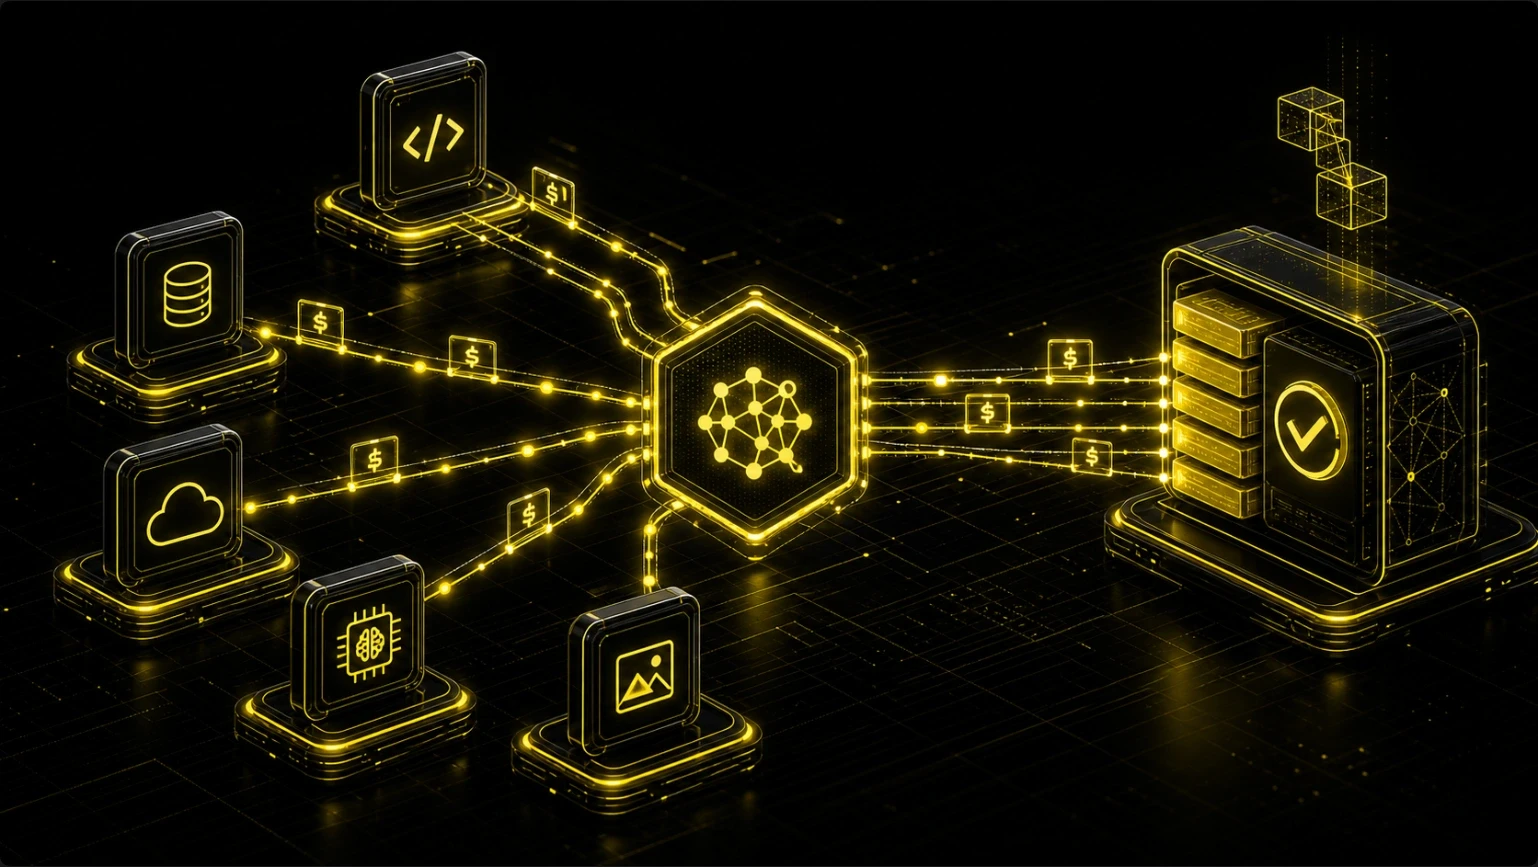
An API provider can sell a data response to an AI agent without creating a permanent account for every caller. The provider protects the resource with a machine-readable payment requirement, verifies payment, executes the request, and returns the result. x402 is designed for this request-level pattern, but the payment challenge is only one part of the merchant system.
The practical lifecycle is:
Request -> HTTP 402 -> payment requirement -> policy check -> payment -> verification -> service execution -> result and receipt.
Define the billable unit
Before adding middleware, decide what one payment buys. A weather result, market-data snapshot, search response, model inference, or file conversion may each have a different unit.
Document:
endpoint or tool;
request scope;
response or result unit;
price and asset;
rate limit;
maximum response size or execution time;
refund or retry behavior;
whether the payment covers one attempt or one successful result.
“Pay per request” is not precise if one request can trigger ten minutes of compute or a large dataset. The billable unit must be understandable to the agent and enforceable by the service.
Return a payment requirement at the resource boundary
When the request lacks valid payment proof, the server can return HTTP 402 Payment Required with the information required to proceed. The response should identify the amount, asset, destination, network or scheme, expiry, and resource binding.
Do not put a secret API key in the payment requirement. Do not treat a free-form description as an authorization policy. The agent should compare the requirement to its own task budget and allowed services before signing.
The server must also prevent the requirement from being reused for a different route or request if that would change the commercial meaning. Expiry, nonce, request identity, and resource binding are implementation details that reduce replay and ambiguity risk.
Verify before returning protected data
The service should verify payment before it releases the paid response. Verification can be handled by a facilitator or merchant-side verification component, depending on the chosen x402 deployment.
The verification result should connect to:
request ID;
payment requirement ID;
payer or payment proof;
amount and asset;
verification time;
service execution state.
Do not return the response merely because the agent supplied a transaction hash. A hash may refer to an incomplete, wrong, or unrelated transfer. The merchant needs a trusted status decision.
Meter usage and make retries safe
A paid API still needs rate limiting and usage records. Payment proves a payment event; it does not prove that the caller is entitled to unlimited requests.
Use a request or idempotency ID. If the agent pays and the HTTP response is lost, a retry should let the server look up the previous attempt. The provider can then return the stored result, show that execution is still pending, or issue a recovery response. Charging again by default is a poor machine-to-machine contract.
For long-running jobs, separate payment acceptance from execution. The API can return an accepted job ID, then expose a status endpoint. The payment receipt should not be confused with the final result.
GOAT Network's x402 repository and GOAT Flow product are relevant to merchants building this kind of surface because they address payment-gated HTTP resources and merchant operations. The repository's implementation details should be checked against the active deployment; documentation and example code do not by themselves prove that every scheme, token, or network is enabled for public merchants. Start with the merchant guide.
Design accountless access carefully
Accountless does not mean anonymous, unlimited, or untraceable. A provider may still need:
abuse prevention;
rate limits;
service identity;
risk scoring;
contractual restrictions;
an audit record;
a refund path.
Payment can be the admission credential for a narrow resource, while a separate identity or API key remains necessary for privileged or persistent access. x402 is strongest when the resource is small, well-defined, and priced per call or per result.
A minimal production test
Test the full path with:
unpaid request returns a clear 402;
agent rejects a price over budget;
valid payment is accepted once;
duplicate retry returns the same result;
invalid or expired proof is rejected;
provider failure creates a recoverable state;
usage and settlement records reconcile.
The provider is ready when it can explain both successful and failed calls without asking the agent to manually interpret a dashboard. Pay-per-request infrastructure is a revenue system, not just a response status.
Treat a paid request as a contract
The provider should publish what successful delivery means. For a data endpoint, it may mean a response matching the requested schema. For an inference endpoint, it may mean a completed result or an explicitly best-effort computation. For a scraping job, it may mean a job record rather than an immediate dataset. The payment terms should not imply a stronger guarantee than the service can provide.
Use versioned request and response schemas. If the resource changes materially, the provider should expose a new version or a clear compatibility rule. This lets an agent evaluate whether the result is suitable before paying and lets the merchant reconcile older requests after a deployment.
The provider should also measure conversion from 402 to verified payment, verified payment to execution, and execution to delivered result. A low payment conversion can mean pricing is unclear. A high payment-to-delivery failure rate means the service is charging for a workflow it cannot reliably complete. These metrics guide product changes without treating raw request volume as revenue.
A good x402 API is therefore a small merchant system: price, authorize, verify, execute, deliver, and recover.
Price the response, not just the route
Two endpoints with the same URL shape can have very different costs. A request that returns ten records should not be priced like one that returns a million. A model call with a long context may consume more resources than a short classification call. The provider can expose tiers, usage limits, or a quote that binds the request to the expected unit.
The provider should decide whether a failed service attempt is chargeable. Charging for compute consumed can be defensible for a best-effort research job; charging for a promised result that never arrived may require a credit or refund. The terms should be clear before payment.
Protect the service from paid abuse
Payment is not an abuse-prevention system. A malfunctioning agent can pay for too many calls, replay a valid proof, send oversized inputs, or use multiple wallets. Apply rate limits, input limits, request authentication where needed, and resource quotas.
For higher-risk data, payment-gated access may still need identity or a contract. A small payment can establish that a payment requirement was met; it does not grant the right to redistribute confidential data or bypass a service policy.
A provider should publish a contact or recovery path for cases that automation cannot resolve. This is not a failure of machine commerce; it is a boundary for exceptional cases. An agent that can identify a failed payment, a pending execution, or an unavailable result can pause safely instead of repeating the same action and increasing the charge.
The result is a payment contract that remains understandable when the service is slow, variable, or temporarily unavailable.
Implementation note
Before opening a paid route, write a small request contract: input limits, price unit, expiry, delivery definition, retry rule, and refund rule. Test a request that is paid but invalid, paid but slow, and paid but delivered after the client timed out. The provider should return a retrievable state rather than invite a second charge.
This contract can begin with one endpoint. The provider can later add batch pricing or long-running jobs without pretending that every route has the same unit economics.
Final review checklist
Before opening the flow to more agents, review the offer, request, payment, and delivery records together. Confirm that the price or terms are current, the buyer policy can reject an out-of-scope action, the payment proof is bound to the right resource, and the service can return a result or a recoverable status. Confirm that retries do not create duplicate orders or duplicate charges.
Also review the human boundary. A merchant may require approval for an unusual quantity, a sensitive product, a high amount, a new network, or a delivery condition that the agent cannot validate. The agent should receive a clear escalation response, not a generic error. This is especially important when the merchant supports both humans and machines: the machine path should be automated where the business is comfortable, but it should not erase the controls that make the human path supportable.
Document the active configuration and revisit it when the product, payment scheme, or fulfillment system changes. A repository example or protocol capability is not proof that every option is enabled for the current merchant deployment.
Reference architecture for a paid endpoint
A production design separates protocol handling from business execution. The main components are:
Route policy. Maps the HTTP method and resource to price, asset, network, payee, expiry, and product version.
x402 resource server or middleware. Detects missing payment, returns the payment requirement, parses the paid retry, and invokes verification or settlement in the required order.
Facilitator or local verifier. Validates the payment payload and, where the selected scheme requires it, performs settlement.
Request ledger. Stores the idempotency key, requirement, payment state, execution state, result pointer, and refund or credit state.
Service executor. Runs the data query, inference, conversion, or tool after the payment gate and input validation pass.
Delivery layer. Returns the synchronous result or a job reference and preserves a retrievable receipt.
Merchant operations. Reconciles payments, service outcomes, exceptions, balances, and customer support.
The resource middleware should be narrow. It should not contain the provider's entire pricing engine or fulfillment logic. Its job is to resolve a route policy, enforce the payment boundary, and pass an authenticated commercial context to the service.
The service should receive a normalized context such as request ID, product version, billable unit, payment reference, payer identifier when available, and authorization result. That context is more useful than a raw transaction hash because it has already been checked against the current requirement.
Walk through one complete API call
Consider a research API that charges $0.05 for a normalized company profile.
The agent sends a request with the company identifier and an idempotency key. The server validates the shape but sees no payment payload, so it returns HTTP 402 with a requirement bound to the route, price, supported asset, destination, network, and expiry.
The agent compares the requirement with its task budget and allowlist. If approved, its wallet or payment service creates the required payload. It retries the same logical request with the payment data and the original idempotency key.
The resource server resolves the same route policy and verifies that the payload matches it. A facilitator may perform verification and settlement, or the deployment may handle the supported scheme locally. The server records the payment decision before executing the expensive data job.
If the profile can be generated quickly, the service returns the result and a payment response or receipt. If processing is asynchronous, it returns an accepted job ID and status route. The request ledger links the job to the payment, so a client timeout does not create a second charge.
If generation fails, the system marks the execution separately from the successful payment. Its commercial policy then determines whether to retry automatically, issue a reusable credit, or refund. The agent receives a deterministic state rather than another 402.
Decide when verification and settlement occur
The x402 specification separates payment verification from settlement and allows scheme-specific ordering. Providers should follow the selected scheme rather than assuming every payment must use the same sequence.
Verification answers whether the submitted payment payload satisfies the stated requirement. Settlement commits or executes the payment according to the scheme. Protected execution must not run with no required check, but the exact order affects latency and risk.
For a cheap, deterministic response, the provider may prefer stronger payment assurance before executing. For an expensive job whose result can fail, the commercial design may need escrow, deferred capture, credit, or explicit best-effort terms rather than a simplistic “pay first” rule. The protocol mechanism and the merchant's delivery promise must agree.
Do not advertise a refund or delayed-settlement behavior simply because a type exists in an SDK or repository. Confirm that the active facilitator, asset, network, merchant configuration, and server implementation support the intended flow.
Make request binding and replay protection explicit
A payment accepted for one resource should not unlock another resource with a higher price or different commercial meaning. Bind the payment requirement to the canonical resource description, method, amount, asset, network, payee, and validity window required by the implementation.
The server must also decide what a retry means. The same idempotency key with the same normalized input should resume or return the original request. The same key with different input should produce a conflict. A new key with a replayed payment payload should fail if the scheme does not permit reuse.
Nonce and expiry checks prevent old authorizations from remaining valid indefinitely. Request hashing can help when price depends on input, but the hash must be derived from a canonical representation; otherwise equivalent JSON bodies can produce inconsistent identities.
Store only what is needed for operations and audit. A request ledger can retain hashes, references, amounts, statuses, and result pointers while avoiding unnecessary sensitive input or complete agent transcripts.
Add discovery without confusing it with payment
Agents need a way to learn that the paid route exists, what it does, and approximately what it costs. Discovery metadata can describe the endpoint, input schema, output schema, price unit, network, and supported assets.
That metadata is not itself payment authorization. The client should still obtain the current payment requirement from the protected resource or trusted current manifest. Catalog inclusion also is not guaranteed merely because payment verification succeeds; discovery and facilitator catalog behavior can be separate implementation concerns.
Use official x402 SDKs or maintained integrations to declare and validate extension metadata rather than hand-rolling protocol objects. Keep discovery descriptions stable enough for agents to plan, while allowing the resource server to return current commercial terms.
GOAT Flow paid API routes can be evaluated as one merchant implementation of this broader pattern. Its merchant operations are relevant when the provider needs more than middleware: products or routes, orders, API credentials, webhooks, balances, and reconciliation. x402 remains the broader protocol and is not exclusive to GOAT.
Observe the paid request as a distributed trace
A useful trace connects the incoming HTTP request, payment requirement, wallet authorization, verification or settlement operation, service execution, result, and merchant record.
Record a correlation ID across these stages and expose a buyer-safe request or job reference. Measure:
unpaid-to-paid conversion;
authorization rejection reasons;
verification and settlement latency;
service execution latency;
paid requests that fail before delivery;
duplicate retries recovered by idempotency;
refunds, credits, and unresolved exceptions;
contribution margin by billable unit.
Separate payment latency from service latency. Otherwise a slow model invocation may be misdiagnosed as a settlement problem, or a facilitator timeout may be hidden inside generic API duration.
Alert on inconsistent states, especially payment confirmed with no execution record, execution completed with no delivery reference, and repeated payments for the same idempotency key.
Production launch sequence
Begin on a test environment with a fixed-price, deterministic endpoint and a small allowlist. Confirm that unpaid requests return a valid 402, over-budget payments are rejected by the client, valid payment succeeds, and malformed or expired payloads fail.
Next test operational failures: terminate the client after payment, delay the verifier, duplicate the paid request, fail the service executor, and replay the payload against another route. The request ledger should explain each outcome.
Then expose a limited production route with conservative price and input limits. Reconcile every payment and delivery during the pilot. Add dynamic pricing, long-running jobs, more networks, or broader discovery only after the provider can recover the initial flow.
The implementation is complete when an agent can pay once, receive either the promised result or an explicit recoverable state, and retrieve the same transaction after an interruption.
FAQ
Does x402 remove the need for API keys?
Not universally. Payment-gated access can replace account credentials for some public, low-risk resources. Privileged data, persistent identity, negotiated contracts, or higher rate limits may still require authentication and authorization.
Can an agent pay without a wallet?
The agent needs an authorized payment capability, which may be a wallet, delegated payment service, prepaid balance, or another supported payer implementation. x402 does not create spending authority by itself.
What happens if the service fails after payment?
Record payment and execution separately. Return a request or job state that supports idempotent retry, credit, refund, or manual review according to terms disclosed before payment.
Is a facilitator required?
A facilitator is optional in the x402 architecture but can simplify verification and settlement across supported schemes and networks. A provider may self-host or verify locally when its implementation and operational capacity support that choice.