
Building the Crypto Payment Stack for AI Agents: Wallets, Identity, x402 Payments, and Settlement
Building the Crypto Payment Stack for AI Agents: Wallets, Identity, x402 Payments, and Settlement
Meta Description: Understand the crypto payment stack for AI agents across wallets, identity, x402 payment capability, settlement, policy, and service delivery.
Slug: crypto-payment-stack-ai-agents-wallets-identity-settlement
A crypto payment stack for AI agents is not just a wallet and a payment API. A usable stack must answer four different questions:
Wallet: what can the agent authorize?
Identity: who is the agent or service?
Payment: what resource is being paid for?
Settlement: how is value finalized and recorded?
These layers can be modular. They do not need to come from one provider, but they must pass identity, authorization, payment, and settlement evidence between them.
Reference architecture: four planes, six evidence objects
The four layers are easier to compose when each has an explicit authority and output.
Plane | Authoritative question | Primary evidence |
|---|---|---|
Wallet and policy | Is this agent allowed to authorize this action now? | Policy decision and signature or payment payload |
Identity and reputation | Which agent or service is acting, and what claims can be checked? | Identifier, ownership proof, reputation or validation reference |
x402 payment | What resource, amount, recipient, asset, network, and expiry are being paid? | Payment requirement and verification result |
Settlement and merchant operations | Where did value finalize, what was delivered, and how is it reconciled? | Transaction, settlement, order, delivery, and refund records |
Across these planes, a transaction should preserve six distinct objects:
an agent or principal identifier;
an authorization decision;
a resource or offer identifier;
a payment requirement;
payment and settlement evidence;
a delivery receipt.
No single object substitutes for all the others. A wallet signature is not reputation. Registered identity is not spending permission. Payment verification is not delivery. Settlement finality is not a refund policy.
How evidence moves through one purchase
Assume a research agent needs to buy a verified data result.
The discovery step returns a service identifier, resource description, price basis, and any identity or reputation references. The agent resolves enough of those references to decide whether the service is eligible. It then sends a request and receives an x402 payment requirement bound to the chosen resource.
The policy engine evaluates the final terms against task budget, per-payment limit, service allowlist, approved asset, network, and expiry. If permitted, the wallet signs or submits the payment. The payment layer verifies that the proof satisfies the same requirement the policy evaluated.
The merchant executes the service and produces a delivery receipt. Settlement evidence is then correlated with the requirement and delivery record. If the service fails after payment, the payment remains valid while the delivery state moves into retry, credit, refund, or manual review.
This flow is important because it prevents “trust” from becoming one boolean. Each layer makes a narrower decision using evidence it is qualified to interpret.
Wallets hold capability, not business authority
An agent wallet can sign a transaction or control a balance. It should not automatically be allowed to spend everything in that balance.
The wallet layer should work with a policy engine that checks:
task budget;
single-payment maximum;
daily or workflow limit;
approved merchants and contracts;
allowed networks and assets;
quote expiry;
approval escalation.
A wallet transaction is an action. The policy engine decides whether that action is permitted. Separating those concerns makes it possible to rotate a wallet or change a budget without rewriting the merchant logic.
The policy decision should include more than approve or deny. It should record the rule version, principal, task, amount, currency or asset, network, merchant or service, expiry, and any human approval. That record allows an operator to explain why a payment was allowed months later.
Delegated wallets need explicit scopes. One agent may be allowed to spend a small amount on data but not transfer funds to arbitrary addresses. Another may request a purchase but require a separate treasury agent or human signer to approve it. Separate request, approval, and signing roles where the value or risk justifies it.
Gas or network fees need policy too. A nominally inexpensive purchase can become uneconomic or exceed budget if execution costs rise. The agent should evaluate total authorized cost and stop rather than repeatedly retry an unaffordable route.
Identity gives the payment a subject
Payment rails explain how value moves. They do not always explain who is paying, what service the buyer represents, or whether a counterparty has a trustworthy history.
Agent identity can support discovery, ownership checks, reputation signals, and authorization decisions. ERC-8004 is relevant to this category because it addresses identity and reputation registries for trustless agents. It should not be described as a token standard or as a universal guarantee that an agent is safe.
Identity also creates privacy choices. A merchant may need enough identity to enforce a service rule, while a buyer may not want to expose unnecessary personal or organizational data for a low-value request. The stack should make the minimum required evidence explicit.
Identity, reputation, and validation should remain separate concepts. Identity supports continuity and ownership. Reputation summarizes past interactions or attestations. Validation provides evidence about a specific claim, capability, or outcome. A persistent identifier with no history is not reputable, while a high reputation score from an unknown or manipulable source is not sufficient proof for a sensitive purchase.
ERC-8004-style registries are relevant because they create interoperable places for agent identity and reputation-related records. Applications still need a trust policy: which registries or validators are accepted, how recent the evidence must be, whether it applies to the requested service, and what happens when a registry is unavailable.
x402 binds payment to an HTTP resource
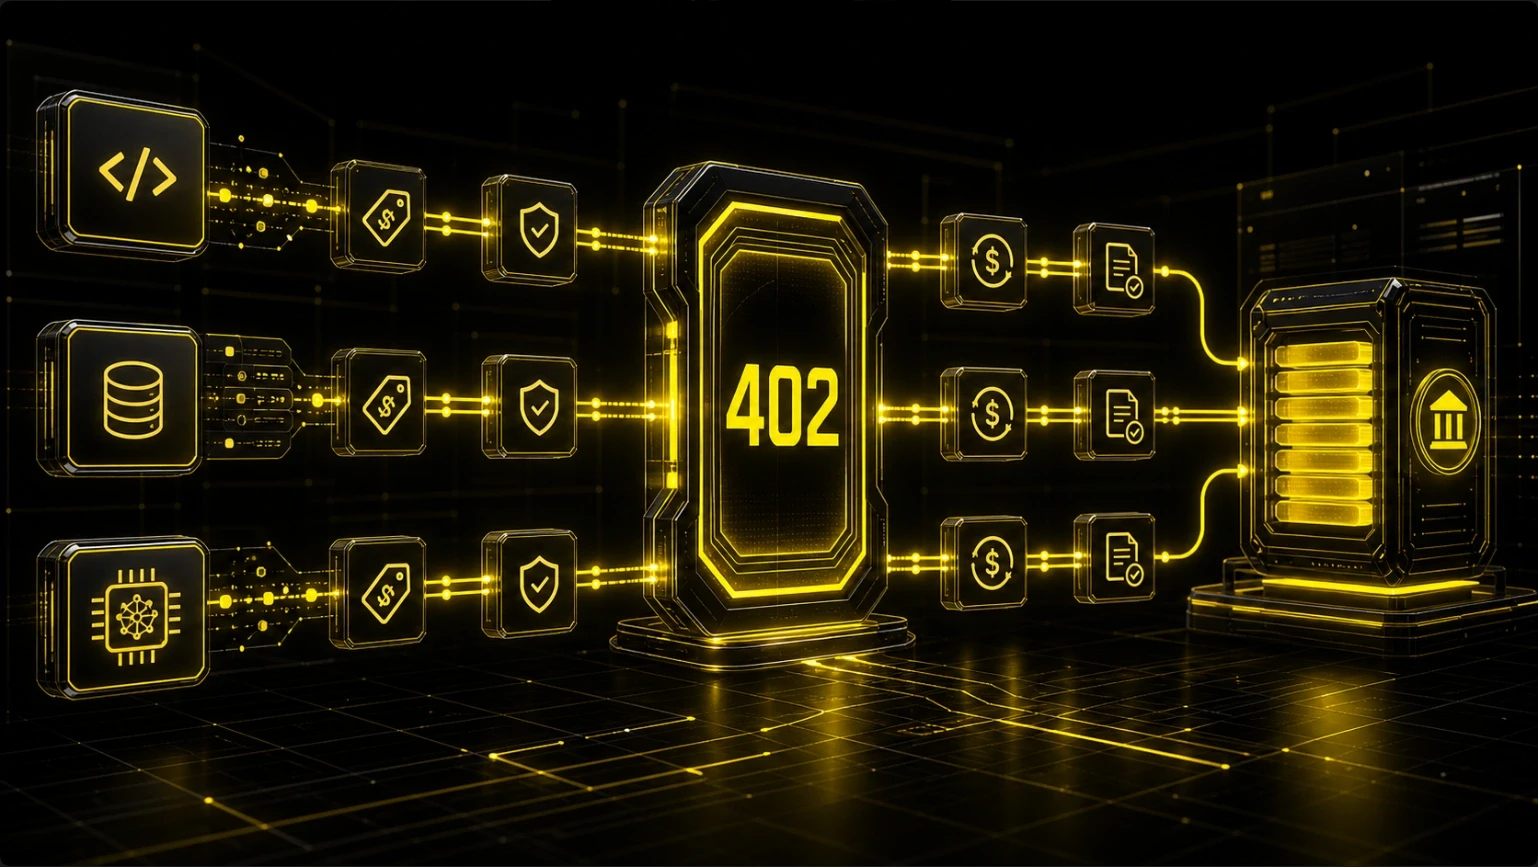
x402 provides an HTTP-native pattern for payment-gated resources. The server can return HTTP 402 with a payment requirement. The agent evaluates the requirement, pays through its authorized capability, and retries with proof. The server verifies payment and returns the resource.
This is useful for APIs, data, AI tools, digital content, and other machine-priced services. It does not replace:
persistent identity;
rate limits;
purchase authorization;
order state;
fulfillment;
refund logic.
The payment requirement should identify the amount, asset, destination, expiry, and resource binding. The agent should compare those values against its policy before signing.
The policy check and verification check must refer to the same requirement. Otherwise an agent can approve one quote and pay another. Preserve a canonical requirement identifier or digest and bind it to the resource, merchant recipient, allowed payment scheme, exact amount or maximum, asset, network, and expiry.
For variable-price services, use a ceiling or preauthorization rule that the agent understands before work begins. The final debit should be derived from measured usage and must not exceed authorization. For fixed-price resources, reject a mismatched amount rather than treating overpayment or underpayment as implicit consent.
Replay protection belongs here and at the service layer. A valid payment proof should not unlock a second resource, and a retry should recover the original result rather than trigger a second charge or execution.
Settlement provides final financial evidence
Settlement is the layer that records how the payment reached its intended destination under the chosen network and asset. It may involve a direct transfer, a facilitator, or a broader cross-chain route. Settlement speed and finality depend on the active rail.
The merchant should correlate settlement evidence with:
offer or resource ID;
order or request ID;
payer or agent identity;
payment requirement;
fulfillment result;
refund or recovery state.
Without those links, a merchant may know that a transfer occurred but not which service it bought.
GOAT Network is relevant because its public agent and commerce stack connects AgentKit, x402, ERC-8004-related identity and reputation concepts, GOAT Flow merchant operations, and Bitcoin-secured infrastructure. The appropriate role depends on the application: AgentKit can support agent-side actions, while GOAT Flow addresses merchant commerce surfaces. Developers should verify current SDK and deployment support before selecting a production route.
Settlement is a policy input as well as a finance record
An agent or merchant may face several networks or assets. The selection should account for accepted payment schemes, available balance, fees, expected confirmation, settlement assurance, refund path, and treasury preferences. “Cheapest network” is not a sufficient rule if the merchant does not accept it or if operational evidence is difficult to reconcile.
The system should distinguish payment submission, verification, confirmation, and merchant-defined settlement readiness. Those states may collapse on one rail and remain separate on another. A service can choose to deliver after verified authorization, after network confirmation, or after a stronger settlement threshold, but the decision should match value and risk.
Cross-chain routing adds quotes, route expiry, bridge or liquidity dependencies, and possibly different refund mechanics. Do not let a routing failure trigger an uncontrolled sequence of new payments. The agent should retain the original purchase intent, request renewed authorization when material terms change, and preserve each attempted route for audit.
Finance needs a normalized record even when rails differ: gross amount, asset, network, payer and payee references where permitted, fee, settlement status, exchange-rate source if converted, order, delivery, and refund state.
Use a layered failure model
Different failures belong to different layers:
Failure | Layer to inspect |
|---|---|
Agent signs over budget | Wallet policy |
Unknown counterparty | Identity or trust |
Wrong amount or expired quote | Payment requirement |
Transfer not finalized | Settlement |
Payment accepted but result missing | Fulfillment |
Duplicate retry | Order and idempotency |
This separation helps operators avoid treating every problem as a wallet failure or a blockchain failure.
Add cross-layer recovery rules before launch:
Scenario | Safe response |
|---|---|
Identity registry unavailable | Use a documented low-risk fallback or pause; do not treat absence as trust |
Policy approves but signature fails | Mark authorization unused and retry only within its expiry |
Quote changes after approval | Require a new policy decision |
Payment verifies but settlement remains pending | Apply the merchant's delivery threshold and expose pending state |
Service fails after payment | Preserve proof, retry idempotently, credit, refund, or escalate |
Delivery succeeds but response is lost | Return the stored result on the same request key |
Reputation later changes | Do not rewrite historical authorization; apply new policy to future purchases |
Wallet or key is rotated | Preserve principal continuity without accepting old unauthorized signatures |
These rules allow the stack to degrade safely instead of converting unavailable infrastructure into repeated payment attempts.
Build the smallest useful stack
For a low-value API, the minimum may be a restricted wallet, x402 middleware, payment verification, and an idempotent result store. For agent-to-agent commerce or higher-value products, identity, reputation, order operations, and stronger approval controls become more important.
The correct stack is not the most automated one. It is the one that makes authorization, payment, settlement, and delivery legible to both the agent and the operator.
Preserve delegation across multi-agent workflows
A multi-agent workflow makes the distinction especially important. One agent may discover a service, another may hold the wallet, and a third may execute the paid tool. Preserve who authorized the action, which service was selected, what payment was made, and what result was returned. A shared wallet address alone does not answer those questions.
GOAT Network's combination of AgentKit, x402, ERC-8004-related identity concepts, and GOAT Flow is relevant to this modular view. It gives builders a way to think about agent actions, payment, trust, and merchant operations as connected layers while preserving their different jobs. Developers should validate the currently supported interfaces and deployment settings before implementation.
The useful design goal is not a fully autonomous buyer with no controls. It is a bounded agent that can act within an explicit policy and leave enough evidence for the merchant and operator to understand the transaction.
Use a task or workflow identifier across agents. The discovery agent can propose a service, the planning agent can reserve budget, the treasury agent can authorize payment, and the execution agent can consume the result. Each handoff should be signed, authenticated, or recorded according to risk. The final receipt should connect those roles without falsely claiming they are one identity.
Delegation also needs revocation and expiry. A purchasing capability granted for one task should not remain valid indefinitely, and a downstream agent should not be able to broaden the merchant, amount, or network chosen upstream.
Decide what evidence crosses each boundary
The wallet can provide an authorization decision or signed transaction. The identity layer can provide an agent identifier or reputation signal. x402 can provide a payment requirement and proof. Settlement can provide a transaction or finalized status. The merchant service can provide a delivery receipt.
Those artifacts should not be collapsed into one “trusted” flag. A service can be paid but not delivered. An identity can be registered but not reputable. A transaction can be signed but exceed a local spending policy. Keeping evidence separate lets each component make the decision it is qualified to make.
A shared transaction envelope can carry references rather than raw secrets. Useful fields include workflow ID, principal or agent ID, policy decision ID, resource and requirement IDs, payment reference, settlement reference, execution ID, delivery receipt, and current recovery state. Each component verifies the fields it trusts and appends its own evidence.
Version the envelope and schemas. Identity formats, wallet providers, payment schemes, and settlement networks can change independently. A versioned contract prevents one upgrade from making old receipts uninterpretable.
Apply progressive trust
Low-value or public resources may need only payment proof and a rate limit. Higher-value or sensitive services may require persistent identity, reputation, stronger authorization, or human approval. The stack should allow the merchant to increase requirements as risk increases.
GOAT Network's combination of AgentKit, x402, ERC-8004-related identity concepts, and GOAT Flow is relevant to this modular view. It gives builders a way to think about agent actions, payment, trust, and merchant operations as connected layers while preserving their different jobs. Developers should validate currently supported interfaces and deployment settings before implementation.
The stack should make upgrades and outages visible. If a wallet provider changes signing behavior, an identity registry is unavailable, a facilitator is delayed, or settlement is pending, the agent should receive a bounded state rather than an instruction to keep paying. Explicit degradation rules are more valuable than a claim that all layers are always available.
The result is a stack that can degrade safely without turning an infrastructure outage into an uncontrolled payment loop.
Implementation note
Map each transaction artifact before selecting providers. Write down what the wallet signs, what identity proves, what the payment requirement describes, what settlement confirms, and what fulfillment returns. Then test an unavailable identity registry, a pending transfer, an over-budget quote, and a service failure after payment.
The goal is not to eliminate every dependency. It is to prevent one missing dependency from being interpreted as permission to continue paying. Explicit states let the agent pause, ask for approval, or retry only when the policy allows it.
Final review checklist
Before opening the flow to more agents, review the offer, request, payment, and delivery records together. Confirm that the price or terms are current, the buyer policy can reject an out-of-scope action, the payment proof is bound to the right resource, and the service can return a result or a recoverable status. Confirm that retries do not create duplicate orders or duplicate charges.
Also review the human boundary. A merchant may require approval for an unusual quantity, a sensitive product, a high amount, a new network, or a delivery condition that the agent cannot validate. The agent should receive a clear escalation response, not a generic error. This is especially important when the merchant supports both humans and machines: the machine path should be automated where the business is comfortable, but it should not erase the controls that make the human path supportable.
Document the active configuration and revisit it when the product, payment scheme, or fulfillment system changes. A repository example or protocol capability is not proof that every option is enabled for the current merchant deployment.
Deployment patterns and provider boundaries
A lightweight paid API may use a scoped wallet, local policy engine, x402 middleware, hosted verification, and a merchant-owned result store. An agent marketplace may add persistent identity, reputation, order records, and dispute operations. An enterprise agent may keep keys in institutional custody while delegating only bounded signing requests to the runtime.
Components do not need to come from one provider. Modularity can reduce lock-in and let teams use specialized custody, identity, payment, and settlement services. Integration cost rises because the developer must normalize identifiers, availability states, and evidence across providers.
An integrated stack can simplify onboarding and operations, but the team should verify data export, credential separation, supported standards, and recovery during provider outage. The correct decision depends on which boundaries the organization is prepared to operate.
GOAT's public stack is most relevant where builders want agent-side actions, x402 payment capability, identity and reputation concepts, merchant operations, and onchain infrastructure to interoperate. That is a useful architectural fit, not proof that every application needs every GOAT component. Validate the current product interfaces and use only the layers that solve the defined responsibility.
Observability and governance
Trace one transaction from service discovery through policy, signature, payment verification, execution, delivery, and settlement. Use correlation IDs that allow engineers, support, security, and finance to inspect the same workflow without sharing unrestricted credentials.
Monitor denial reasons, authorization latency, payment verification latency, failed execution after payment, duplicate retries, pending settlement, refunds, identity lookup failures, and manual approvals. A rising rate of policy denial may indicate unsafe agent behavior or a stale pricing integration; a rise in paid-but-undelivered events points to service execution rather than the wallet.
Governance should define who can change budgets, allowlists, identity trust sources, accepted payment routes, and settlement thresholds. Changes need versioning and audit history. Emergency controls should pause new authorization while preserving retrieval and reconciliation for already completed transactions.
FAQ
Do agents need blockchain identity before paying?
Not for every low-value request. A payment-gated resource may require only payment proof, while privileged services can require persistent identity or reputation.
Is a wallet enough to represent an agent?
No. A wallet proves control of a signing capability, not necessarily the operator, purpose, reputation, or permission boundary.
Where does x402 fit in the stack?
x402 is the machine-readable payment layer for HTTP resources. It works alongside wallets, policy, identity, merchant operations, and settlement rather than replacing them.
Must all four layers come from one provider?
No. They can be composed if identifiers, evidence, failure states, and authority boundaries are compatible. Integrated products may reduce operational work, while modular stacks provide more control and replacement options.
Does a successful onchain transaction mean the service was delivered?
No. Settlement proves a financial event under the chosen rail. The merchant still needs execution and delivery evidence linked to the paid requirement.