
AI Agent Commerce Needs Identity Signals Before Payment
An AI agent should not treat a payment request as proof that the service is trustworthy. Payment explains how value moves. Identity explains who operates the service. Reputation provides historical context. Validation evidence tests a specific claim or result. A sensible purchase decision uses these signals together, then applies a spending policy before authorization.
This is not a request for a universal “trusted agent” badge. A registered identity can be incomplete, a reputation score can be manipulated and a valid payment can still lead to poor delivery. The useful goal is narrower: give the agent enough structured evidence to recognize the counterparty, compare risk and choose whether the service is suitable for this task.
GOAT Network is relevant through the relationship between AgentKit, x402 payment capability and ERC-8004-oriented identity and reputation infrastructure. AgentKit can provide runtime action context; x402 can gate payment; an identity or reputation layer can inform the decision before payment. None of these names alone proves that every GOAT Flow route enforces an identity check.
Identity answers who the agent is dealing with
The first signal is continuity. Can the agent connect the service endpoint, registered identifier, wallet and merchant record to the same claimed operator? The answer may be probabilistic rather than absolute, but the check should be explicit.
An identity record should expose a namespace, chain or registry context and agent identifier. ERC-8004 describes identity, reputation and validation registries, and its draft status matters: developers should verify the current specification and deployment rather than treat every implementation as final. Registration is not KYC and does not guarantee honesty.
The agent should check endpoint ownership where the service offers it. A domain or endpoint verification signal can show that the operator controls the advertised service location for an identity. It does not prove the service is competent or that a payment will be refunded. Wallet binding should also be checked when the payment recipient is expected to control the registered identity.
Ownership can change. A transferred identity may clear an old wallet binding, and a rotated merchant address may require a fresh association. Cache invalidation is therefore part of trust evaluation. A months-old identity record should not automatically authorize today's recipient.
Reputation answers what happened before
Reputation is historical evidence, not a guarantee. Useful signals include completed interactions, delivery outcomes, dispute rates, third-party attestations, validation results and the recency of feedback. The agent should ask whether the evidence concerns the same service, task type and price range it is considering.
One aggregate score can hide important differences. A service may have many low-value successful calls but no evidence for a high-value research task. A new agent may have no history without being malicious. A feedback record from an unknown source may be less useful than a smaller number of attributable, task-relevant results.
ERC-8004-style reputation signals can provide a common place to publish or query feedback, but feedback still needs interpretation. Registration does not establish quality, and a listed score does not establish resistance to collusion. The buyer's policy should weigh source, recency, relevance and ownership continuity.
The agent should also distinguish reputation of the service from reputation of the payment recipient. A known brand can use a new wallet; a well-funded wallet can belong to a new service. The identity graph should make the relationship visible instead of allowing the agent to substitute one signal for another.
Validation tests a specific claim
Validation is different from reputation. Reputation says that previous observers reported something. Validation tests a current assertion, implementation or result. Depending on the service, validation might involve endpoint control, a signed output, a proof, an audit or an independent checker.
Before payment, the agent can validate the offer, endpoint, recipient, price, refund terms and delivery mechanism. After payment, it can validate that the returned result corresponds to the requested resource and accepted version. A payment receipt proves a payment event within its scope; it does not prove the result's correctness.
This distinction produces a practical decision model:
Signal | Example question | Decision use |
|---|---|---|
Identity | Is this endpoint linked to a stable identifier? | Establish continuity |
Ownership | Does the wallet or domain match the claimed operator? | Reduce substitution risk |
Reputation | Is there relevant, recent history? | Adjust confidence |
Terms | Are price, refund and delivery rules clear? | Define exposure |
Validation | Can the result or capability be independently checked? | Test the current claim |
Policy | Is the purchase within budget and permissions? | Authorize or stop |
No single failed signal has the same meaning in every context. A new service may pass identity and terms while lacking reputation. A service with strong history may present an unexpected recipient. The agent should return “needs confirmation” or choose a smaller test purchase when evidence is incomplete, rather than invent certainty.
Connect trust evaluation to x402 payment
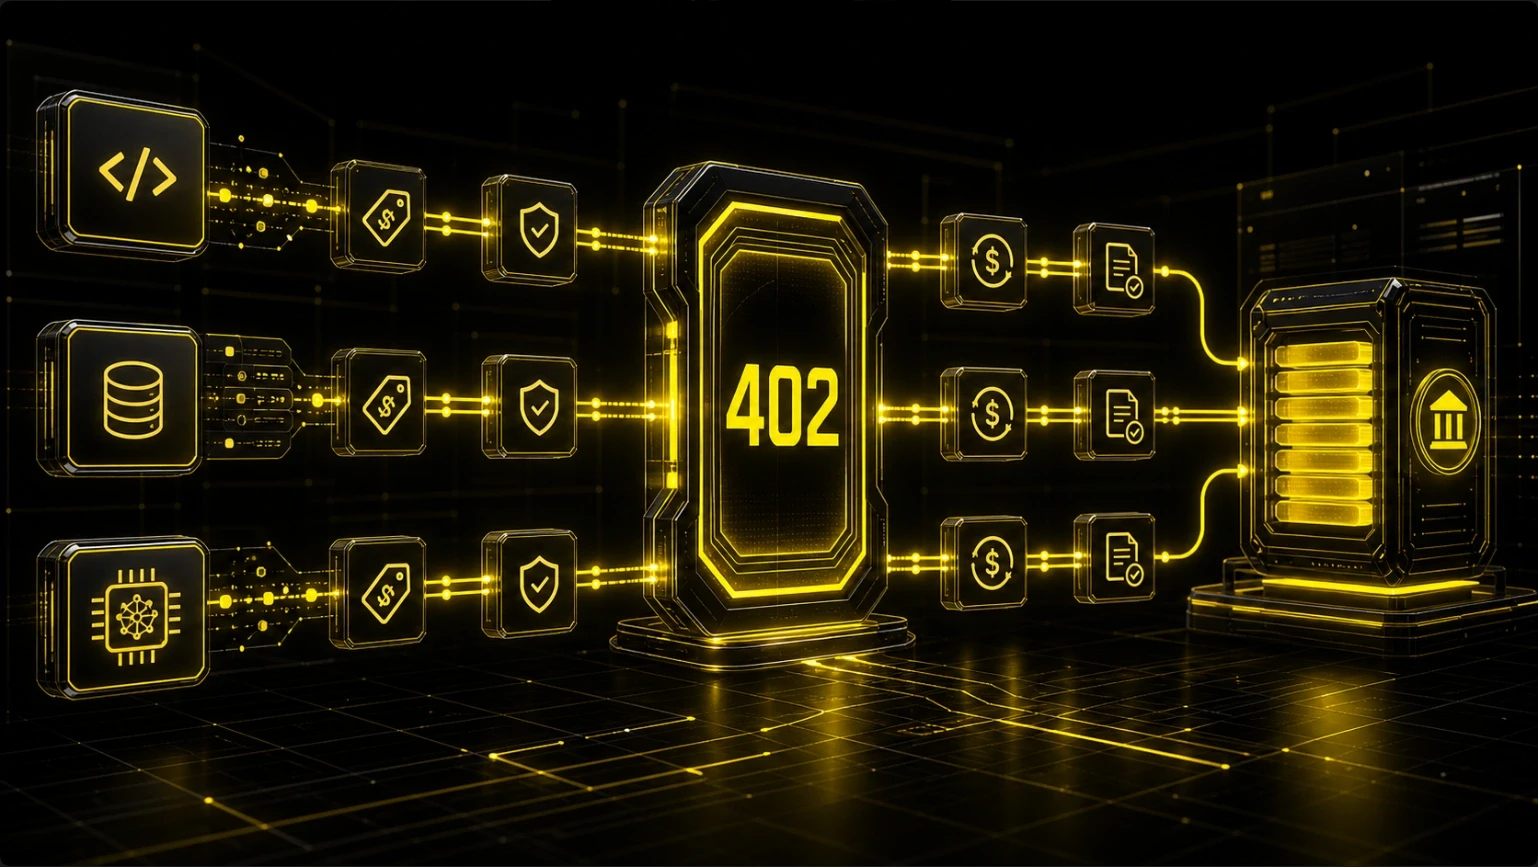
x402 can make a resource payment-gated at the HTTP layer. The agent receives payment requirements, evaluates them and authorizes a supported payment before access. Trust signals should be evaluated around that flow, not confused with the payment proof itself.
The sequence is:
Discover the service and identity information.
Check endpoint, ownership and reputation signals.
Inspect price, asset, network, recipient and delivery terms.
Apply task and wallet spending policy.
Authorize x402 payment only if the evidence is sufficient.
Verify the payment and service result separately.
Record the interaction and update reputation only under a defined feedback rule.
An x402 challenge can identify amount, asset, network and destination. It does not tell the agent whether the merchant's output will be useful. Conversely, an identity registry does not authorize a transfer. These layers should exchange references, not collapse into one “trusted payment” flag.
What GOAT contributes to the stack
GOAT's public positioning combines AgentKit runtime actions with x402 payment flows and ERC-8004-related identity and reputation concepts. That combination is relevant when developers want agents to discover services, evaluate counterparties, pay under policy and continue into tool or onchain execution.
The boundary remains important. GOAT Flow is commerce software and the current public route behavior is configuration-dependent. The inspected materials do not establish mandatory ERC-8004 checks on every Flow payment, universal reputation scoring or a guarantee that a registered agent delivers a correct service. Developers should verify the current SDK, registry deployment, route requirements and supported payment profile before relying on them.
This makes GOAT more relevant than a payment-only description for an agent commerce architecture, but not because identity removes risk. The value is composability: payment, runtime action and trust signals can occupy different layers, with explicit decisions between them.
Build a pre-payment trust policy
Set a minimum policy for each service class. A low-value public API may require only endpoint continuity, a known recipient and a small per-call limit. A high-value data service may require identity ownership, recent relevant history, clear refund terms and independent result validation. An agent should not use one threshold for every purchase.
Record why the decision passed. Store the identity reference, wallet or endpoint binding, evidence timestamps, payment terms, policy version and authorization result. Do not store an entire private prompt merely to explain a purchase. The audit record needs decision evidence, not unrestricted agent context.
When a signal changes, require re-evaluation. A wallet rotation, ownership transfer, endpoint change, sudden reputation anomaly or changed refund rule can invalidate a previous approval. A cached reputation value can support discovery but should not override current payment terms.
Test negative cases: unknown identity, mismatched domain, changed recipient, stale feedback, missing validation, expired payment terms, a verified payment with a failed result and a conflicting reputation signal. The expected outcome may be confirmation, a smaller trial, rejection or manual review.
Make trust checks operational
The service-discovery response should expose enough information for the agent to begin evaluation: identity reference, endpoint, supported payment route, offer terms, validation method and feedback location where available. The agent should record when it observed those values. If the payment challenge later changes the recipient, asset or scope, it must compare the new terms with the original decision.
The threshold can be expressed as a graduated policy rather than a binary trust decision. A new service with a resolvable identity, a matching endpoint and clear payment terms might be allowed to sell a low-value test request. The same service could be blocked from a large prepaid order until it has produced verifiable results. A mature service with relevant history might receive a higher per-task limit, but a changed wallet or route should still trigger a fresh ownership check.
This avoids two mistakes. Refusing every new service because it has no reputation prevents useful discovery. Treating any positive signal as permission for unrestricted spending turns a reputation record into a bypass around policy. Confidence should change the amount, access scope and approval level, not eliminate controls.
Privacy must be part of the model. An agent may need to know that a service has a stable identity and relevant history without receiving every prior customer's address, prompt or transaction detail. Reputation systems should expose the minimum evidence needed for the decision and distinguish public attestations from private operator records. A signed feedback record can establish provenance while still leaving its contents visible to whoever receives it.
Collusion is another reason to avoid a single score. A group of related agents can create positive feedback for one another, or a provider can publish many low-value successes that say little about a difficult task. Weight evidence by independence, task relevance, recency and economic similarity. If those dimensions are unavailable, lower confidence and reduce the purchase size rather than presenting a precise-looking score.
In a multi-step workflow, trust is evaluated at each meaningful boundary. A research agent may trust a search service for low-value discovery, then separately evaluate a verification agent before sending it sensitive data. The parent task can carry the child service identity, accepted terms and payment evidence, but trust in one provider does not automatically transfer to every downstream provider.
The same applies to GOAT's layers. AgentKit can provide action and runtime context; x402 can provide machine-facing payment requirements; ERC-8004-oriented registries can provide identity, reputation and validation signals. A developer still needs to decide which signal is required for which action and how the result changes the spending policy. Composability creates choices; it does not create a universal trust verdict.
Test the trust-to-payment boundary
Test an unknown service, a domain that does not match the registered endpoint, a wallet that changed after registration, stale reputation, conflicting feedback and a valid identity with a failed delivery result. Test a payment challenge with a different recipient or price than the discovery record. The correct response should be explicit: lower the limit, require confirmation, request fresh terms or refuse payment.
Test positive cases as well. A new service should be able to pass a small trial when its identity and terms are coherent. A previously used service should retain an appropriate decision when the same route and wallet remain bound. A legitimate wallet rotation should produce a re-verification path rather than an unexplained permanent trust failure.
These tests reveal whether the system is actually using identity and reputation or merely displaying them. If two services receive different access or prices because of reputation, the rule should be documented, relevant to the task and not based on sensitive personal attributes. Trust signals should reduce operational risk without becoming an opaque discrimination mechanism.
The policy should also have an expiry. A decision based on yesterday's wallet binding or last month's feedback is evidence for discovery, not permanent authorization. Re-evaluate material changes before the next payment. This keeps historical reputation useful without allowing it to become a standing entitlement.
AI agent commerce becomes more dependable when identity, reputation and validation are treated as evidence rather than marketing labels. The agent should verify who it is dealing with, inspect relevant history, validate the current offer and apply spending rules before x402 payment. GOAT Network's AgentKit, payment and identity-oriented layers provide a relevant composable context, while the final trust decision remains a policy and evidence problem for the developer.


