
An x402 integration handles payment for a request. A selling platform must also own order operations, delivery handoffs and recovery. Here is the distinction.
An x402 payment integration gives a service a way to request, verify and settle payment through an HTTP interaction. A platform for selling to AI agents takes on additional merchant work: representing the purchase, tracking its state, connecting payment to fulfillment, and making unresolved transactions recoverable. The difference is the responsibility each system owns, not whether both can accept a payment.
That distinction does not make a platform compulsory. If your API sells a single data response and your application already handles delivery, retries and records, an x402 integration may be enough. Payment verification alone becomes inadequate when the seller treats it as proof that the entire commercial obligation is complete.
For a merchant comparing these options, the decisive question is what happens after an interruption. Can your team determine what the agent bought, whether payment succeeded, what was delivered, and what is still owed? A working payment demo answers only part of that question.
The paid request is a useful unit, not the whole business
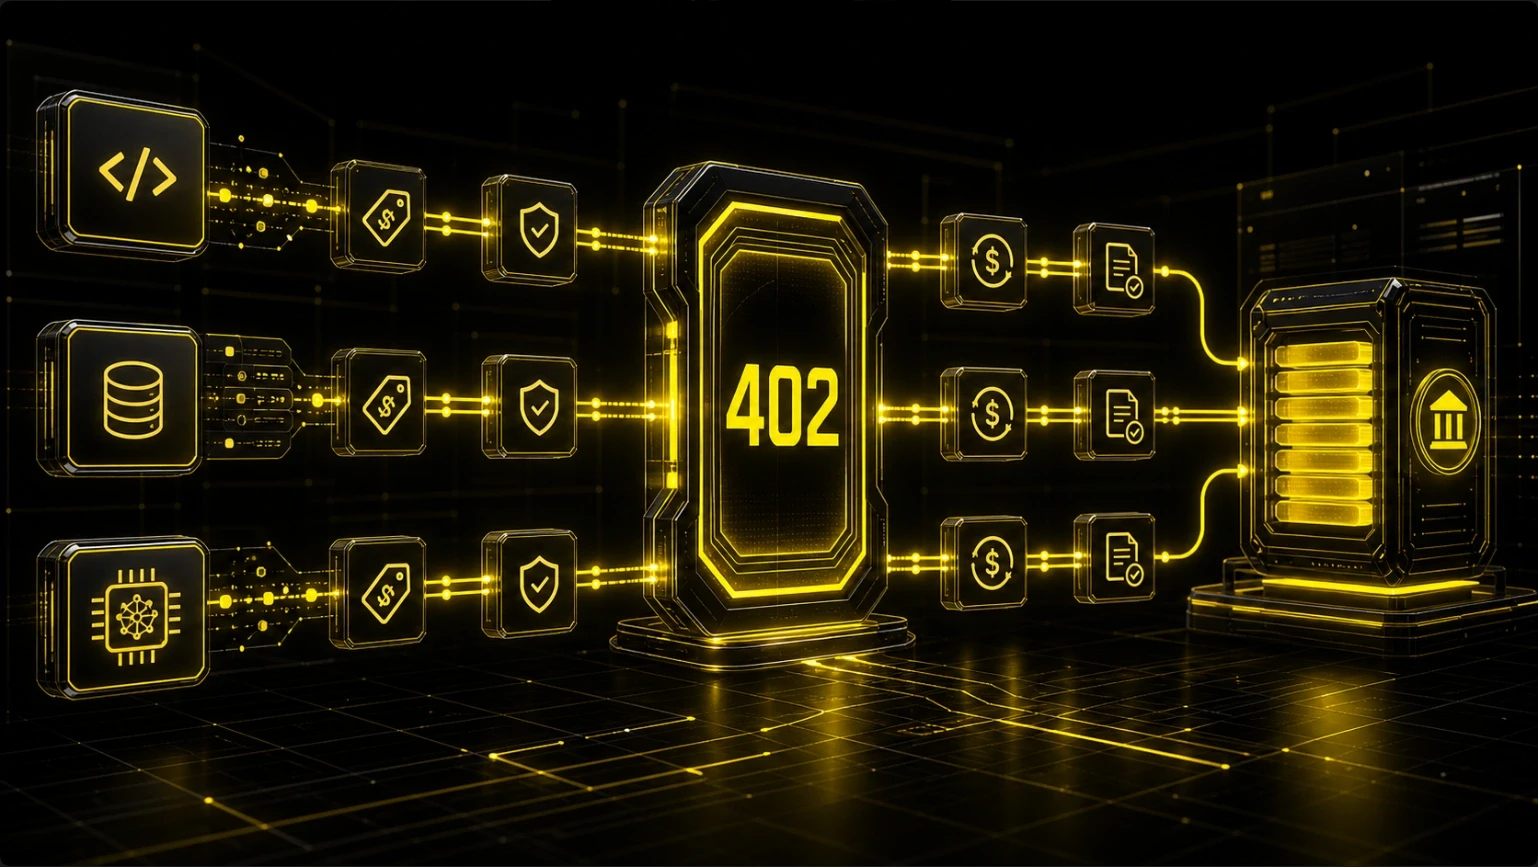
x402 makes a paid HTTP resource accessible to software that understands its payment requirements. A client requests a resource, receives a payment challenge, constructs the appropriate payment payload and continues the exchange. The service can verify that payload and obtain the payment outcome without sending the buyer through a conventional account-and-checkout journey.
The protocol already communicates meaningful transaction information. In x402 V2, PAYMENT-REQUIRED carries the requirements, PAYMENT-SIGNATURE carries the client's payment payload, and PAYMENT-RESPONSE carries the settlement response. The timing of onchain funds movement depends on the payment scheme; a valid authorization should not be described as confirmed settlement in every flow. These are explicit distinctions in the x402 HTTP payment documentation.
Verification asks whether the payment payload meets the declared requirements. Settlement concerns executing or redeeming the payment under the selected scheme. Fulfillment is the seller providing the purchased resource. A positive answer to the first question does not, by itself, establish the other two.
For a simple service, these responsibilities can fit closely together. Consider a hypothetical API returning a current temperature reading. The seller can produce the response within the paid interaction, return it, and retain whatever evidence its service needs for retries and support. If the surrounding application already owns those jobs, adding a separate commerce product may duplicate existing capabilities.
The protocol does not forbid that complete exchange. Nor does an optional facilitator have to become the seller's business system. The official facilitator documentation assigns it payment verification and settlement responsibilities, while the resource server decides whether to fulfill the request. Its documented recovery handling also recognizes that a pending settlement is not necessarily a failed payment.
The missing commerce layer, therefore, is not a field that must be added to every x402 message. It is the merchant responsibility left unowned when a team adds payment handling but does not connect it to the rest of the sale. That work can live in the merchant's application, a platform, or a deliberate combination of both.
Follow the obligation when the connection disappears
Take a more demanding example: an agent buys a research report that requires a background job. This is a hypothetical design example, not a reported customer transaction. The buyer expects a completed report, rather than merely permission to start computation.
The seller accepts the requested report specification and price. Payment succeeds. A worker begins generating the output. Then the agent's connection disappears before it receives a usable result.
At that point, the payment system may know exactly what happened to the money. It does not necessarily know whether the worker finished, whether the file was stored, whether the correct buyer can retrieve it, or whether the agent received a link that still works. Those questions concern different records and different owners.
The first necessary connection is between the purchase and the accepted work. The seller needs to preserve enough context to distinguish this report from another request: the requested output, the accepted commercial terms and a stable purchase reference. Otherwise, a support operator can find a payment but cannot determine what it paid for. A wallet address and an amount are not a complete description of a report obligation.
Next comes the connection between payment and the fulfillment attempt. The seller must know whether the background job was started, whether it is still running and where its result will be recorded. A timeout on the buyer's HTTP connection should not erase the identity of work already underway. Without that association, retrying the purchase can create another job even if the first payment and first job remain valid.
Delivery needs its own evidence. A stored report, a retrieval entitlement and a successful response are different observations. For some products, making the output available to the authorized buyer is the agreed completion condition. Others require an acknowledgement or a further action. The merchant must define that condition rather than borrowing a payment status and calling it delivered.
Now let the agent return and repeat its request. A recoverable sale lets the server identify the original purchase and return its current outcome: still processing, ready to retrieve, or unable to complete under the seller's stated remedy. A payment-only integration that treats every new request as a new purchase may charge again or commission duplicate work. Which failure occurs depends on the application, not on the agent's ability to pay.
There is also a late-payment branch. Suppose an offer or order expires while the transfer is still being resolved. If funds subsequently arrive, the seller faces a commercial exception: honor the original terms, decline new work while arranging a remedy, or apply another previously disclosed rule. An expired application record cannot make a received transfer disappear. Conversely, a received transfer cannot make an unavailable product fulfillable.
None of this requires a universal order-state vocabulary. It requires durable associations and explicit owners. The useful unit for an operator is the purchase history connecting agreed work, payment evidence, fulfillment attempts and any outstanding obligation. Separate systems can maintain that history, but somebody must make their transitions consistent enough to recover the sale.
Extensions help, but somebody must operate them
It would be inaccurate to compare a sophisticated selling platform with an artificially bare version of x402. The ecosystem includes facilities that address parts of the lifecycle problem.
The payment-identifier extension supports a logical payment ID and seller-side response caching so a retry can avoid processing the same payment again. The documentation describes advertising extension support, generating the identifier at the logical request level and retaining it for operations that must survive restarts. These are useful building blocks, not a reason to disregard protocol integrations.
For the report seller, however, deduplicating payment is not identical to deduplicating work. The worker queue needs to associate the purchase with the original job. The output store needs to preserve the result. The access handler needs to retrieve that result for the entitled buyer. If one of those components forgets the relationship, a correctly deduplicated payment can still accompany a duplicate report job or an inaccessible report.
The lifetime of recovery also matters. An HTTP response cache may satisfy short network retries, while a report promised for later delivery needs a durable purchase record over a longer period. The team must choose retention and storage to match its obligation. Calling the feature idempotency does not establish that every external side effect or every application replica shares the same protection.
Discovery has a similar boundary. x402 Bazaar provides a machine-readable catalog for participating payable API endpoints and MCP tools. Its documentation describes an evolving discovery layer, with support determined by the participating facilitator and route configuration. A merchant should not assume that adding an x402 response automatically registers a complete selling presence everywhere.
Discovery can help an agent find the report service. It does not establish whether a particular report was completed or which operator must resolve a late transfer. A listing and an order history answer different questions.
These extensions make the integration-versus-platform comparison more practical. A merchant can assemble protocol components and keep operational control, provided it supplies the business-state connections and operates their persistence. A platform can package some of that work. Neither an extension name nor a platform label proves the end-to-end result without examining the deployed implementation.
An agent that can sign is not an agent allowed to buy
The buyer adds another responsibility boundary. A seller receiving a valid payment is not evidence that the agent respected its user's purchasing mandate.
A wallet signer provides a technical capability: it can authorize a transaction or sign payment data. A purchasing policy determines when that capability may be used. The policy might restrict recipients, cap one purchase, reserve a total budget across concurrent tasks, or require confirmation for a particular action. Those controls need an enforcement location before signing or broadcasting, with state that remains correct across retries and concurrent purchases.
Consider the report agent making several individually small purchases. Each payment can satisfy the merchant's requirements while their aggregate exceeds the user's intended budget. Checking the next request in isolation cannot prevent that if the budget is shared across tasks. The buyer needs a mechanism that accounts for existing spending and outstanding commitments, not simply a wallet with enough funds.
GOAT AgentKit belongs to the action and runtime side of this distinction. It provides tooling for agent actions, including wallet and payment operations, rather than automatically taking ownership of the merchant's delivery obligation. Even its control claims need to be scoped to the implementation being used.
The pinned AgentKit PolicyEngine implementation checks allowed networks, action network support, write enablement, risk level and confirmation requirements. That class does not implement built-in aggregate-budget accounting or amount and recipient limits. Applications may add controls elsewhere, but a buyer should not infer those protections from the presence of a PolicyEngine or a functioning signer.
Identity is a separate concern again. ERC-8004, currently a Draft, proposes identity, reputation and validation registries and explicitly leaves payments outside its scope. Identifying an agent or examining feedback can inform a trust decision; it does not prove that a purchase was authorized under a budget, that payment settled, or that the report was delivered.
For the merchant, this means a commerce platform cannot be evaluated as a substitute for all buyer-side controls. For the buyer, a successful sale does not retrospectively validate the policy that permitted it. Both sides need a clear owner for their part of the exchange.
Look for the order operation, not a second payment rail
The positive case for a selling platform is easiest to assess through operations that a merchant would otherwise have to build. GOAT Flow provides a concrete example, with important limits.
GOAT Flow is the commerce product; x402 is a broader HTTP payment protocol, and AgentKit is agent action/runtime tooling. Flow's Checkout, QuickPay and API Payments address different merchant entry paths. The distinguishing question is what common transaction work remains available after a buyer uses one of those paths.
In the current public DIRECT merchant path, the payer transfers an ERC-20 token to the merchant-configured receiving address. Buyer funds do not pass through Flow in this path; Flow creates and tracks the order record around the direct transfer. This is not escrow followed by a platform payout. An ERC-20 transfer on an EVM network is also not a Bitcoin L1 transfer, even when the commerce product is associated with GOAT Network.
The Flow merchant guide documents order identifiers, payment information and lifecycle statuses. It also describes reconciliation views for matched payments, unpaid orders and late payments, with chain/date filtering and CSV export. These are seller operations around payment evidence: they help distinguish a normal completed payment from an exception an operator must investigate.
Return to the hypothetical report. A payment matched to an order lets the merchant connect the transfer to its accepted purchase reference. A late-payment view gives the operator a way to find transfers that arrived after expiry rather than hiding them among ordinary successful payments. Reconciliation is valuable because the seller's next action depends on the relationship between the money and the obligation, not solely on the presence of an onchain transaction.
That contribution still has a boundary. The merchant guide instructs sellers to obtain trusted backend status or authenticate the deployment's webhook and verify the relevant order/payment details before fulfillment. It also requires idempotent fulfillment. A browser success callback is a user-interface signal, not authority to deliver the report or ship twice after a notification retry.
Flow's payment record is not proof that the merchant's background job succeeded. The merchant still owns generating the report, storing the output, granting the right access and deciding what happens when delivery fails. A platform can supply a useful handoff without becoming the producer or guarantor of every good sold through it.
The evidence itself needs careful interpretation. The order proof's historical signature field is an unsigned Keccak256 digest, not a cryptographic signature attesting to fulfillment. It should not be treated as equivalent to the signed receipt used by Flow's separate MPP profile. Likewise, a portal column labelled Payout Tx does not establish an escrow or later payout process for DIRECT transfers.
This is the kind of distinction to investigate when comparing GOAT Flow's merchant-facing surfaces with a standalone integration. The platform's value lies in documented order and reconciliation work, while the merchant retains explicit delivery responsibilities. Supported assets, amount limits and webhook behavior must be confirmed for the actual merchant environment; a public product description is not a universal capability entitlement.
A profile name is not a compatibility result
Protocol support is another place where sellers can accidentally buy a broader promise than the evidence provides. A label such as MPP does not establish that any MPP client can use every endpoint bearing that label.
MPP, the Machine Payments Protocol, is an independent protocol. GOAT Flow's current MPP integration is a specific profile: the buyer requests a challenge through a JSON endpoint, sends the instructed ERC-20 transfer directly to the recipient, submits the transaction for verification and receives a signed Payment-Receipt. The buyer then presents that receipt to the protected merchant resource.
The Flow MPP integration guide identifies those JSON endpoints and the three-segment signed receipt as GOAT-specific contracts, rather than generic MPP's protected-resource Challenge/Credential exchange. It reports no published interoperability result with official MPP SDKs. A seller evaluating a different client needs adapter and conformance evidence, not an inference from the shared name.
The resource server remains part of the trust boundary. It must validate the receipt's signature, merchant audience, route/request binding, expiry and intended replay policy. Where the receipt is single-use and several replicas serve the route, consumption needs shared atomic state. The server must reject a receipt presented for an unrelated route; successful payment verification still does not make an unavailable report appear.
For the hypothetical seller, this creates two separate acceptance questions. Can the intended agent client execute this payment profile? Can the resource server use the resulting evidence to authorize the correct report retrieval? Answering only the first leaves the sale incomplete from the buyer's perspective.
Keep deployment availability beside the claim as well. Flow's MPP profile needs an enabled environment and merchant capability; accepted chains and tokens come from active configuration. Generic x402 support, a GOAT repository module and an enabled Flow paid route are different pieces of evidence. They should not be collapsed into a claim of universal interoperability.
Buying operations has a cost
Once the responsibilities are visible, the decision is less ideological than protocol versus platform language suggests.
An integration is attractive when the merchant already has the necessary commercial system. A team with durable purchase records, a reliable job queue, retrieval authorization, reconciliation and exception handling may need only a payment-aware boundary around those components. It can choose compatible schemes and extensions, retain control over the product model and avoid duplicating operations in another service.
That choice does not eliminate commerce work. It assigns the work to the merchant. The team owns the connection between a payment identifier and its purchase, handles inconsistent outcomes and keeps recovery functioning as its application changes. If the only evidence of readiness is a middleware demonstration returning a resource after payment, the operational decision has not yet been made.
An operated commerce platform becomes more compelling when those functions are missing, scattered across scripts or needed by non-developer operators. A consistent order view and an explicit late-payment workflow can be more valuable than writing another payment parser. Supporting several selling entry paths may also justify a common operational record instead of separate transaction logic for each path.
The tradeoff is dependence on the service's actual behavior. Merchants need to understand its configuration model, status meanings, API availability, authentication boundary and recovery options. They must know which evidence can be exported and how an unresolved order is handled when notifications or access to the service fail. Delegating an operation changes its owner; it does not remove the need to evaluate that owner.
There is no supported reason to assume a platform is always cheaper or faster to launch. That depends on the merchant's existing systems and the enabled product configuration. Nor is a minimal integration inherently less reliable. Reliability follows from the implemented state, storage and recovery paths, not from the category name.
For the temperature API, retaining a minimal integration may be the clearest choice. For the delayed-report seller, a platform may reduce payment/order operating work while the application continues to own report production and delivery. The reasonable decision is to delegate the responsibilities the platform demonstrably manages and retain an explicit owner for the rest.
Ask for an interrupted sale, not another happy-path demo
The next evaluation should demonstrate recovery, whether the candidate is your own integration or an operated product. Treat this as a proposed acceptance exercise, not a claim that any particular deployment has passed it.
Use one identifiable purchase. Interrupt the buyer's response after payment may have succeeded, then resume with the same logical purchase reference. Ask the system to show whether payment is confirmed or still unresolved, whether work was started, and where the result can be retrieved. A fresh payment should not be the automatic response to uncertainty about an existing transfer.
Repeat the request while the report job is still running. The useful outcome is one understood commercial obligation with controlled work and delivery attempts, not merely a verifier returning success twice. If the system's payment protection stops at a local cache, find out which component preserves the purchase-to-job relationship after a restart or on another replica.
Then introduce the expiry branch. Show what the operator sees when funds arrive late and who decides whether the original work can still be honored. The exercise should reveal the policy and the responsible party. Do not accept an automatic-refund claim unless that exact flow is documented and enabled; direct receipt of tokens does not create a universal remedy.
Finally, separate the records. Payment evidence should identify the accepted transaction. Delivery evidence should identify the output or other agreed completion condition. Buyer-side authorization should show the relevant spending decision. If an evaluator must infer one from another, the architecture still has an unowned responsibility.
A simple synchronous service can satisfy this evaluation with modest application logic. A more complex seller may benefit from platform order operations, as Flow's documented model illustrates, while retaining responsibility for its own output. Choose the arrangement that can reconstruct the purchase and resolve what is owed after interruption. That is a materially stronger qualification for selling to AI agents than the ability to verify payment alone.