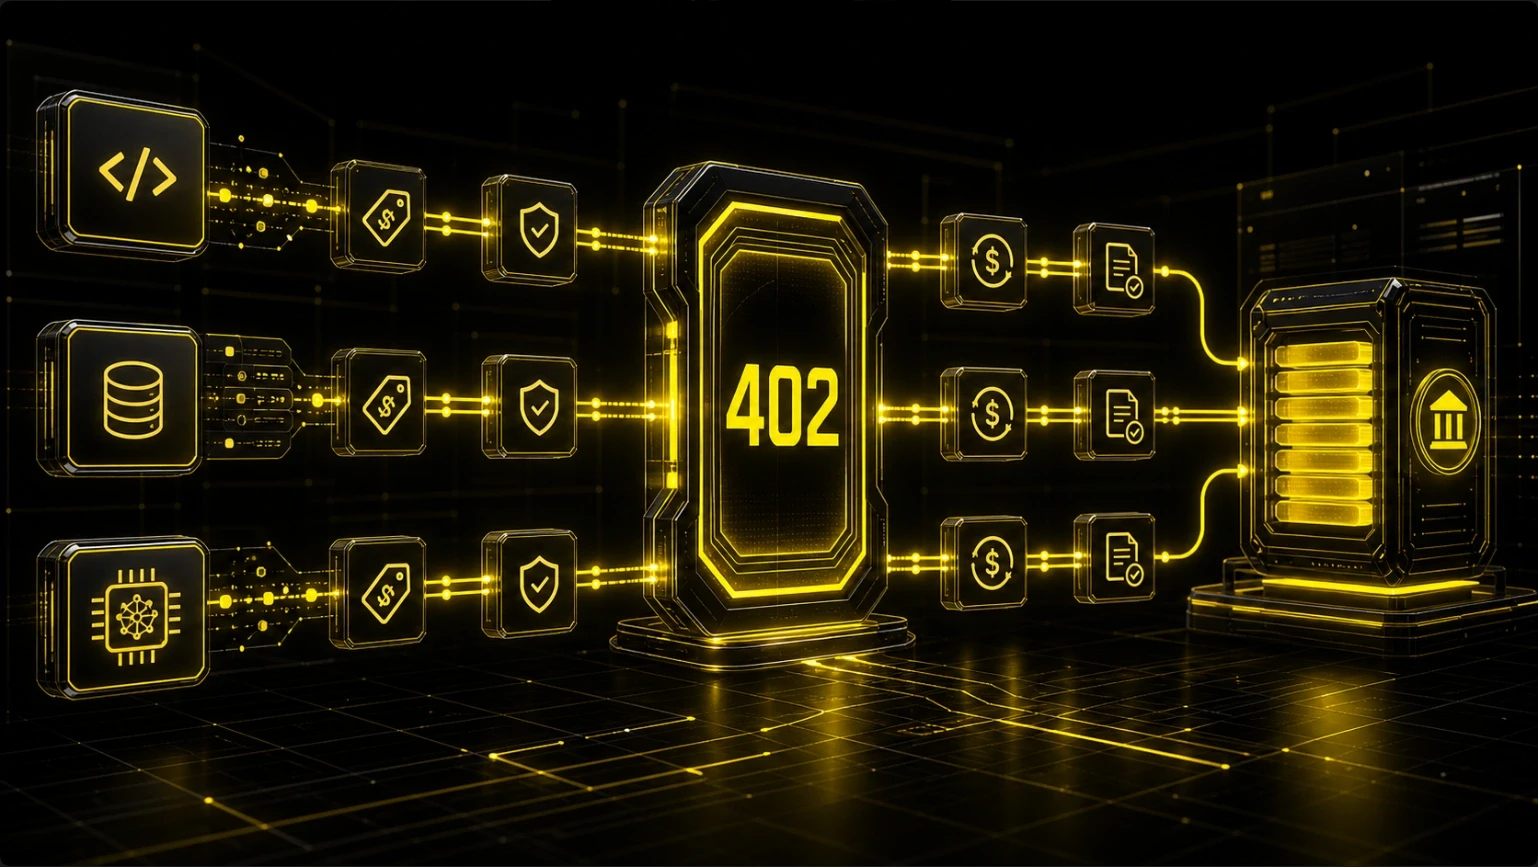
Payment settlement does not prove delivery. Map the x402 infrastructure that binds agent payments to API responses, content rights, product orders, and recovery.
The x402 infrastructure needed to sell APIs, digital content, and products to AI agents is larger than a payment middleware package. A complete merchant system must describe the resource, quote authoritative terms, verify payment, grant the correct access, record delivery, and recover when payment and fulfillment do not finish together.
The decisive design artifact is a payment-to-delivery contract. It answers five questions for every purchase:
What exactly did the agent agree to buy?
Which payment evidence satisfies that offer?
What access or product does the merchant owe?
Which record proves that delivery happened?
What happens if the same request is retried or one stage fails?
That contract differs by resource. A paid API call normally authorizes one execution. A report may create a reusable entitlement. A fixed-price product creates an order that can outlive the HTTP request. The same payment protocol can support all three, but the surrounding commerce infrastructure cannot treat them as the same transaction.
The Payment Protocol Is One Boundary, Not the Whole Store
x402 is an open payment standard for charging for APIs and content over HTTP. In a typical flow, a client requests a protected resource, the resource server returns 402 Payment Required with acceptable payment terms, the client submits a payment payload, and the server verifies or settles it before returning the resource.
In x402 V2, three headers make the payment exchange explicit:
PAYMENT-REQUIREDcommunicates the available payment requirements.PAYMENT-SIGNATUREcarries the buyer's payment payload when the request is retried.PAYMENT-RESPONSEreports the result of settlement.
Those headers establish a strong payment boundary. They can communicate price, network, scheme, destination, authorization, and settlement outcome in a machine-readable exchange. They do not, by themselves, define a SKU, a software license, an inventory reservation, a report's access period, a refund policy, or proof that a model generated a usable answer.
This distinction matters because a merchant can receive a valid payment and still fail to deliver. The model server can time out. A signed download URL can expire before the agent uses it. A product order can be recorded twice. A webhook can arrive after the buyer has retried. Payment integrity is necessary, but monetization is complete only when it is joined to delivery integrity.
For that reason, the resource server should not ask only, “Is this payment valid?” It should also ask, “Which offer and execution does this payment authorize, has that execution already happened, and what does the buyer receive now?”
Six Boundaries Turn a Paid Resource Into a Sellable Resource
A useful x402 architecture assigns authority rather than collecting features. Six boundaries cover the merchant journey from discovery through recovery.
Boundary | Authoritative question | Typical record | What it must not be confused with |
|---|---|---|---|
Offer | What is being sold, at what price, under which terms? | Product, route, quote, or checkout session | A marketing description |
Discovery | How can an agent find and parse the offer? | Manifest, tool schema, route metadata, or product page | Final payment terms |
Payment | Which authorization or settlement satisfies the offer? | Payment requirement, payload, receipt, transaction, or facilitator result | Proof of service delivery |
Entitlement | What may this buyer access after payment? | Request grant, license, token, account right, or signed URL | The payment transaction itself |
Delivery | What was actually returned or performed? | Response digest, artifact ID, fulfillment event, or completion status | A browser success message |
Operations | How are exceptions, retries, refunds, and accounting resolved? | Order ledger, webhook log, reconciliation record, refund case, audit trail | A dashboard total without source events |
The offer boundary should bind price to a resource version. An agent choosing a $0.03 endpoint needs to know whether that price covers one successful response, one attempted execution, a maximum payload size, or a result that meets a defined condition. A fixed-price dataset needs a product identifier and version, not merely a payment destination.
Discovery is deliberately weaker than authority. A manifest can help an agent find a route, accepted asset, or product. It may be cached or become stale. Once a server returns a current challenge or creates a signed checkout session, those terms should supersede descriptive metadata. Otherwise an agent may pay an old price, choose a disabled asset, or send funds to terms the merchant no longer honors.
The entitlement and delivery boundaries are where business logic enters. x402 can gate the resource, but the merchant defines whether access is single-use, time-limited, transferable, revocable, or repeatable. The merchant also decides what counts as successful delivery. These policies should be machine-readable where possible and recorded even when the buyer has no conventional account.
Finally, the operations boundary closes the loop. Every payment needs identifiers that let the merchant correlate the offer, agent request, payment attempt, settlement result, fulfillment action, and exception. Without that chain, support and reconciliation become guesswork.
API Delivery Is Request-Scoped
For a paid API, the commercial unit is usually one authorized request. Consider a market-data endpoint that charges an agent for a current price snapshot. An operational contract might look like this:
The normalized request matters. If the price varies by symbol count, freshness, model size, or computation, the payment must authorize the actual requested workload rather than only the URL. The quote should expire, and the resource server should reject a payment payload that is valid in isolation but bound to a different amount, network, destination, route, or request identity.
One idempotency identifier should follow the operation across payment and execution. If the agent loses the HTTP response after the server executes the call, a retry should return the stored result or a stable status, not charge and execute again. This is particularly important for expensive model inference, write operations, and tools that trigger downstream actions.
Delivery evidence for an API can be compact. It may include the request ID, resource version, execution status, response digest, completion timestamp, and payment or receipt identifier. The merchant does not need to put private response data onchain. It needs enough durable evidence to answer whether the paid execution occurred and whether the returned result corresponds to the authorized request.
The charging rule must also define failures. Charging only for successful responses is buyer-friendly but makes the merchant absorb compute spent on failed attempts. Charging for every attempt protects compute revenue but creates poor incentives when the service is unreliable. A practical policy can distinguish validation failures, merchant-side execution failures, and successful executions whose response was lost in transit. The delivery record makes those distinctions enforceable.
Content Delivery Is Entitlement-Scoped
Digital content changes the unit of value. If an agent buys a premium research report, the commercial promise may be access to a specific edition for 30 days, not one successful HTTP response. Returning the PDF once does not answer whether the agent can download it again, retrieve an updated file, or delegate access to another process.
The contract therefore needs an entitlement:
Accountless payment does not eliminate the need for a stable claimant. A wallet address, agent identity, signed capability, or merchant-issued entitlement token can link a later request to the original purchase. The right choice depends on privacy and recovery requirements. A bearer capability reduces account friction but can be copied if exposed. A persistent identity supports redownload and support, but introduces identity binding and data-retention decisions.
The content merchant must state duration, version, usage rights, concurrency, redownload behavior, and revocation conditions. These are not x402 payment fields by default; they are terms attached to the offer and enforced by the content service. An agent should be able to inspect them before authorizing payment.
Delivery proof also differs from API proof. A response digest may show which file was served, while an entitlement record shows why access was allowed. Neither alone proves that the buyer successfully consumed the content. Merchants should avoid claiming stronger proof than they possess. A signed URL issuance event proves that access was granted; it does not necessarily prove download completion or usefulness.
This is the central tradeoff of accountless content sales: reducing registration friction makes persistent rights harder to recover. Merchants that sell one-time, low-value access may accept bearer-style delivery. Merchants selling ongoing updates or higher-value licenses usually need a durable buyer or agent identity in addition to payment.
Product Delivery Is Order-Scoped
A fixed-price digital product introduces an order as the durable commercial object. The product might be a software license, a downloadable asset bundle, a prepaid service package, or a standardized analysis. The order persists while payment and fulfillment proceed at different speeds.
A clean state model separates four facts:
The merchant's catalog should own the product key, price, description, and version. The order should snapshot the accepted terms so a later price update does not alter an existing purchase. Payment confirmation should reference that order. Fulfillment should have its own idempotency key and terminal state.
Suppose an agent buys a fixed-price compliance template. The payment is confirmed, but license generation times out. The order is paid and unfulfilled; it is not unpaid, failed, or safely repeatable from the beginning. A retry should resume license generation against the same order. If generation ultimately cannot complete, the merchant needs a refund or manual-resolution path tied to the same record.
Asynchronous products also require a delivery channel. A response may return an order status URL rather than the final artifact. Webhooks can notify an agent platform, while polling can provide a fallback. In either case, status transitions must be authenticated and monotonic: a delayed event should not move a delivered order back to processing, and duplicate events should not issue a second license.
For physical goods, inventory, shipping, address validation, cancellation, and returns add further contracts. Those logistics are outside this article's scope. The same architectural rule still applies: payment confirmation authorizes fulfillment work, but it is not evidence that fulfillment completed.
An Integrated Control Plane Can Connect the Contracts
Merchants can assemble these boundaries from middleware, a wallet or facilitator, a catalog, a database, an entitlement service, and custom operational tooling. An integrated commerce product can reduce the number of joins the merchant must build, but it should not erase responsibility boundaries.
GOAT Flow is relevant here because it combines merchant-facing commerce surfaces with operational records. Its current Merchant Guide documents receiving configuration, API keys, webhooks, orders, reconciliation, QuickPay products, hosted checkout, and paid API routes. The current public merchant guide covers DIRECT transfers, in which supported ERC-20 assets move to a configured merchant receiving address. That is a GOAT Flow implementation boundary, not a requirement of x402 as a whole.
Within the contract model, GOAT Flow can perform several distinct jobs:
QuickPay product records can hold a merchant-defined fixed offer.
Public agent instructions and manifests can expose machine-readable discovery.
A current challenge or checkout session can provide authoritative payment terms.
Paid API route flows can join a protected resource to payment verification and a receipt.
Order, webhook, balance, and reconciliation views can provide the merchant operations trail.
The merchant's application still owns the business outcome. It decides whether an API result is valid, what a content entitlement permits, when a license is issued, and what recovery the buyer receives after a service failure. GOAT Flow can connect payment and commerce records; it cannot infer whether a custom model answer met the merchant's quality promise.
Authority must remain explicit. Machine-readable manifests are useful for discovery and preflight, but the active portal, API response, checkout session, or payment challenge controls current terms. Supported chains, tokens, contracts, limits, fees, and capabilities can be deployment- and merchant-specific. A cached manifest or repository type should not override runtime data.
This is also why browser state should not drive fulfillment. A success callback can improve user experience, and a transaction hash can identify an onchain event, but the merchant should release value only from trusted payment status or the verified proof required by the selected integration. The same rule applies when the buyer is an agent rather than a person.
Design Around the Paid-but-Not-Delivered State
The hardest merchant incidents occur between successful payment and successful delivery. Designing this state first exposes missing identifiers and recovery rules before revenue is live.
Disagreement | What the system should preserve | Recovery decision |
|---|---|---|
Payment confirmed, API failed | Payment ID, request ID, failure class, compute state | Retry without recharging, issue credit, or refund under policy |
Agent retried after losing the response | Idempotency ID, stored response or execution status | Replay the result rather than payment and execution |
Manifest price differs from challenge | Manifest version, authoritative challenge, expiry | Require current terms; do not silently alter the signed payment |
Browser says success, server lacks confirmation | Checkout/session ID, transaction candidate, trusted status | Hold fulfillment and reconcile rather than guessing |
Webhook delayed or duplicated | Event ID, order state, receipt time, processing log | Deduplicate, poll authoritative status, and apply monotonic transitions |
Refunds need the same precision as charges. The merchant should define whether a refund reverses only payment, also revokes an entitlement, or leaves access intact because the resource was already consumed. A refund record should reference the original payment and order rather than appearing as an unrelated outbound transfer.
Reconciliation is the process of comparing these independent facts: what the merchant expected, what the payment system verified, what the chain or settlement layer recorded, and what the service delivered. Differences should become explicit cases with owners and outcomes. Hiding them inside one generic failed state destroys the evidence needed to resolve them.
An audit trail should therefore capture authorization and causality, not merely timestamps. At minimum, preserve the resource or product version, quote or challenge ID, buyer or payer identifier, payment identifier, settlement result, order or request ID, delivery status, retry lineage, and any refund or manual decision. Sensitive response content can remain off the log; hashes or references can connect it when necessary.
Build From Fulfillment Backward
Merchants often begin with payment middleware because the 402 exchange is visible and easy to demonstrate. A production build is safer in the opposite order.
First, define successful delivery. For an API, specify the successful status and response artifact. For content, specify the entitlement and access window. For a product, specify the terminal fulfillment event.
Second, define the recovery invariant. Decide what a retry returns, when a refund is allowed, and who resolves a paid-but-undelivered case. If the service cannot answer those questions, adding payment only creates harder incidents.
Third, create the durable identifiers. Bind resource version, quote, payment, order or request, buyer, and delivery record. Test duplicate requests and events before testing volume.
Fourth, make terms discoverable but keep authority server-side. Let agents inspect product or route metadata, then require them to accept a current, expiring payment requirement or session. Record which version they accepted.
Fifth, integrate verification and settlement. Choose self-managed or facilitated verification according to the payment scheme and operational model. Release access only after the authoritative condition for that flow is satisfied.
Sixth, add merchant operations. Webhooks, reconciliation, refunds, keys, team permissions, alerts, and audit history are not secondary polish. They are how the business repairs the gaps between automated systems.
Only after one resource completes this sequence reliably should the merchant add more offer types or networks. A single API route with tested idempotency and recovery is a stronger foundation than a large machine-readable catalog whose fulfillment cannot be proven.
Test the Contract Before Adding Another Sales Channel
x402 makes a payment requirement native to the HTTP request, but AI agent monetization depends on the contract around that exchange. The offer must identify the resource. The payment must bind to current terms. Verification must authorize one entitlement or fulfillment action. Delivery must create its own evidence. Operations must reconcile the cases where those records disagree.
The correct fulfillment unit changes with the product: one request for an API, one entitlement for reusable content, and one order for a fixed-price product. Treating those units explicitly gives agents predictable access and gives merchants defensible revenue records.
Before expanding the catalog, run one paid resource through success, timeout, duplicate request, delayed status, and refund scenarios. For teams that want an integrated path across checkout, QuickPay, API payments, and merchant operations, explore GOAT Flow against the same contract. Add the next sales channel only when the full system can prove what was offered, paid for, delivered, and repaired.


