A unified checkout should give humans and AI agents different buying paths into the same catalog, order, payment, verification, and fulfillment system.
Meta Description: A unified checkout should give humans and AI agents different buying paths into the same catalog, order, payment, verification, and fulfillment system.
Slug: unified-checkout-ai-agents-humans
A unified checkout for humans and AI agents should not force both buyers through the same screen. It should give them different ways to discover, authorize, and pay for an offer while creating the same authoritative business records underneath: one catalog item, one quote, one order, one verified payment state, and one fulfillment result.
That distinction matters. A person can inspect a product page, select a card or wallet, and respond to an error visually. An AI agent needs structured product data, machine-readable payment terms, explicit spending authority, and a deterministic result it can process. Making the interfaces identical would make at least one buyer worse off. Making the back offices separate would leave the merchant with duplicated inventory, conflicting prices, fragmented reporting, and two ways to deliver the same order incorrectly.
The practical model is therefore one commerce system with more than one buying protocol. GOAT Flow provides a concrete example: its public product structure connects Checkout, QuickPay, and API Payments with merchant management and transaction records, while serving stores, human buyers, and AI agents through different entry surfaces.
One Checkout Should Mean One Commercial Truth
“One checkout” is useful only when it describes what the business controls. It should mean that the same offer and the same order rules apply regardless of whether the buyer is a person, an assistant acting with approval, or an autonomous workflow operating within a delegated budget.
The following boundary is more durable than a single universal interface:
Commerce responsibility | Share across humans and agents | Keep channel-specific |
|---|---|---|
Product identity and availability | Yes | Presentation format may differ |
Price and quote validity | Yes | How the buyer reads and accepts the quote |
Order ID and line items | Yes | Session or request transport |
Purchase authorization | Same policy objective | Human consent and agent policy execution differ |
Payment state | One merchant status model | Card, wallet, and protocol evidence differ |
Fulfillment result | One delivery record | Browser response, API response, or entitlement format differs |
Refund and dispute handling | One case history | Rail-specific reversal mechanisms remain different |
The left column is the merchant's commercial truth. The right column contains adapters for the buyer and payment rail. This separation prevents an agent channel from becoming an unsupervised shadow store with a different price, stale inventory, or weaker delivery controls.
It also corrects a common misconception about AI agent checkout. The important feature is not that an agent can press a digital equivalent of a “Buy” button. It is that the merchant can translate a machine request into the same controlled order lifecycle used elsewhere, without depending on visual context or informal human judgment.
The Shared Commerce Contract Has Five Records
Before adding an agent channel, a business should identify five canonical records. These records can be implemented in one service or several connected systems, but each needs a single authority.
1. Offer record
The offer identifies what is being sold: a SKU, report, API route, service package, license, or entitlement. It should define availability, quantity or usage scope, currency or accepted assets, and any conditions that affect delivery. Human-facing copy can be rich and visual; the machine representation must be structured enough to evaluate.
2. Quote record
The quote fixes the payable terms for a limited period. It answers: how much, in which currency or token, to which destination, on which network if relevant, for which offer, and until when? The quote should come from the merchant or its trusted commerce system. Neither a modified browser field nor an agent's cached catalog should become the final price authority.
3. Order record
The order binds buyer intent to the offer and quote. It should carry a stable identifier, line items, amount, customer or agent reference when available, fulfillment destination, and idempotency reference. Humans may arrive through a cart while agents arrive through a structured request, but both need a canonical order if the business is expected to support, reconcile, or refund the purchase later.
4. Payment evidence
Payment evidence is rail-specific. For a card transaction, the merchant may rely on the payment processor's authenticated status and later account for reversals or disputes. For an on-chain transfer, evidence includes the expected network, asset contract, amount, recipient, transaction identity, and confirmation state. For a protected machine resource, a verified receipt may additionally bind payment to a route or request.
The business can normalize these into states such as pending, confirmed, failed, or refunded, but it must not discard the underlying evidence. Two rails can share a status vocabulary without sharing the same proof or reversal behavior.
5. Fulfillment record
The fulfillment record states what the merchant delivered and when. It might contain a shipment reference, download entitlement, API response identity, tool execution ID, license activation, or failure reason. Linking it to the order is what lets support determine whether “paid” also became “received.”
Together, these records form the shared commerce contract:
The contract is more important than the checkout widget. A business can replace a browser, wallet connector, agent client, or payment rail without redefining what was sold and whether it was delivered.
Humans and Agents Enter Through Different Doors
A human checkout usually begins with presentation. The customer browses a site, reads descriptions, selects options, and receives visual prompts. The merchant backend creates or validates the cart and price; a hosted checkout can then collect payment. Errors can ask the person to choose another method or return to the store.
An agent checkout begins with discovery and structured evaluation. The agent needs a canonical service location, machine-readable offers, fresh payment terms, and a result it can parse. It should not scrape a price from decorative page text and assume that price remains valid.
GOAT Flow's current QuickPay design shows how the paths can differ while sharing the merchant configuration. According to the GOAT Flow Merchant Guide, QuickPay can expose a hosted payment page for buyers as well as an agent.md guide and manifest.json for machine discovery. Fixed products use a merchant-configured product record. Dynamic purchases instead use a checkout session created by the merchant backend, keeping authoritative pricing and private merchant credentials away from the browser.
For an API, the interface can be even more direct. The agent requests a protected resource, receives payment requirements, authorizes the payment, and retries with the required evidence. The official x402 introduction defines this HTTP-level pattern. It does not define a merchant's catalog, order support, inventory, refunds, or accounting; those remain commerce-system responsibilities.
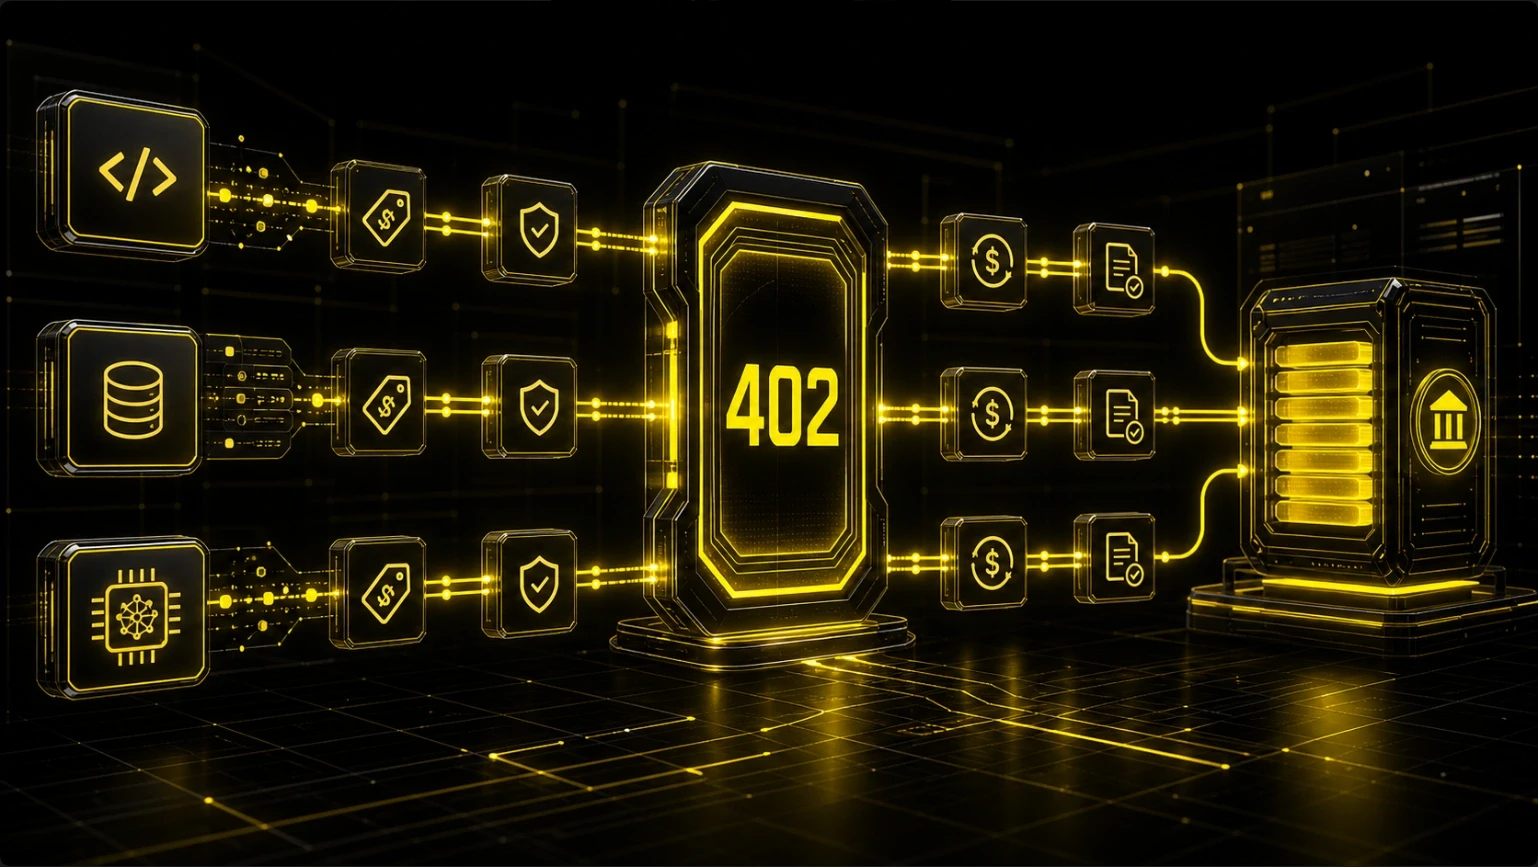
The three entry paths can converge as follows:
The diagram does not imply every purchase needs the same protocol exchange. It means each path must resolve to the merchant's authoritative offer and produce records that the merchant can operate as one business.
Unify the Order, Preserve the Payment Rail
A unified checkout may offer cards, crypto wallets, or an HTTP-native payment flow, but these options solve different parts of the purchase.
Cards give businesses access to established consumer payment behavior and familiar support processes. They also carry processor rules, fraud controls, possible chargebacks, regional availability, and credentials designed around human or delegated consumer commerce.
Direct crypto payments let a wallet transfer a supported asset to a merchant receiving address. They are programmable and can work across borders, but the payer needs a compatible wallet, the correct asset, and sometimes native gas. Transfers may be difficult or impossible to reverse without a separate merchant refund transaction.
x402 communicates payment requirements at the HTTP layer. It is particularly useful when the thing being bought is itself an HTTP resource, such as an API response, data result, model call, or machine tool. It does not turn every retail checkout into an API, nor does it replace order management.
The GOAT Flow product page currently describes card payments through Stripe and cryptocurrency payments that move directly to the merchant wallet. That combination can support a common business catalog while retaining different payer experiences. However, a merchant should verify the active deployment before relying on any specific card market, network, token, limit, or fee. Current runtime configuration, not a static article, is the authority for what a merchant can accept.
The design rule is simple: normalize the commercial outcome, not the rail's semantics. An order may become paid through different methods, but the record must retain which method was used, what evidence supports the state, and which recovery actions are possible.
Machine Access Needs Explicit Authority
An agent's ability to discover an offer is not permission to buy it. A wallet's ability to transfer funds is not proof that a user or organization intended this purchase. A valid payment is not proof that the agent should receive every resource the merchant operates.
A safe AI agent checkout separates four decisions:
Discovery: Can the agent locate and understand the product or service?
Identity or context: Which agent, user, organization, wallet, or task is making the request?
Authorization: Is this buyer allowed to purchase this item at this price under the current budget and policy?
Payment: Did the expected value move under the terms bound to the order?
For a low-cost public report, a merchant may allow accountless purchase and deliver a download entitlement after verified payment. For licensed data, regulated goods, age-restricted products, volume-priced services, or private APIs, payment alone will not satisfy identity and authorization requirements. The agent may still need an account, API credential, entitlement, signed delegation, or approval step.
Buyer-side controls matter as well. Autonomous payment should mean policy-controlled execution, not unlimited spending. A practical agent policy can constrain the merchant, product category, maximum amount, cumulative task budget, accepted networks and assets, quote expiry, and circumstances requiring human approval. The commerce system should provide enough structured terms for that policy to make a deterministic decision.
This is another reason not to force the human and agent journeys into one screen. Human consent can be gathered through visible review and confirmation. Agent consent is better represented by explicit delegated authority and a logged policy decision. They serve the same business objective but require different evidence.
Payment Success Is Not Yet Delivery
Unified checkout fails if each channel uses a different shortcut to authorize fulfillment. A browser may display success before the merchant backend has validated the final order state. An agent may hold a transaction hash that points to a real transfer but does not match the expected recipient, asset, amount, network, or order. A webhook may be delayed or replayed. A retry may execute the service twice.
The GOAT Flow integration guide makes a critical boundary explicit: browser callbacks are user-experience events, not payment proof. Its hosted checkout model keeps product and session prices server-authoritative, and merchants are expected to use trusted backend status or authenticated evidence before fulfillment.
A channel-neutral fulfillment decision should verify at least:
the order is the one the merchant created;
the paid offer, amount, currency or token, destination, and network match expected terms;
the payment state comes from a trusted processor, merchant API, authenticated webhook, or validated receipt;
the order has not already been fulfilled;
the requested product is still deliverable;
the fulfillment action records its own stable result or failure.
Idempotency connects these checks. The same purchase intent should retain one stable idempotency key across retries. A network timeout should lead the client or merchant to query existing state, not create a new payment blindly. Fulfillment should also reject a second delivery attempt for the same order unless the product explicitly permits it.
The hardest case is “paid but not delivered.” Stock may disappear, an API dependency may fail, a model call may time out, or a license system may reject activation. The order should move into a recoverable exception state rather than being mislabeled as complete. The merchant then needs a defined choice: retry delivery, issue an alternative entitlement, or refund through a method supported by the original rail and business policy.
Unified checkout does not eliminate this failure. It makes the failure visible in one place and gives every channel the same commercial resolution.
One Back Office Still Needs Rail-Aware Recovery
The operational benefit of unified checkout is not merely a cleaner dashboard. It is the ability to answer one set of business questions across all buyers:
Which offer was purchased?
What price and terms were accepted?
Which orders are awaiting payment, confirmation, delivery, or review?
Did a retry create a duplicate transaction?
Which payment and delivery records support a customer claim?
What revenue was received by method, asset, network, product, and buyer channel?
GOAT Flow's documented Merchant Portal groups orders, reconciliation, receiving addresses, hosted checkout, QuickPay Products, paid API routes, balances, API credentials, webhooks, team roles, and audit logs. This is the product layer above a payment protocol: it gives the merchant a place to operate transactions instead of merely returning a payment requirement.
Still, “one back office” should not mean one generic refund button with identical behavior. A card payment may be refundable or disputable through the processor. A direct on-chain transfer generally requires the merchant to create a new outbound transaction if it agrees to a refund. An API call that already consumed compute may need a service-credit policy rather than an automatic monetary reversal. The support interface can unify the case, but the resolution must remain rail- and product-aware.
The same is true for identity. A human email, account ID, wallet address, agent identifier, and organization credential are not interchangeable. The merchant should link them to the order when justified, minimize unnecessary data, and preserve the original buyer context for support and audit.
Reporting should therefore contain two layers: normalized business fields for revenue and fulfillment, plus native rail and channel fields for investigation. Removing the second layer may simplify a dashboard while making exceptions harder to resolve.
A Software Merchant Shows Where the Paths Converge
Consider a hypothetical research-data company with three offers:
A fixed-price industry report available as a PDF.
The same report available for purchase by a research agent.
A pay-per-request company-enrichment API.
The human visits the storefront, selects the report, and opens hosted checkout. The agent reads a machine-readable product catalog, evaluates the same report ID and price, then opens or executes the supported payment path. Both channels create an order for the same offer version. Both must receive one download entitlement after the payment is verified.
The API follows a different entry protocol. The research agent calls the endpoint and receives a machine-readable payment requirement. Once valid payment evidence is presented, the endpoint returns the requested data. The merchant can record the request against the same customer or agent context when available, but it should use a fulfillment record suited to API delivery: request ID, response status, usage unit, and result hash or reference where appropriate.
Now consider three failures:
The agent cached yesterday's report price. The server-authoritative quote rejects the stale amount rather than creating an underpaid order.
The human closes the browser after paying. Backend verification still advances the order, and the customer can recover the entitlement later.
The paid enrichment request times out after execution begins. The stable request and payment identifiers let the merchant determine whether to return the existing result, retry execution without charging again, or mark the order for recovery.
The interfaces and delivery artifacts differ, but offer identity, accepted terms, payment state, support history, and commercial reporting remain connected. That is a unified checkout architecture.
Adopt One Shared Record at a Time
Businesses do not need to replace their entire commerce stack to add an AI agent checkout. A staged approach reduces the chance of creating a parallel system.
Stage 1: Canonicalize the offer. Give every product and paid service a stable identifier. Decide where availability, price, usage rights, and delivery terms are authoritative.
Stage 2: Canonicalize the order. Ensure every channel can create or reference one order model with line items, quote version, buyer context, payment state, and idempotency key.
Stage 3: Add a machine-readable entry path. Start with one bounded fixed-price product or API. Expose only the fields an agent needs to discover, evaluate, and request it. Do not expose merchant secrets or let cached metadata override fresh terms.
Stage 4: Normalize verification and fulfillment. Map each rail's trusted evidence into the order state, then require one idempotent fulfillment service to check that state. Exercise duplicate requests, stale quotes, delayed confirmation, failed delivery, and refund handling before launch.
Stage 5: Unify operations and measure separately. Let support and finance search one order history, while preserving channel and payment-method dimensions. Compare completion, failure, recovery, support load, and repeat use without assuming an agent channel should behave like a human funnel.
A business is ready when it can answer this question for any purchase: “Which authoritative offer and order did this buyer accept, what evidence proves payment, and what record proves delivery?” If the answer depends on inspecting a browser message or an agent transcript, the checkout is not yet unified.
For businesses evaluating a concrete implementation, explore GOAT Flow and verify the current Checkout, QuickPay, API Payment, network, asset, limit, and merchant-operation capabilities in the intended deployment.
FAQ
Does unified checkout require humans and AI agents to use the same payment method?
No. It requires different payment methods to resolve to the same authoritative offer, order, payment-status, and fulfillment model. Card and crypto rails should retain their native evidence, fees, confirmation, refund, and dispute behavior.
Can an AI agent use a hosted checkout page?
It can when the integration provides a supported machine workflow, but agents should not be expected to interpret a visual page like a person. A public manifest, structured product record, or API payment requirement is more reliable for automated discovery and decision-making.
Does x402 replace a merchant's existing checkout system?
Not by itself. x402 communicates payment requirements for HTTP resources. A merchant still needs product or service definitions, pricing authority, order records, payment verification, fulfillment logic, reconciliation, and exception handling.
Can agent purchases be accountless?
Some public, low-risk, fixed-price products or APIs can support accountless payment-gated access. Persistent licenses, private data, regulated products, negotiated pricing, subscriptions, or role-based services may still require identity, credentials, and an account relationship.
Should a merchant fulfill an order after receiving a transaction hash?
No. The merchant should verify that the transaction and trusted payment state match the expected order, network, asset, amount, recipient, and transaction identity, then ensure the order has not already been fulfilled.
How should refunds work in a unified checkout?
The support case and order history can be unified, but the refund action remains payment-method-specific. Card processors may support reversals through their systems; direct on-chain refunds generally require a new merchant-authorized transfer and careful validation of the destination.
One Business System, More Than One Buying Protocol
Human and agent checkout should converge where the business needs control and diverge where the buyer needs a usable, authorized interaction. The merchant should share the catalog, quote, order, payment state, fulfillment record, and operating history. It should preserve different discovery methods, consent evidence, credentials, payment proofs, and recovery procedures.
That design gives an AI agent a machine-readable route to purchase without weakening the human experience or creating a second source of commercial truth. The most important test is not whether both buyers can reach a payment screen. It is whether the business can prove, through one coherent record, what each buyer agreed to, how payment was verified, and whether the promised product or service was delivered.


