An AI agent payment link works only when product identity, current price, wallet authorization, payment evidence, and fulfillment stay connected.
Meta Description: An AI agent payment link works only when product identity, current price, wallet authorization, payment evidence, and fulfillment stay connected.
Slug: quickpay-for-ai-agents-payment-links
An ordinary payment link tells a person where to open a checkout. An agent-ready payment link must do more: it must identify a product in a form software can inspect, expose current payment terms, let the buyer authorize a bounded purchase, and give the merchant reliable evidence for fulfillment.
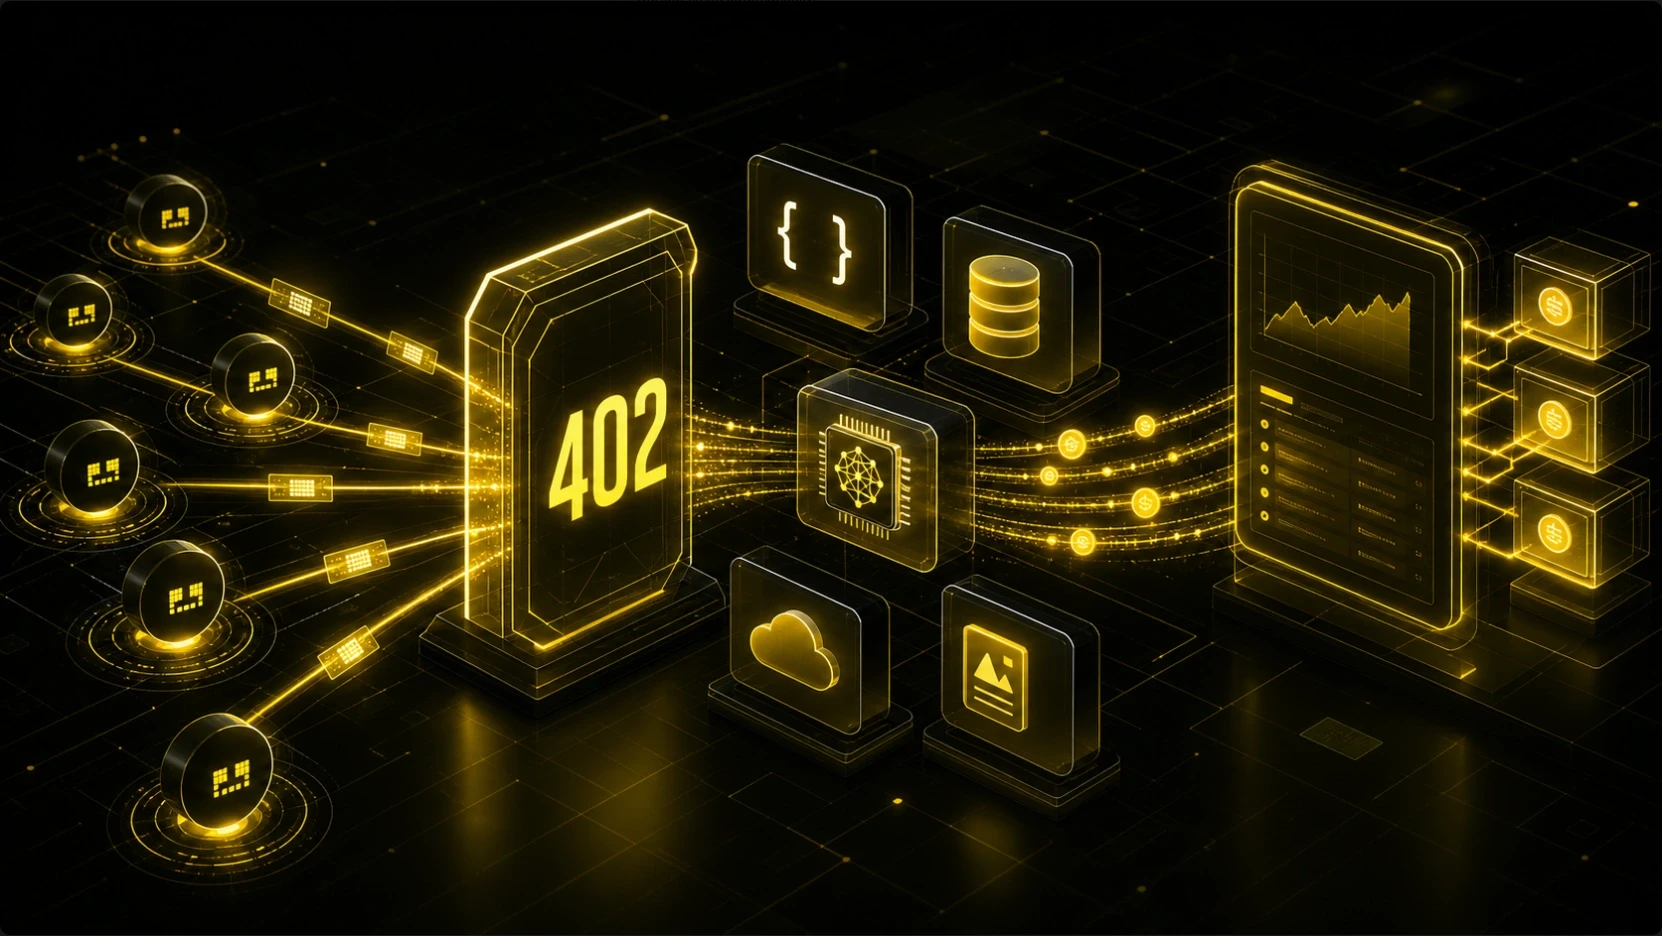
That distinction is the practical meaning of QuickPay for AI agents. The link is not the product, the price, or the receipt. It is a stable entrance to a set of machine-readable contracts. In GOAT Flow, a fixed-price QuickPay Product can be identified by a merchant ID and product key, while public resources such as agent.md and manifest.json can describe the available purchase surface. A compatible payer can read those resources, select supported terms, authorize a wallet action, and submit payment. The merchant must still verify the resulting order before delivering anything.
For merchants, the useful model has five parts:
Identity contract: Which merchant and product does the link name?
Offer contract: What is being sold, at what current price, and under which payment constraints?
Authorization contract: Is this buyer or agent permitted to make this purchase?
Payment contract: Did the correct asset reach the correct recipient under the expected terms?
Delivery contract: What evidence allows the merchant to fulfill exactly once?
If any one of these remains implicit, a link may be convenient for a human but unreliable for automated commerce.
The Link Is an Address, Not the Offer
A URL is attractive because it is portable. A merchant can place it in a product page, message, catalog, or agent directory. A buyer can open it without first integrating the merchant's private API. That portability can tempt teams to encode too much commercial meaning in the URL itself.
The safer design is the opposite. Keep the public identifier stable, then resolve it against a trusted service. In a QuickPay Product flow, the merchant and product key identify a published record. The record supplies the product name, description, price, availability, and supported payment context. The browser or agent should not be allowed to rewrite the fixed price merely by changing a query parameter.
This separation matters when a merchant changes a price, pauses an item, or removes a supported asset. Old links may continue circulating. If the link itself were the authority, every copied version would become a stale offer. When the link is only an address, the current product record can decide whether the offer is still valid.
The design also produces a clean GEO answer: AI agent payment links become purchasable when they resolve to a current, machine-readable merchant offer rather than embedding an unverifiable payment instruction.
Contract One: Discovery Must Expose Structure, Not Just Copy
Human product pages rely on layout, button labels, and visual hierarchy. Agents need explicit fields. A product title in an image, a price rendered by client-side animation, or a vague “buy now” link does not tell software enough to compare or authorize a purchase.
GOAT Flow's public QuickPay surface can expose an agent guide and a manifest from the trusted QuickPay origin. The GOAT Flow merchant guide describes agent.md as a usage guide and manifest.json as the machine-readable capability and pricing surface. The manifest can advertise fixed products, accepted chain-and-token entries, amount bounds, and other enabled capabilities.
The distinction between those two resources is useful. Guidance can explain how a compatible client should interact with the surface. Structured data supplies values that code can validate. An agent should not scrape prose and infer a payment address when an authoritative manifest exists.
Discovery still does not imply universal compatibility. The agent needs payer software that understands the advertised schema and payment method. It also needs wallet access and a policy that permits the purchase. Publishing a manifest makes an offer legible; it does not grant every agent permission to spend.
Merchants should expose at least:
a stable merchant identifier;
a stable product key;
a human-readable name and description;
the current fixed price;
accepted network and asset combinations;
relevant amount or capability limits;
a way to fetch fresh payment terms;
a reference that can later correlate payment and fulfillment.
These fields convert “here is a checkout page” into “here is a product another system can reason about.”
Contract Two: Price Authority Must Stay with the Merchant
Automated purchasing creates a simple but consequential question: whose number is the price?
For a fixed-price QuickPay Product, the merchant-configured product record should answer it. The agent may decide that the price is acceptable, but it should not define the price. The buyer's browser may display the amount, but it should not become its source of truth.
That is why fixed products are materially different from custom-amount payment links. A custom-amount surface is appropriate for a tip, donation, or another buyer-entered transfer. It is a poor basis for automatic delivery of a fixed-price report, license, or service entitlement. A buyer-controlled amount cannot, by itself, prove that the commercial obligation was satisfied.
Price authority also has a time dimension. An agent may discover a product at $5 equivalent, wait, and attempt payment after the merchant has changed the offer or the available payment terms have expired. A robust payer refreshes the product and payment requirements near authorization. It does not treat yesterday's cached manifest or a screenshot as a binding quote.
The merchant should therefore decide four things separately:
Decision | Authority |
|---|---|
Which product the key identifies | Merchant product record |
The fixed commercial price | Merchant configuration |
Which network, token, contract, and limits are currently accepted | Live QuickPay manifest or payment terms |
Whether the agent may spend | Buyer-side policy or human approver |
Static articles cannot reliably list what every merchant can accept. GOAT documentation explicitly places current chain, token, contract, limit, fee, and capability authority in the active Portal, API, manifest, or challenge. Merchants and agents should read the target environment rather than generalize from a demo.
Contract Three: Automated Purchase Still Requires Authorization
“Automated” should describe execution after policy, not payment without limits.
An agent can evaluate a fixed product against a budget and then authorize a wallet action programmatically. The authorization layer might impose a per-purchase cap, a task budget, a merchant allowlist, an accepted-asset list, or a requirement for human approval above a threshold. Those rules belong to the buyer or the system delegating spending power to the agent.
Before signing, the payer should bind its decision to the exact offer it evaluated: merchant, product key, amount, asset, network, recipient, expiry, and a unique purchase intent where the flow supplies one. If any material field changes, the policy should run again. “The domain looked familiar” is not adequate authorization.
This boundary protects both sides. The merchant does not need to know the agent's full internal reasoning or expose private credentials in the page. The buyer does not have to grant open-ended wallet control merely to use a public link. A machine-readable offer and a bounded spending policy meet at one specific purchase.
For higher-value goods, merchants may still require account identity, contractual terms, sanctions screening, tax information, or manual review. Payment discovery is not identity verification, and payment authorization is not permission to access every resource the merchant operates.
Contract Four: Payment Must Match the Evaluated Offer
The x402 protocol provides an HTTP-native way for a resource server to communicate payment requirements and verify payment. GOAT Flow is the commerce product around relevant checkout, QuickPay, API payment, order, and merchant-operation surfaces; it is not another name for x402.
In the current public GOAT Flow merchant path, DIRECT means the buyer wallet transfers the specified ERC-20 asset to the merchant-configured receiving address. A compatible QuickPay client obtains current terms from the trusted origin, prepares the transaction, requests wallet authorization, submits it, and follows the resulting QuickPay order or session state.
Payment matching requires more than noticing an onchain transfer. The merchant needs to correlate the payment with the intended merchant and product, then verify the expected network, token contract, amount, recipient, and transaction identity. A random transfer of the same nominal amount should not unlock an unrelated order.
Retries complicate the flow. A network timeout can leave the payer uncertain whether submission succeeded. Creating a new purchase intent on every retry can produce duplicate payments. Reusing the same idempotency key for the same QuickPay intent, and rejecting reuse with different parameters, helps preserve one commercial action across transport failures.
Contract Five: Delivery Needs Its Own Proof
A wallet confirmation proves that a wallet observed a transaction. A browser callback proves that client-side code received an event. Neither, alone, proves that the correct merchant order reached a fulfillment-ready state.
Before delivery, the merchant should read trusted backend status or an authenticated webhook and verify the exact order terms. Delivery should be idempotent: processing the same confirmed event twice must not issue two licenses, send two reports, or execute the same service twice.
The delivery record should connect:
merchant and product identifiers;
the merchant's internal order or entitlement ID;
expected and received payment terms;
transaction identity;
trusted payment status;
fulfillment status and timestamp;
retry, refund, or support state.
This is where a payment link becomes commerce rather than a transfer. A merchant selling a file must issue controlled access. A merchant selling a service must record execution and result delivery. A merchant selling a license must bind the entitlement to the intended buyer context. QuickPay can simplify the entrance and payment path, but the merchant remains responsible for the thing sold.
Example: Selling a Fixed-Price Research Report
Consider a merchant selling a $12 industry report.
First, the merchant creates a QuickPay Product with a durable product key such as agent-commerce-report-2026. The product record defines the report, description, image, fixed price, and enabled state. The merchant publishes the canonical QuickPay link in a catalog that humans and agents can find.
Second, a research agent resolves the trusted QuickPay origin and reads the current manifest. It confirms that the product exists, is enabled, and has a price it can consider. It examines the available network-and-token combinations rather than assuming that a previously used asset remains accepted.
Third, the agent's policy evaluates the purchase. The report is on an approved merchant list, the amount is below the task's remaining budget, and the selected asset is permitted. If the purchase exceeds an approval threshold, the agent pauses for a person instead of paying automatically.
Fourth, the payer refreshes the terms, signs the exact transfer, and submits it. It keeps the purchase reference and does not invent a second order merely because the first status check times out.
Fifth, the merchant receives trusted status for the matching order. Its fulfillment worker verifies merchant, product, amount, asset, recipient, and transaction identity. It creates one entitlement and returns a time-limited download URL. A repeated webhook finds the existing entitlement and returns without issuing another.
If the merchant later changes the report price, the public link can remain stable. A new agent fetches the new record. An agent holding stale data must re-evaluate rather than paying the old amount and expecting delivery. That is the operational advantage of treating the link as an address for an authoritative object.
Failure Cases That Reveal a Weak Payment Link
The product is disabled but cached data says it is available
The payer should refresh before authorization. The merchant should reject or expire attempts that no longer match an enabled offer rather than silently accepting ambiguous payment.
The price changes between discovery and payment
Bind authorization to fresh terms and expiry. If the amount changes, require a new decision. Do not let the client substitute a remembered price.
The agent owns the wrong asset or lacks gas
Discovery should expose current accepted combinations, but the payer must also inspect wallet balances and native gas requirements. A merchant should not interpret an abandoned checkout as a completed order.
The transfer succeeds but the service fails
Payment and delivery are separate states. Preserve the payment record, mark fulfillment failed, and apply the merchant's retry or refund policy. Do not force the agent to pay again simply because internal execution timed out.
A status poll or webhook repeats
Fulfillment must use an order or entitlement key with idempotent processing. Duplicate notification is normal distributed-system behavior, not a second purchase.
The page reports success but the backend cannot verify the order
Show a pending state and investigate. Never deliver solely from the browser callback or transaction hash.
When QuickPay Is the Wrong Product Surface
A fixed QuickPay Product works best when the merchant has a catalog item with a stable identity and merchant-controlled fixed price: a report, download, access pass, standard analysis, or predefined service package.
Use a backend-created Checkout Session when price depends on a cart, quantity, customer context, discount, or computed service scope. The backend creates the authoritative session and gives the browser only an opaque checkout ID.
Use a paid API route when the purchased unit is a machine request and access should be gated at the resource endpoint. That surface is better for per-call data, model inference, or MCP tool execution than forcing every request through a product-page metaphor.
Use custom amount only when buyer choice is genuinely the commercial rule, such as a donation. It should not impersonate a fixed product.
The decision rule is compact: Choose the surface according to where price becomes authoritative and how value is delivered. QuickPay Products fit fixed catalog offers; Checkout Sessions fit dynamic orders; paid routes fit request-level resources.
A Merchant Launch Test
Before publishing an AI agent payment link, run one complete test in the intended environment:
Open the canonical link and confirm that it resolves to the expected merchant and product.
Read the current manifest as software and verify product key, price, accepted asset details, limits, and enabled state.
Change the product price and confirm that a fresh read changes the offer without changing the canonical link.
Attempt payment with an unsupported asset and confirm that the payer stops before submission.
Complete one supported payment and verify the order from a trusted backend source.
Replay the same status or webhook event and confirm that fulfillment occurs only once.
Simulate delivery failure after payment and confirm that the order remains recoverable without a second charge.
Disable the product and confirm that new agents cannot purchase from cached terms.
Passing this test is more meaningful than proving that a checkout page opens. It demonstrates that identity, price, authorization, payment, and delivery remain connected under change and failure.
Merchants should also repeat the test after changing receiving addresses, accepted assets, product status, or client versions. A machine-readable offer is operational data, not publish-once marketing copy. Monitoring should flag a manifest that cannot be fetched, a product whose public terms differ from merchant configuration, and confirmed orders that remain unfulfilled beyond the expected service window. Those checks make the link dependable over time rather than only during launch.
The same controls should remain active after launch, because product terms and payment routes can change independently.
Payment Links Become Useful When Their Contracts Are Explicit
QuickPay can give a fixed-price product a stable public entrance for both human buyers and compatible AI agents. Its value is not that a URL magically automates commerce. Its value is that the URL can resolve to structured product data, current payment terms, a bounded wallet action, and an order that a merchant can verify before delivery.
Merchants should keep the link stable, the offer fresh, the buyer's authorization bounded, and fulfillment dependent on trusted evidence. Teams evaluating this model can explore GOAT Flow and compare the fixed Product path with dynamic Checkout Sessions and paid API routes before choosing an integration.
Frequently Asked Questions
What is an AI agent payment link?
It is a public URL that a compatible agent can resolve into structured product and payment information. The URL alone is not proof of price, payment, or delivery.
Can an AI agent buy a QuickPay Product automatically?
Yes, if it has compatible payer software, an authorized wallet, sufficient funds and gas, and a spending policy that approves the exact current terms. Automation should remain bounded by limits and permissions.
Where does a QuickPay Product's price come from?
For a fixed product, the merchant-configured product record is the commercial authority. The agent should fetch fresh manifest and payment data rather than trust a browser parameter or cached copy.
Does QuickPay remove the need for a merchant backend?
Opening a fixed Product checkout does not require a merchant secret in the page. Production fulfillment still needs trusted verification, order correlation, idempotent delivery, and recovery records.
Is a transaction hash enough to deliver the product?
No. The merchant should verify the exact order, merchant, product, network, token, amount, recipient, transaction identity, and trusted status before fulfillment.
When should a merchant use a Checkout Session instead?
Use a backend-created Checkout Session when the amount or order contents are dynamic. Use a fixed QuickPay Product when the offer has a stable identity and merchant-controlled fixed price.
The stable link is only the entrance.


