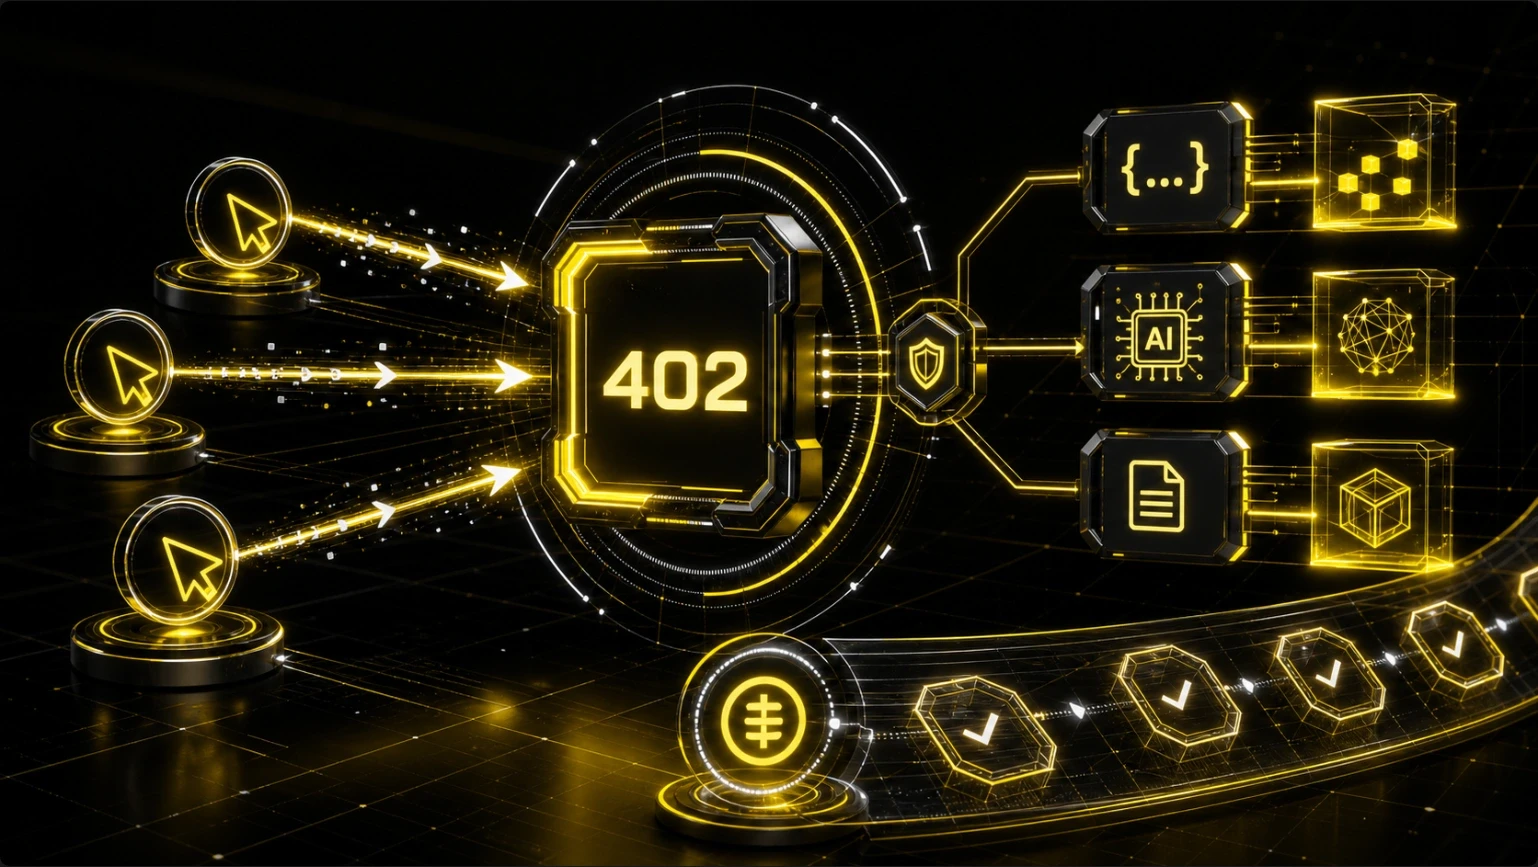
Choose x402 infrastructure by responsibility: API middleware, payment verification, edge gateways, or merchant orders, with GOAT Flow's role and limits.
Developers can charge AI agents using x402 Foundation SDKs and middleware, hosted facilitators such as Coinbase CDP, developer payment stacks such as thirdweb, or gateways attached to an existing deployment. GOAT Flow API Payments is relevant when charging also requires merchant-managed orders, payment status, and fulfillment coordination. Bazaar addresses service discovery, not payment processing. These options occupy different positions in a paid-service architecture; several may be used together.
The useful selection question is not which name appears on the longest feature list. It is which responsibility you need to outsource, and what happens when that operation has an uncertain outcome. A payment challenge, a settled transfer, and a delivered API result are different events.
Start With the Job You Need to Outsource
Use the following starting points to narrow the decision. The comparison reflects official documentation reviewed on October 21, 2026, not executed integrations, measured performance, or guaranteed account eligibility.
Your immediate job | Starting point | What to verify before committing |
|---|---|---|
Add payment requirements to a new API route | Language/framework integration, protocol version, scheme, receiving wallet, and production verification/settlement path | |
Outsource payment verification and settlement | Credentials, supported network/scheme/token combination, risk screening, and current commercial terms | |
Compose a provider-specific paid API integration | The particular client/server/facilitator path, server-wallet configuration, and token authorization requirements | |
Charge matching traffic at the Cloudflare edge | Closed-beta admission and the documented requirement that both buyers and sellers be US-based | |
Monetize traffic already served through CloudFront | A CloudFront-associated WAF web ACL, rule configuration, supported payment network, and actual client compatibility | |
Connect a paid API purchase to merchant order operations | Merchant setup, configured chain/token, integration profile, completion checks, and application-owned delivery | |
Describe payable resources so agents can find them | Resource metadata, supported directory/facilitator integration, actual listing, and evolving API behavior |
This is not a ranking of seven interchangeable payment providers. Middleware can use a facilitator. A gateway can rely on a facilitator. A merchant platform can maintain business state around payments. A discovery extension helps prospective clients locate resources without becoming the system responsible for delivering them.
Start with an existing constraint. A team building its first paid endpoint has a different integration problem from a publisher already operating CloudFront. A data business that must recover failed purchases needs more than a convenient way to return HTTP 402. That difference determines which evidence to request from a provider.
A Paid Request Crosses Several Responsibility Boundaries
The resource server defines what is sold and which payment terms it accepts. The client interprets those terms and obtains authority to spend. Payment verification determines whether the submitted payment material meets the selected mechanism's requirements. Settlement commits the economic operation according to that mechanism and network. The merchant application handles the result or entitlement the buyer purchased.
The diagram assigns responsibilities; it does not prescribe one settlement order for every scheme. The selected payment mechanism determines how authorization, resource execution, and settlement are sequenced. An integration must follow that contract rather than assume that every successful verification means money has moved irreversibly or that every handler runs only after final settlement.
A third-party facilitator is not mandatory in every implementation. The Foundation's facilitator documentation permits local verification and direct settlement as well as hosted services. Removing the vendor does not remove those jobs. Someone still needs to validate the payment, submit or observe the required operation, and reconcile failures.
Identity and access are separate again. A payment may establish that a resource's price was met without proving that the caller has permission to retrieve private customer data. Likewise, a directory entry does not authorize a purchase. Keep the service's access policy and the buyer's spending policy attached to their own trusted systems.
New APIs: Compose Middleware With the Right Verification Path
For a new paid API, the reference seller integrations are a natural starting point. The Foundation provides language-specific paths for Node.js, Go, and Python. The server protects a resource and describes acceptable payment conditions; a compatible client handles the payment exchange. Your application still decides what one billable call means and how the purchased result is associated with that call.
Do not promote a test configuration into production unchanged. The seller quickstart identifies the public x402.org facilitator as a development/testnet service. Moving to a production network requires reviewing the facilitator or self-operated implementation, receiving wallet, asset, and network configuration together. A familiar package name does not prove that an arbitrary signer and token will work with the chosen server.
Coinbase CDP provides hosted verification and settlement. Its documentation describes authenticated facilitator access, supported schemes and networks, and risk screening that can decline payments. Evaluate that operational contract rather than describing it as an unconditional relay. Check the current support information and account requirements; a broad list of chains elsewhere on a platform is not a compatibility guarantee for this particular payment route.
thirdweb offers another developer-composed route. Its x402 documentation describes client, server, and facilitator integration with wallet configuration and token authorization conditions. The token requirements of one documented path should not be applied to every thirdweb product or chain. Nor should broad marketing coverage become a claim that your exact client, token, and destination network have been tested together.
If an existing agent also needs payment tools, GOAT Flow for AgentKit documents payer-side adapters separately from merchant-side actions. These can connect an agent to a supported merchant integration. They are not a universal bridge between arbitrary Foundation middleware, third-party facilitators, and GOAT's order API. Match the adapter, profile, and deployment explicitly.
Hosted facilitation reduces the amount of settlement infrastructure your team must operate. In return, you depend on its credentials, supported combinations, screening, availability, and pricing contract. Self-operation offers more control but transfers responsibility for RPC reliability, transaction handling, monitoring, and recovery to your team. Choose it when that ownership is deliberate, not merely because a hosted service is technically optional.
Before selecting either, write down the supported protocol version, transport, scheme, network, token contract, signer, verifier, and receiving address. Reject unsupported terms. If no component can explain how an uncertain settlement is recovered, the integration is not complete just because its happy-path request returns data.
Existing Services: Check the Gateway's Deployment Boundary
A gateway can place charging rules in front of traffic without moving every handler into a new application. That can suit an existing API, content service, or tool endpoint. It does not mean that every deployment is eligible or that an edge payment rule replaces the service's business logic.
Cloudflare Monetization Gateway documents rules for matching requests and attaching payment requirements. Its described flow verifies authorization, obtains the origin response, and settles through the Coinbase x402 Facilitator. As of the reviewed documentation, it is in closed beta, with both buyers and sellers required to be based in the United States. Those are selection constraints, not details to postpone until after an integration is designed.
AWS WAF AI traffic monetization belongs to a different deployment boundary: its setup requires a WAF web ACL associated with an Amazon CloudFront distribution. A business already serving content through CloudFront should evaluate that path against its traffic rules and payment configuration. A team using another AWS service should not infer support solely because that service can integrate with WAF in other contexts.
HTTP 402 in a cloud product's documentation also does not establish compatibility with every Foundation SDK version. Verify the buyer's supported exchange and the deployment's configured networks. The relevant question is whether the actual agent can satisfy the gateway's payment contract, not whether both products use the same status code.
Consider an existing research-content API whose origin already manages customer entitlements. An edge rule may be a useful charging entry point, but the origin still needs to know which paid request can access which result. If a response disappears after payment, the merchant needs a recovery path. Gateway placement can reduce integration work; it does not erase the sale's operating obligations.
Merchant Operations Begin Where a 402 Challenge Stops
GOAT Flow is a useful candidate when the missing layer is the commercial purchase record around a paid API. Its API Payments documentation assigns authentication, pricing, order creation, and delivery to the merchant's backend while providing payment requirements and payment/order handling. That is a more specific role than calling it another generic facilitator.
GOAT Flow's Merchant Portal covers merchant approval, payment configuration, orders, credentials, webhooks, and reconciliation. These require the active deployment's configuration. Service-fee credits are not a pooled balance of customer payments: the documented DIRECT Crypto flow sends the buyer's tokens to the configured merchant recipient. Verify applicable fee-credit requirements separately from the payer's funds and transaction gas.
Two forms of state matter. Payment state records what happened to the purchase's payment obligation. Delivery state records whether the requested data, report, or entitlement was returned. A payment platform can provide an authoritative payment result without proving that your application delivered the correct resource. Keeping both records is what makes a paid API recoverable.
There is also an attributed commercial example. In its September 10, 2026 announcement, GOAT Network reports that StableJack made 96 market-data endpoints payable through GOAT Flow at 0.5 USDC per call. That illustrates the intended API-business use case. It is a vendor-published account, not an independent runtime test, general pricing schedule, or proof that another integration works without adaptation.
Design One Paid API Purchase Before Calling It a Demo
Take a hypothetical /api/market-snapshot operation priced at 1 USDC per purchase. This is a design example, not a real provider quote or executed transaction. Choose GOAT Flow's documented Custom Integration for this example; do not mix it with the separate MPP receipt flow or present it as a drop-in Foundation middleware recipe.
First establish the environment using the Merchant Portal setup and operations. Obtain the approved merchant configuration and backend credentials, identify the supported network/token pair and receiving address, and pin the actual SDK release your team can install and test. Amount units must follow that token's decimals. A display amount is not a safe integer transfer amount until the asset configuration is known. Keep credentials, pricing, and allowed recipients out of untrusted client input.
The merchant then needs one durable business record for the intended purchase. Save the request identifier, validated customer or caller context, request inputs, price, payer, network, token, and a stable dappOrderId before creating a platform order. Reuse of the identifier with different inputs or payment terms must be rejected, not interpreted as an update to an already authorized purchase.
The current API Payments example describes application-owned persistence and an atomic creation claim. Only its first eligible caller may create the platform order. Concurrent calls and process restarts must not obtain fresh creation authority simply because the first response is late. That database behavior is your implementation obligation, not a magic SDK option.
After creation, save the returned platform order ID and payment requirements before presenting them to the agent. The agent checks the amount, permitted recipient, chain/token, expiration, and remaining budget through trusted policy, then authorizes the supported transfer. A model writing confirmed: true is not authenticated human consent, and a payment protocol does not supply unlimited spending authority.
The backend verifies the original order through its authenticated status path or validates the applicable authenticated webhook. It checks the purchase association and method-specific completion rule, then invokes a durable once-only delivery operation. Store the resulting snapshot or entitlement so that a lost HTTP response can be recovered without selling the same resource again.
Now consider the more revealing case: platform order creation times out before the response is saved. The current Server SDK contract does not offer a general idempotencyKey for ordinary creation. Repeating an existing dappOrderId is rejected; it is not a lookup returning the original order. Preserve the creation claim and mark the purchase for reconciliation. Use saved merchant and purchase details to locate the original outcome instead of inventing a public lookup method or immediately creating another payable order.
If a transfer was already broadcast, preserve its transaction association as well. Expiry, a polling timeout, or a disconnected page does not prove that funds never moved. Recover the original purchase before asking the agent to authorize a replacement. A real demo must show this behavior with actual redacted records; the proposed sequence alone does not prove it.
Production Evidence Must Cover Rejection and Recovery
A successful small purchase is useful evidence, but it leaves the most consequential boundaries untested. Require observed outcomes for the following cases before expanding autonomy or describing an integration as production-ready.
Test condition | Expected application behavior | Evidence to retain |
|---|---|---|
Unsupported scheme, network, token, expired quote, or substituted recipient | Reject before signing or transferring | Validated terms, rejection reason, and trusted policy context |
Purchase exceeds permitted authority or concurrent requests exhaust the budget | Deny or seek trusted approval; reserve aggregate exposure atomically | Budget reservation and allow/deny records, without secrets |
Wallet lacks the required token balance or transaction gas | Do not fulfill; retain the purchase association and reconcile any uncertain submission before replacement | Wallet failure and original transaction/status evidence, where present |
Order creation response is lost | Block another create until the original outcome is reconciled | Durable business claim, attempt details, recovered order association |
Polling stops or payment remains pending/held | Inspect the same purchase; do not interpret a helper return as fulfillment permission | Status history and method-specific acceptance decision |
Payment is accepted but the API response fails | Recover delivery or follow an agreed compensation process, not a fresh charge | Separate payment and delivery states plus saved result/recovery record |
Duplicate webhook, request, or worker restart occurs | Reuse the original purchase and prevent duplicate business fulfillment | Deduplication/consumption decision and once-only result association |
Test payment signals, not just successful function returns. The GOAT Flow SDK reference documents that a polling helper can return a failure state. Card orders can also remain held at PAYMENT_CONFIRMED; a Crypto example's success condition is not a universal Card rule. Use the completion contract for the selected surface and payment method.
Ordinary order completion uses INVOICED; Checkout Session completion uses COMPLETED. The helper stops at PAYMENT_CONFIRMED rather than waiting through a Card hold, so continue safe status reads or follow the applicable authenticated completion event. Still check purchase eligibility and delivery ownership before releasing the resource.
Proof labels need equal care. The SDK's server-issued payment record has a historical signature field documented as an unsigned hash. It is not interchangeable with a signed Payment-Receipt from the separate GOAT Flow MPP profile. A transaction hash is a correlation key, not sufficient authorization to release a purchased resource.
Webhook delivery must be authenticated according to the selected deployment's contract. A plausible event body cannot authorize fulfillment. Re-read trusted status when required, match merchant and purchase details, and make polling and event-driven delivery converge on the same durable operation. Neither an extra callback nor a new worker should create a second sale.
Distinguish replay protection at different layers. A wallet nonce can constrain a transaction; a payment verifier can reject invalid payment material; your service still needs to prevent the same accepted evidence from granting unintended access. Retrieving one's already purchased result and purchasing a second unit are different operations. Define that difference before choosing the retry behavior.
Refunds and support also need owners. A failed handler does not automatically reverse a Crypto transfer, and a cancelled order is not evidence that money was returned. Agree on delivery recovery, eligibility for compensation, approval authority, and the records needed to resolve a dispute. Evaluate total operating cost, including failed requests and reconciliation, rather than comparing only nominal network fees.
None of these tests was executed for this guide. A verified implementation should publish its dependency/environment record, redacted payment challenge, actual allow/deny output, order/transaction associations, and delivered result where disclosure is authorized. Missing evidence should remain a release task, not become a fabricated successful log.
Choose the Smallest Stack That Owns Your Unresolved Work
For a new paid endpoint, begin with a compatible seller SDK and an explicit verification/settlement choice. A hosted facilitator can reduce operating work; self-operation is appropriate only when the team accepts that responsibility. For an existing edge deployment, first establish Cloudflare eligibility or CloudFront/WAF fit before redesigning the origin.
Evaluate GOAT Flow when merchant orders, payment confirmation, reconciliation, and application-level delivery coordination are part of the requirement. Its specific value is a documented commercial workflow around paid operations, not being the official or exclusive implementation of x402. If your existing system already handles those obligations well, adding a second order system may create more reconciliation work than it removes.
Add discovery separately when agents must locate unfamiliar services. Bazaar can expose structured resource information through supporting integrations, but an arbitrary endpoint returning 402 does not automatically become listed, recommended, or purchased. Verify that the intended client can discover the actual listing and understand its schema and terms.
The final selection should leave no ambiguous owner: who sets the price, who authorizes spending, who verifies payment, who records the purchase, and who recovers an undelivered result. Choose providers after assigning those jobs, then validate one complete purchase and its failure paths. That produces a defensible architecture without pretending every component must come from the same company.
FAQ
Do I need a hosted facilitator to accept x402 payments?
Not necessarily. Verification and settlement can be self-operated where the chosen implementation supports that approach. A hosted service outsources those duties; it does not eliminate their compatibility and recovery requirements.
Can I charge an agent without creating a conventional customer account?
Payment-gated access can avoid a separate signup for suitable public resources. It does not remove required access controls, purchase correlation, abuse prevention, or any identity obligations relevant to the service. Do not treat GOAT's authenticated Custom Integration example as proof that every integration is automatically accountless.
Does Bazaar make every paid API discoverable?
No. It provides discovery mechanisms through supporting implementations and metadata. Actual registration, listing, schema visibility, and client use still need verification; discovery is not a purchase guarantee.
Is GOAT Flow MPP interchangeable with a standard x402 SDK?
No such general equivalence should be assumed. MPP is a separate protocol, and GOAT's API Payments documentation specifies a deployment-matched MPP integration profile. Use the selected client/verifier contract and test the exact combination rather than mixing payment payloads or receipt formats.


