Cards extend agent reach, stablecoins settle value, and x402 prices HTTP resources. Map all three to authorization and verified fulfillment.
Meta Description: Cards extend agent reach, stablecoins settle value, and x402 prices HTTP resources. Map all three to authorization and verified fulfillment.
Slug: ai-agent-payments-card-crypto-x402-layers
An AI agent can pay through card infrastructure, send crypto from a wallet, or use x402 to unlock a paid digital resource. Placing those options in one flat comparison obscures their different jobs. A card is a credential accepted by an existing payment network. A stablecoin is an asset that can move onchain. x402 is an HTTP payment protocol that lets a server describe a payment requirement and lets a client satisfy it as part of a resource request.
A single purchase can use more than one of these layers. An agent might receive a tightly scoped card credential to buy from a conventional online store. It might send a stablecoin directly to a merchant wallet. Or it might receive an HTTP 402 response, authorize a stablecoin payment, and retry the request with payment evidence. The correct choice depends less on the label and more on four questions: who authorized the purchase, what the agent presents, how value settles, and what evidence permits fulfillment.
That distinction matters for both agent developers and merchants. A payment can be technically successful while the purchase remains unauthorized, unmatched to an order, duplicated, or undelivered. The payment method is only one part of the transaction.
Three labels, three different layers
The phrase "AI agent payments" covers several functions that conventional checkout often hides behind one button. Separating them prevents category mistakes. A delegated card credential provides access to existing card commerce, but does not establish agent identity, task authority, or service delivery. A direct crypto payment moves a token under wallet authorization, but does not by itself define the product, refund rules, or fulfillment. x402 communicates payment requirements and evidence for an HTTP resource, while leaving custody, policy, settlement, and merchant operations to other components.
The differences become clearer when each option is described by its place in the transaction.
Cards sit at the payment-presentation layer. The agent presents a credential that a merchant's existing processor can authorize. The underlying consumer funding source may be a card or bank account, but the merchant sees a familiar card-network transaction.
Crypto sits at the value and settlement layer. The agent controls or has delegated access to a wallet, selects an accepted asset and network, signs a transaction, and transfers value. The transfer can be verified onchain, but it still needs to be associated with the correct commercial obligation.
x402 sits at the application protocol layer. The seller attaches payment terms to an HTTP resource. An unpaid request receives 402 Payment Required; a compatible client evaluates the terms, pays through a supported payment scheme, and retries. The x402 Foundation describes x402 as an open, neutral standard for internet-native payments, not as a coin, wallet, or settlement network.
This means "card versus crypto versus x402" is not always a valid either-or decision. A more useful design question is: which combination gives the agent a usable credential, gives the merchant an accepted settlement path, and binds payment to delivery?
The four decisions inside every agent purchase
Every purchase initiated by an agent needs a complete chain of authority and evidence. Four decisions define that chain.
1. Purchase authority
Who is the principal behind the agent, and what has that principal allowed it to buy? Authority may come from a human approval, an enterprise procurement policy, a prepaid task budget, or a standing rule limited by merchant, amount, asset, time, or category.
Wallet access or a card credential does not answer this question. It only gives the agent technical capacity to present or move value. A well-designed system checks the current purchase against policy before releasing the credential or signing the transaction.
2. Payment presentation
What does the merchant or resource server receive? It could be a one-time card, a network-specific token transfer, or payment evidence encoded for an x402 exchange. Presentation must match the seller's acceptance interface.
An agent with USDC on one network cannot assume a merchant accepts that asset on that network. Likewise, a general-purpose card credential may still fail if it is restricted by amount, geography, merchant category, or issuer controls.
3. Settlement
How and when does value become available to the merchant? Card authorization, capture, payout, reversal, and chargeback are distinct events. A direct stablecoin transfer follows the selected chain's confirmation and finality model. An x402 exchange uses an underlying payment scheme and network; x402 coordinates the exchange but does not replace settlement.
4. Fulfillment evidence
What proves that the merchant may release the product, API response, or service? A browser success screen is not enough. Neither is an arbitrary transaction hash. The merchant needs trusted evidence bound to the expected order, payer terms, recipient, amount, asset, network, and transaction identity.
This four-part model exposes where failures belong. A declined card is a payment-presentation failure. A stablecoin sent on the wrong network is a settlement-path failure. A paid request that times out before the result is returned is a fulfillment and recovery failure. Treating them all as "payment failed" makes recovery harder and can cause duplicate charges.
Path one: an agent uses a delegated card credential
Cards are useful when an agent needs to buy from merchants that already accept card payments and have no machine-native payment endpoint. The agent does not need unrestricted access to the user's card details. Instead, a wallet or issuing platform can provide a credential scoped to a specific spend request.
Stripe's April 2026 description of its agent-payment products illustrates this model. A user can authorize an agent to request a one-time-use card or Shared Payment Token backed by payment methods in the user's Link wallet. Stripe says the agent does not receive the user's raw payment credentials, and the spend request can include controls such as amount, currency, and merchant. At the time of that announcement, each Link spend request required human review before the credential was shared with the agent. That is a concrete example of delegated card access, not evidence that every card system supports autonomous purchasing. Stripe documents the flow here.
A typical card-backed agent purchase looks like this:
The agent identifies a product and constructs a proposed order.
The principal or policy engine evaluates merchant, amount, currency, and purpose.
An issuing or wallet service returns a scoped card credential after approval.
The agent submits that credential through the merchant's existing checkout.
The processor and issuer authorize the transaction.
The merchant creates or updates the order and applies its normal fulfillment rules.
Capture, payout, possible reversal, and reconciliation continue through card infrastructure.
The major advantage is reach. An agent can transact with a large installed base of merchants without requiring each one to add an onchain wallet or x402 middleware. Cards also come with mature fraud, refund, and dispute processes, although those processes create operational cost and delayed certainty.
The limitations follow from the same design. Card checkout often assumes browser interaction, customer details, risk checks, and merchant-specific flows. Authorization can be reversed later. Very small per-request payments may be uneconomic. An agent also needs a secure way to obtain and use a constrained credential without exposing the principal's broader account.
Consider a travel assistant buying a $180 hotel reservation. The hotel already accepts cards, needs guest and booking information, and may support cancellation. A scoped card credential fits the merchant interface and the purchase's dispute expectations. x402 would add little unless the hotel exposes a machine-priced API resource as a separate product.
Path two: an agent sends a stablecoin directly
Direct crypto payment changes the interface. Instead of presenting a credential to a card processor, the agent signs a transaction from a wallet. The merchant specifies an accepted chain, token, amount, and receiving address. The transfer can settle directly to that address after network confirmation.
The flow is programmable, but it is not self-describing unless the merchant supplies enough order context:
The merchant creates a priced order or payment request.
The agent checks the requested token, chain, recipient, amount, expiration, and reference.
A spending policy verifies that the purchase is authorized and that the wallet has token and gas balances.
The agent signs and broadcasts the transfer.
The merchant or payment service watches for the transaction and validates its terms.
The merchant binds the validated payment to the order and fulfills once its confirmation policy is satisfied.
This path can work well for crypto-native services, cross-border digital products, or merchants that want funds delivered to their own wallet. It also makes transaction evidence independently observable onchain. Yet onchain visibility does not prove what was bought, whether the service was delivered, or whether a transfer should be refunded.
The failure cases are specific. An agent can select the wrong network, use the wrong token contract, send an incorrect amount, allow a quote to expire, lack native gas, or broadcast successfully while merchant status polling fails. Transfers are not automatically reversible. The merchant therefore needs an order record and a recovery policy for overpayment, underpayment, duplicate transfer, and paid-but-undelivered states.
GOAT Flow's current public crypto merchant path is an example of this model. Its merchant documentation describes DIRECT ERC-20 transfers to a merchant-configured receiving address, with server-side order tracking and reconciliation. Supported networks, assets, limits, addresses, and capabilities must be read from the active Portal, API, challenge, or manifest rather than inferred from repository examples. The GOAT Flow Merchant Guide also makes the operational layer visible: receiving configuration, orders, payment status, webhooks, API credentials, and reconciliation surround the transfer itself.
Path three: x402 coordinates payment with the resource request
x402 is strongest when the product is naturally represented as an HTTP resource: an API response, data query, model inference, MCP tool call, file, or protected content item. It moves price discovery and payment instructions into the request-response exchange.
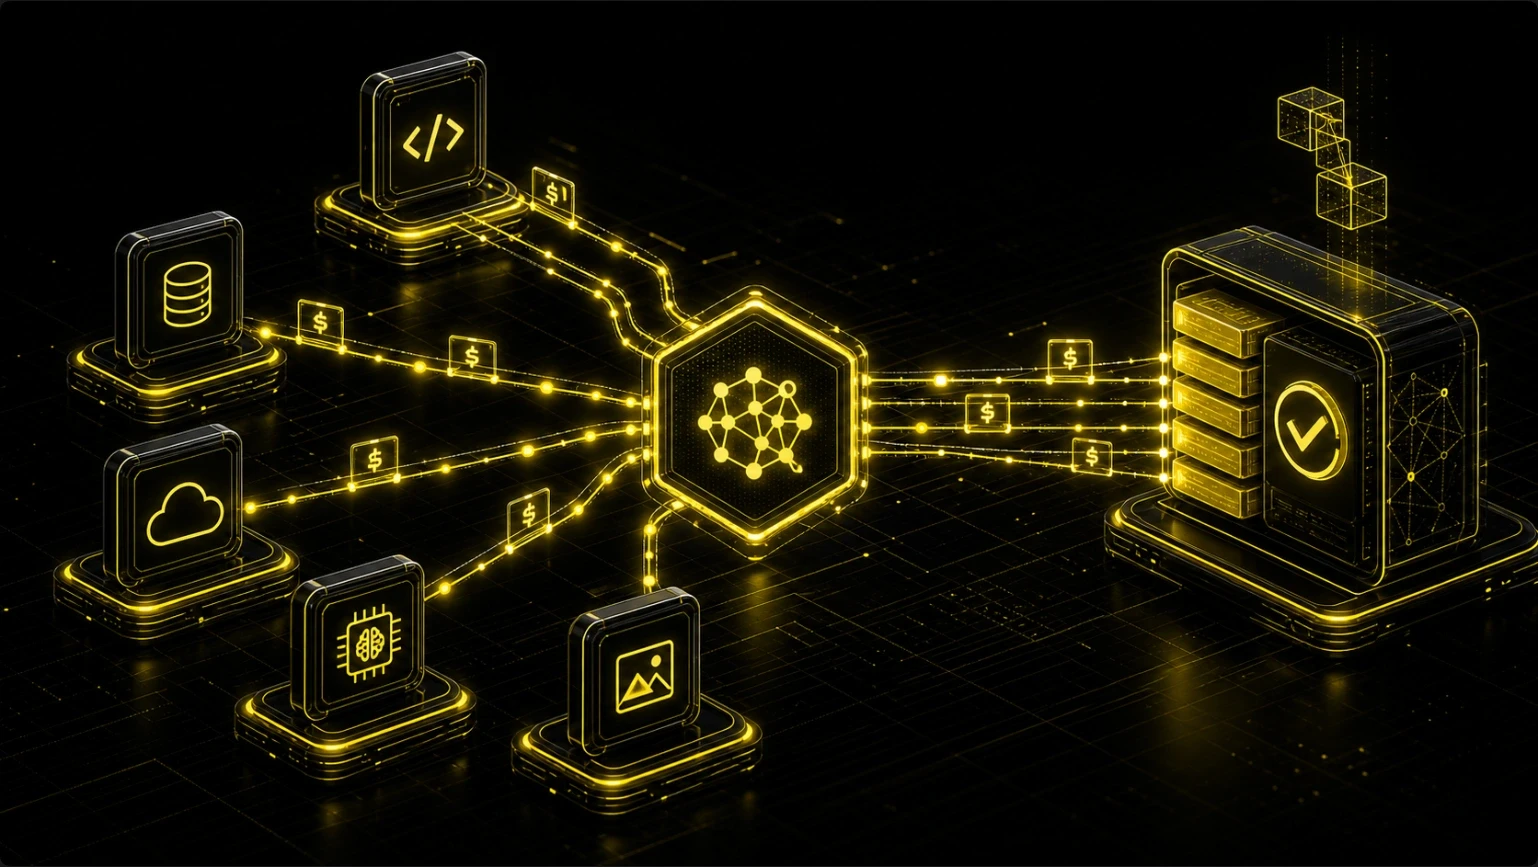
A simplified x402 purchase proceeds as follows:
The agent requests a paid resource.
The server returns
402 Payment Requiredwith structured payment requirements.The agent evaluates the resource, price, accepted scheme, network, asset, and expiration against its policy.
The agent creates the required payment using its wallet or payment provider.
The client retries the request with the payment payload or proof.
The server or facilitator verifies the payment and settles it according to the selected scheme.
The server returns the protected resource when verification succeeds.
The critical addition is not merely a new way to transfer stablecoins. It is the binding of a priced resource and its payment requirement to an HTTP interaction. That makes per-request commerce easier to automate than a flow that sends funds first and asks the merchant to infer what the transfer purchased.
Imagine a research agent requesting a $0.04 company-risk score. A subscription could force the agent's operator to create an account and pre-commit to a plan. A direct wallet transfer could move $0.04, but the data provider would still need to associate that transaction with the exact query. With x402, the endpoint can return the price and payment terms for that request, then release the response after valid payment evidence is supplied.
x402 does not remove the need for authorization. The agent still requires a wallet, key-management model, supported asset, sufficient balance, gas or sponsored transaction path, and spending policy. The server still needs replay protection, payment verification, idempotent fulfillment, and a recovery path if payment succeeds but computation fails.
Nor does x402 necessarily replace identity or API keys. An account-light public data endpoint may use payment as its access gate. A regulated, personalized, quota-sensitive, or permissioned service may still require identity and authorization in addition to payment. Payment proves that terms were satisfied; it does not automatically prove who the client is or what data it may access.
One merchant can expose several entry points without merging their rules
A business may serve human customers, shopping agents, and software agents from the same commercial operation. That does not mean every buyer should use the same interface.
Consider a hypothetical market-intelligence company with three offers:
a $49 downloadable industry report for human buyers;
the same fixed-price report exposed through a machine-readable product link;
a $0.04 risk-score API for agents making many one-off requests.
The human report buyer may prefer a hosted checkout with card or crypto options. An agent buying a fixed-price report needs structured product and payment terms it can inspect without interpreting a visual page. The API customer needs a request-level challenge and a response bound to payment verification. All three purchases can feed shared order, transaction, and reconciliation records, but their acceptance and fulfillment proofs differ.
This is where a product such as GOAT Flow is relevant. GOAT Flow presents Checkout for stores and platforms, QuickPay for sellers and creators, and API Payments for API providers. Its product page also describes card payments through Stripe and cryptocurrency payments to merchant wallets. QuickPay can expose a hosted page plus machine-readable discovery surfaces, while paid resource integrations can serve programmatic clients.
The important boundary is that GOAT Flow is the commerce product, while x402 is a broader HTTP payment protocol used by relevant payment surfaces. They are not interchangeable names. A merchant can use GOAT Flow to coordinate buyer interfaces and merchant operations while still preserving different rules for card authorization, direct crypto settlement, and paid API access.
The merchant also needs one canonical order state. If a human sees a successful browser screen, an agent receives a payment receipt, and an onchain transfer is visible, those observations should resolve to server-trusted records before fulfillment. Otherwise the business risks delivering twice, delivering against the wrong payment, or refusing a legitimate paid order because two systems use different identifiers.
Payment permission is not purchase permission
Giving an agent a wallet or a payment credential answers "can it pay?" It does not answer "should it make this purchase?" Production systems need controls on both sides of the transaction.
On the buyer side, policy should normally bind authorization to more than a maximum balance. Useful constraints include:
merchant or recipient allowlists;
per-purchase and per-task limits;
accepted currencies, tokens, and networks;
time windows and quote expirations;
product category or endpoint restrictions;
cumulative daily or workflow budgets;
approval thresholds for unusual purchases;
retry budgets and duplicate-payment detection.
On the merchant side, fulfillment logic should verify the expected commercial terms. For a crypto order, that means checking the merchant and order identifiers, recipient, chain, token contract, amount, transaction identity, and accepted status. For an x402 resource, payment proof also needs to be bound to the intended request and protected against replay. For card purchases, authorization and capture state must be reconciled with the order and the merchant's delivery policy.
Idempotency connects both sides. An agent may retry because the network timed out after payment. A webhook may be delivered more than once. A server may verify the same receipt during repeated resource requests. Stable identifiers and idempotent fulfillment let the system return the existing result or order state rather than charging or delivering again.
Paid-but-undelivered cases require an explicit policy. If model inference fails after payment, the service might retry without a second charge, return stored results, issue a credit, or start a refund workflow. The right response depends on the payment path and product. Card reversals, onchain refunds, and x402 request retries have different mechanics. They should not be hidden behind one generic error message.
GOAT Flow's integration guidance applies the same principle to merchant delivery: browser onSuccess is a user-experience signal, not payment proof, and a transaction hash alone is not a fulfillment decision. Merchants should rely on a trusted backend status, a deployment-verified webhook contract, or the applicable signed receipt, then make fulfillment idempotent. This is a product-specific implementation of a general rule: release value only when payment evidence is bound to the expected order or resource.
Choose from the transaction backward
There is no universal winning option. Start with what is being purchased and what the seller can accept.
Use delegated card infrastructure when the agent must reach conventional merchants. This is often the practical route for travel, procurement, retail, and services already built around card checkout. Require scoped credentials and explicit spend controls. Account for declines, fraud review, capture timing, reversals, and merchant-specific checkout requirements.
Use direct crypto payment when both parties can coordinate a wallet transfer and the product benefits from onchain settlement. Define the chain, token, amount, recipient, expiration, order reference, confirmation policy, and refund process. Do not treat transfer visibility as delivery proof.
Use x402 when the commercial unit is an HTTP resource and request-level payment is valuable. APIs, MCP tools, data, inference, and digital content are natural candidates. Confirm that the buyer supports the required payment scheme and that the server can verify payment, prevent replay, and recover from paid execution failures.
Combine entry points when the merchant serves both humans and agents. Shared order operations can sit behind hosted checkout, machine-readable fixed-price offers, and paid API routes. Keep the acceptance rules and proof requirements explicit for each surface.
A practical architecture review can use this sequence:
Define the purchased unit: cart, booking, file, API call, tool execution, or outcome.
Identify the principal and the exact delegated authority.
Determine what the merchant already accepts.
Select the credential or wallet the agent can safely use.
Define the settlement event that changes the order state.
Specify the evidence that releases fulfillment.
Design retries, duplicate handling, refunds, and reconciliation before allowing unattended execution.
This method may lead to cards for broad merchant reach, direct stablecoins for crypto-native orders, x402 for request-level services, or a product that supports several surfaces. The decision follows the transaction instead of a technology preference.
Teams evaluating a mixed human-and-agent commerce model can explore GOAT Flow to examine how Checkout, QuickPay, API Payments, and merchant operations are separated in the current product. Whatever implementation is chosen, the decisive test remains the same: the system must know who authorized the purchase, what was paid, which obligation it satisfied, and what evidence permits delivery.
FAQ
Can an AI agent pay with a credit card?
Yes. An agent can use a delegated, scoped card credential supplied by an issuing or wallet system. That does not mean the agent should receive the user's raw card details or unlimited spending authority. The credential may be limited by merchant, amount, currency, time, or explicit human approval.
Are AI agent crypto payments always made with stablecoins?
No. Stablecoins are common because they provide a relatively stable unit for pricing, but the accepted asset depends on the merchant, network, payment scheme, and active product configuration. The agent must validate the exact token contract, chain, amount, and recipient before signing.
Is x402 a cryptocurrency or blockchain?
No. x402 is an HTTP-native payment protocol. It communicates payment requirements and proof between a client and server. The underlying payment can use a supported blockchain and stablecoin, but those are settlement components rather than x402 itself.
Does x402 eliminate the need for accounts and API keys?
It can reduce account and credential requirements for payment-gated public resources, but it does not eliminate them in every service. Personalized, regulated, private, or role-restricted APIs may still need persistent identity and authorization in addition to payment.
Can one merchant accept both card and crypto payments from agents?
Yes, if its commerce infrastructure exposes compatible buyer interfaces and keeps order state consistent. The card and crypto paths still have different authorization, settlement, reversal, and verification rules. A unified dashboard does not make the underlying transactions identical.
What should a merchant verify before fulfilling an agent order?
The merchant should use a trusted backend record or applicable signed receipt to verify the expected order or resource, amount, asset or currency, recipient, payment identity, and accepted status. A browser success message or unverified transaction hash is not sufficient by itself.