Build a reliable payment verification boundary for AI agent orders using evidence binding, explicit order states, idempotent fulfillment, and recovery.
Meta Description: Build a reliable payment verification boundary for AI agent orders using evidence binding, explicit order states, idempotent fulfillment, and recovery.
Slug: ai-agent-payment-verification-before-fulfillment
Payment verification should authorize a specific fulfillment action, not merely confirm that money moved. Before delivering an API result, report, license, or digital product to an AI agent, a merchant needs trusted server-side evidence that binds the payment to the correct merchant, order, amount, asset, recipient, and deliverable. The merchant must then claim that delivery exactly once.
That distinction matters because several events may look like payment success without proving that an order is fulfillable. A checkout page can display success before a merchant backend has verified the order. A wallet can return a transaction hash for a transfer that later fails or pays the wrong recipient. An authentic webhook may be delivered more than once. A final onchain transfer does not prevent the paid service from timing out.
The production boundary is therefore:
Verified payment evidence + exact obligation match + one successful fulfillment claim = permission to deliver.
This article develops that boundary as an operational model. It focuses on the handoff from verification evidence to order state, exactly-once fulfillment, and recovery. It does not retell the general x402 request-and-payment sequence.
Define the fulfillment predicate before accepting payments
A fulfillment predicate is the complete set of conditions that must be true before a merchant performs an irreversible business side effect. It should be explicit enough to become a database constraint, transaction boundary, or policy rule.
For an order-based purchase, a practical predicate is:
The exact fields vary by product. A fixed-price research report may bind one order to one download entitlement. An inference service may bind a payment to a model, input digest, maximum compute budget, and result identifier. A paid API route can instead bind access to a canonical HTTP method and route.
Payment verification answers a commercial question: did this payment satisfy this obligation? A transaction hash answers a narrower one: which transaction should be inspected? A successful chain receipt still does not prove that the token, amount, destination, order reference, and permitted deliverable all match.
This is also why a browser callback should never be the authority for fulfillment. Browser state is controlled by the client, can be interrupted, and may be replayed. It is useful for displaying progress. It is not a merchant-side authorization decision.
Use an evidence ladder instead of one “paid” boolean
Payment events have different evidentiary value. Treating all of them as equivalent makes duplicate delivery and mismatched payments much more likely.
Signal | What it can establish | What it does not establish |
|---|---|---|
Agent intent or signed request | The buyer intended to purchase under stated parameters | Funds moved or the merchant received value |
Wallet submission result | A transaction was submitted and has an identifier | Confirmation, correct commercial terms, or delivery authorization |
Transaction hash | A transaction can be located | That its asset, amount, recipient, and obligation are correct |
Onchain receipt or transfer event | A transfer executed under observed chain conditions | That it belongs to the expected merchant order or permits a particular deliverable |
Authenticated order status | The payment system associated evidence with an identified order and state | That the merchant's service has executed or the customer received the result |
Authenticated webhook | The sender reported a state transition | Uniqueness; webhook deliveries can be retried or arrive out of order |
Signed, route-bound access receipt | The presented receipt passed defined issuer, audience, route, and expiry checks | That a downstream tool completed correctly |
Merchant fulfillment record | A delivery claim or result was recorded | Payment truth unless linked to independently verified evidence |
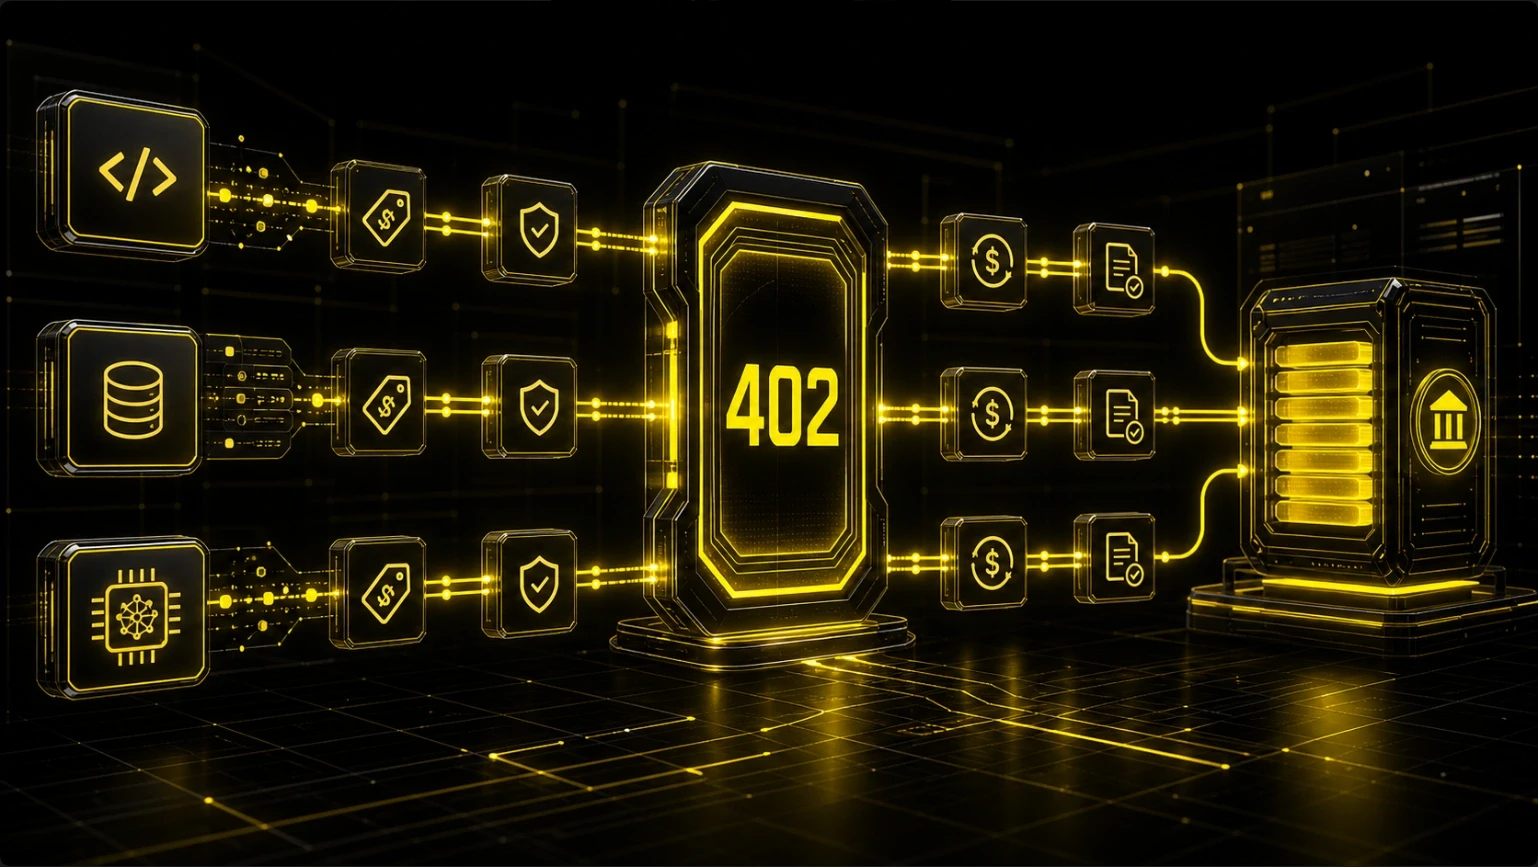
The x402 protocol documentation places payment verification and settlement between a payment requirement and access to the protected resource. That protocol boundary is necessary, but a merchant still owns the business rules after verification: what is delivered, whether delivery can be repeated, and how a paid failure is resolved.
Two principles follow.
First, use the strongest available server-side evidence for the surface being sold. An order status from an authenticated merchant API and a signed receipt presented to a protected route can both authorize work, but they are not interchangeable.
Second, keep evidence monotonic. A later, stronger signal may advance an order, but a delayed browser event or duplicated webhook should not move a delivered order backward or trigger another delivery.
Keep payment state and fulfillment state in separate ledgers
One status field cannot accurately represent both money movement and service delivery. “Paid” and “delivered” are facts owned by different systems and can diverge legitimately.
A payment ledger might contain:
A fulfillment ledger might contain:
The join between them is a durable authorization record. When the payment predicate passes, the merchant creates or advances a fulfillment record to READY. A worker then atomically changes READY to CLAIMED before calling an external model, generating a license, exposing a download, or shipping an item. Only one worker can win that transition.
This design can represent operational states that a single “paid” field cannot:
PAYMENT_VERIFIED + EXECUTION_FAILED: the buyer paid, but the service failed before producing a valid result.PAYMENT_VERIFIED + DELIVERY_UNCERTAIN: the result may have been sent, but the acknowledgement was lost.PAYMENT_EXPIRED + NOT_AUTHORIZED: no qualifying payment was observed during the purchase window.PAYMENT_LATE_REVIEW + NOT_AUTHORIZED: value arrived after expiry, so automated fulfillment is suspended pending policy.PAYMENT_VERIFIED + DELIVERED: both the financial and business obligations have completed.
Do not rewrite PAYMENT_VERIFIED to “failed” because an inference job crashed. That destroys financial truth. Likewise, do not mark an order delivered simply because payment verification passed. The two-ledger model preserves evidence for retries, refunds, support, and reconciliation.
Checkout orders need authenticated status plus obligation binding
For a checkout or merchant order, the authoritative input should come from a trusted backend channel: an authenticated order-status query or a deployment-confirmed, authenticated webhook. The server then validates the returned fields against its own order record before opening the fulfillment gate.
Current GOAT Flow documentation illustrates this pattern. Its server-side order waiters treat PAYMENT_CONFIRMED and INVOICED as successful terminal states, while FAILED, EXPIRED, and CANCELLED terminate unsuccessfully. The documentation also warns that a poller may observe only INVOICED because a DIRECT order can advance from PAYMENT_CONFIRMED within one watcher transaction. Merchants should therefore treat the documented successful set as a set, rather than wait for one intermediate status that may not be externally visible. See the current GOAT Flow Merchant Guide before implementing against a deployment.
A successful status is still only one input. Before fulfillment, compare the authenticated record with the merchant's expected obligation:
Merchant and environment identifiers
Internal order or client reference
Expected chain and token contract, not only a display symbol
Required amount and any permitted tolerance
Merchant receiving address
Transaction hash and, where relevant, log identity
Product, service, quantity, or entitlement
Expiration and late-payment policy
Consider a merchant selling a fixed-price research report. The checkout shows success and supplies a transaction hash. The backend later retrieves an authenticated INVOICED order. The merchant should not generate the download token until the order identifier, price, asset, recipient, and transaction all match the stored report order. After they match, the backend claims a fulfillment key such as report-order:<order_id>. Every webhook retry or status poll resolves to that same key and returns the existing delivery result.
This is stronger than “wait for confirmation” because confirmations address chain confidence, while obligation binding addresses commercial correctness.
Webhook handling requires the same discipline. Verify the webhook contract and signature for the active environment, store an event identifier or payload digest, and process state changes idempotently. Do not assume one universal GOAT Flow event-name list: current repository guidance explicitly says deployment behavior is authoritative for event names, payloads, signatures, and retries.
Paid API access uses a different verification path
Per-request APIs have a tighter execution boundary. The verifier can sit directly in front of the protected handler and decide whether this request is authorized to run. Instead of resolving a persistent order and then delivering an entitlement, middleware validates payment evidence bound to a resource.
GOAT Flow's current MPP-profile paid-route integration is a concrete example. After payment verification, the buyer receives a signed Payment-Receipt and presents it to the merchant route. The documented middleware checks the receipt signature, merchant audience, canonical route binding, expiration, and, when enabled, whether the receipt identifier has already been consumed. These are described in the GOAT Flow MPP middleware documentation.
That receipt has a different job from an order status. It can authorize a request to a named route under the receipt's constraints. It should not be described as a universal x402 receipt format, nor should it be used as generic proof that an unrelated service was delivered. GOAT Flow's current three-segment signed receipt is a GOAT-specific integration extension.
For a paid data endpoint, the fulfillment predicate might be:
Reusable and single-use access create a real tradeoff. A reusable receipt can reduce payment friction for a time-bounded access window, provided its scope is deliberate. A single-use receipt is simpler for one paid invocation, yet its replay store becomes part of the availability path. If the store is unavailable, failing closed protects revenue and duplicate execution at the cost of temporarily denying valid buyers. Failing open preserves availability and introduces a risk of reuse.
In a multi-replica API, an in-memory “used receipt” set is insufficient. Each replica could accept the same receipt. The GOAT middleware documentation therefore calls for a shared store with atomic consumption semantics when single-use enforcement spans production replicas.
Make fulfillment atomic and idempotent
Exactly-once delivery cannot be guaranteed merely by asking agents not to retry. Networks retry, webhooks redeliver, clients time out, workers crash, and queues provide at-least-once delivery. The merchant must make repeated inputs converge on one business result.
The key pattern is claim before side effect:
Normalize the verified obligation and compute a stable fulfillment key.
Start a database transaction or use an atomic compare-and-set operation.
Insert the fulfillment claim only if the key does not exist.
If the claim already exists, return the recorded state or result instead of executing again.
Commit the claim before invoking an irreversible external side effect, or use an outbox/work queue that preserves the claim-to-execution handoff.
Record the result, delivery evidence, and failure classification against the same claim.
The key must represent the commercial operation, not just the incoming HTTP request. For an order, use a merchant-scoped order identifier plus fulfillment type. For a single paid API call, use a verified receipt identifier plus an operation digest. For a retriable inference job, use the order and job specification so a client timeout cannot purchase or launch a second job accidentally.
An atomic claim is not the same as a long database lock around model inference. The claim establishes ownership. A worker lease, heartbeat, and recovery policy can manage long execution. If a worker crashes after claiming but before completing, another worker should resume the same fulfillment record after the lease expires, not create a new one.
Irreversible side effects need an additional boundary. If issuing a software license through a third-party system, send the fulfillment key as that system's idempotency key when supported. If it does not support idempotency, record a durable outbox command, query the provider before retrying, and route ambiguous outcomes to review. “Retry until success” is unsafe when success may have occurred without a response.
Paid does not mean delivered
The hardest failures occur after the payment predicate passes. At that point the merchant has received value, and the service obligation may remain incomplete.
The service times out before producing a result
Keep the payment verified. Mark the fulfillment attempt as EXECUTION_FAILED or retriable, and apply a bounded retry policy to the same claim. The retry budget should reflect the product economics and whether repeated execution can cause additional cost.
For example, an AI inference merchant receives a verified payment and claims job order-781:model-A:digest-X. The model provider times out. A worker retries that job identifier twice. If all attempts fail, the merchant moves it to a resolution state. It does not ask the agent to pay again unless the original obligation has been explicitly resolved.
Execution may have succeeded, but the response was lost
Mark the delivery UNCERTAIN, not failed. Query the downstream provider or result store using the same idempotency key. If a durable result exists, return it. If no reliable evidence exists and repeating the action would be harmful, require review.
The payment arrives after expiry
Expiry should stop automatic execution, but it should not make an observed transfer disappear. Record a late-payment state, retain the transaction evidence, and apply a merchant policy: honor at the original terms, issue a new quote with manual approval, or refund through a separately authorized process. Do not rebroadcast payment or create a second order merely because the original poll timed out.
The webhook never arrives
Webhooks are notification channels, not the only possible source of truth. A reconciliation or polling worker can retrieve authenticated order state and advance the same order. Conversely, receiving a webhook should not bypass field matching or idempotency.
Verification succeeds, but output quality is disputed
Payment verification cannot judge whether a report was accurate or an AI result met quality expectations. Store the input digest, service version, execution timestamps, result identifier, and delivery acknowledgement. Then route the case through the merchant's refund, rerun, or review policy. Do not claim that the payment layer automatically resolves service-quality disputes.
Automatic recovery is appropriate when the operation is deterministic, idempotent, and inexpensive to repeat. Manual review is safer when delivery is irreversible, high value, ambiguous, or tied to a subjective outcome.
Reconciliation closes evidence gaps after the real-time path
Real-time verification decides whether to fulfill now. Reconciliation asks whether the merchant's internal records, payment-system records, and observed transfers still agree later.
Useful reconciliation classes include:
Matched: the order, expected obligation, verified transfer, and fulfillment record agree.
Paid but not delivered: payment is verified, but fulfillment remains failed, pending, or uncertain.
Delivered without matched payment: a severe control exception requiring immediate investigation.
Late payment: value arrived after the normal order window.
Duplicate or reused evidence: one transaction or receipt appears against more than one obligation.
Unresolved: a record exists in one system but cannot yet be matched confidently in another.
GOAT Flow's merchant documentation includes order and reconciliation records, but a reconciliation report should not become the first-line authorization gate for a latency-sensitive purchase. Its value is detecting gaps that the synchronous path, polling, or webhook processing missed.
Each record should preserve the evidence needed to explain a decision. That includes merchant and order IDs, environment, quote terms, payer and recipient, chain and asset, amount, transaction and log identity, and verification source and time. Also retain webhook or receipt identifiers, the fulfillment key, execution attempts, result location, and resolution outcome. Avoid storing unnecessary sensitive request content; identifiers and hashes can often provide correlation without retaining full payloads.
Run a production acceptance test around failures, not just success
A checkout demo that completes once proves very little. Before enabling automated agent order fulfillment, test the state boundary deliberately.
Test | Expected behavior |
|---|---|
Browser reports success before backend verification | No fulfillment occurs |
Valid transaction hash pays the wrong recipient or asset | Predicate rejects the obligation |
| Valid matching order can proceed |
Same authenticated webhook is delivered repeatedly | One fulfillment claim, one result |
Agent retries the same paid API request concurrently | Atomic receipt/operation claim prevents duplicate execution |
Receipt is valid but bound to another route | Protected handler rejects it |
Shared receipt store is unavailable | Defined fail-closed response; no untracked consumption |
Payment confirms after order expiry | Late-payment review state; no blind rebroadcast or delivery |
Worker crashes after claiming execution | Lease recovery resumes the same fulfillment record |
Service succeeds but response is lost | Existing result is recovered using the fulfillment key |
Service exhausts its retry budget | Payment remains verified; case moves to resolution policy |
Test and production credentials are mixed | Environment binding rejects the request |
The launch criterion is not “all payments succeed.” It is that every input produces an explainable state transition, duplicate evidence cannot create duplicate value, and operators can recover ambiguous outcomes without changing financial history.
Merchants evaluating GOAT Flow should confirm current order states, webhook authentication and retry behavior, supported chain and asset configuration, receipt verification keys and algorithms, fee rules, and enabled capabilities in the active environment. Repository examples and documentation describe the integration model, but the live Portal and API remain authoritative for deployment-specific behavior.
Authorize delivery, not just payment
Reliable agent commerce requires a clean boundary between value movement and merchant action. The verifier must bind strong evidence to one exact obligation. The order system must record financial truth separately from execution and delivery. The fulfillment service must claim the work atomically and make every retry converge on the same outcome.
That model works for checkout orders, fixed-price digital products, paid tools, and request-native APIs even though their evidence channels differ. It also gives merchants a defensible answer when something goes wrong: what was paid, what was authorized, what executed, what was delivered, and what must happen next.
For a current implementation example spanning checkout, QuickPay, API payments, and merchant operations, explore GOAT Flow and validate the active environment before enabling automatic fulfillment.


