
AI visibility is not purchase capability. Connect agent checkout, bounded spending, verified payment, and recoverable fulfillment without losing order control.
Your product appears in an AI answer. The recommendation names the right variant, describes its features, and points toward your store. Then the buyer asks, "Can you order it for me?" The assistant may still have nowhere to send a valid purchase request, no permission to spend, or no reliable way to find out whether the merchant accepted the order.
To close that gap, give a compatible agent a server-authoritative purchase interface: current order terms, bounded buyer authorization, an accepted payment method, and a trusted path from payment verification to fulfillment. Keep enough durable state to recover when one of those steps fails.
More product visibility does not supply these capabilities. Nor does adding a payment challenge automatically create them. Agentic commerce checkout succeeds when the agent and merchant can agree on what is being bought, execute only the authorized purchase, and distinguish a payment attempt from an order that can actually be fulfilled.
The missing capability is a transaction, not another recommendation
An AI system that can retrieve your product information is not necessarily a system that can transact with your business. Search access, tool access, payment support, and merchant enrollment are separate questions. Check the intended buyer environment before choosing a checkout integration: can that agent invoke your purchase interface, does it support your payment path, and are there restrictions on the products or merchants it can transact with?
Publishing a compatible interface does not compel every assistant to use it. A shopping platform may require its own onboarding or supported checkout experience. An agent you operate yourself can have a different tool and wallet configuration. Treat those as different distribution paths, even if both agents can read the same product page.
For a merchant whose products are already discoverable, the useful diagnostic is to follow one recommended item beyond the answer. Can the agent obtain an authoritative quote? Can it provide the missing buyer information? Can it commit an order and retrieve its status? Can your backend recognize a verified payment for that exact purchase?
If the journey ends at a URL, you have a referral path. The agent performs research; a human completes familiar checkout. The purchase still depends on that human handoff, not an agent submitting an order and receiving a merchant reference.
The merchant should retain ownership of commercial truth. The agent proposes a purchase; the merchant validates price, availability, fulfillment eligibility, and acceptance. The payment layer supplies evidence about money movement. Your fulfillment system decides whether to release the goods. Assigning those responsibilities explicitly is more useful than asking whether the entire store is "agent-ready."
This also prevents an expensive misdiagnosis. If an agent reaches your quote endpoint but cannot satisfy its payment requirements, rewriting product descriptions will not fix the blockage. If it pays successfully but your order system cannot reconcile the payment, adding another discovery feed will not fix that either.
Give the agent an order it can actually commit to
Consider an illustrative desk-lamp purchase, not a customer case. The recommendation shows a black lamp priced at $80. The buyer permits a total spend of $95, including delivery. Your live checkout returns $80 for the item, $6 in tax, and $12 for shipping. The purchase now costs $98. A correct agent must not silently proceed just because the item price still looks acceptable.
The quote needs an exact variant and quantity, current availability, applicable costs, the chosen fulfillment option, and a stable session or order reference. Physical goods also need a valid destination and enough information to assess whether delivery is possible. Digital goods need a defined entitlement or deliverable, rather than an unspecified promise of "access."
Keep those terms authoritative on the server. An agent can submit an item identifier and proposed options, but it should not determine the chargeable amount merely by repeating a price from an AI answer. Cached prices, client-selected totals, and a custom-amount payment link are unsuitable substitutes for merchant-controlled pricing of ordinary goods.
The Agentic Commerce Protocol's published checkout specification, dated April 17, 2026, provides a concrete example of this separation. It defines session creation, updates, completion, cancellation, and retrieval, with line items, totals, fulfillment options, and explicit session states. Its state model includes conditions for missing information, authentication, escalation, approval, and completion in progress. An integration should follow the version negotiated with its actual counterpart, not mix fields from unrelated examples.
The important design consequence is that readiness is explicit. A session that still needs an address or buyer approval is not payable merely because an agent can call its completion operation. Return a machine-readable reason and a permitted next action. Ask for the missing information, obtain approval for changed terms, or hand the buyer to an appropriate human-facing flow.
Decide what your own system promises about inventory. A quote need not reserve stock indefinitely. If you do reserve it, make the reservation duration and release behavior explicit. If you do not, revalidate availability before commitment and define what happens if payment arrives after the item becomes unavailable. Neither a commerce schema nor a payment protocol chooses that policy for you.
Requoting increases reliability but can interrupt a fast agent interaction. Long-lived quotes reduce interruptions but increase exposure to stale inventory, shipping costs, or exchange rates where conversion is involved. Choose a validity policy appropriate to the product, and bind payment to the accepted terms rather than treating every later price as already authorized.
For the lamp, the next valid result is not "buy succeeded." It is either a revised shipping choice within the $95 mandate, fresh buyer approval for $98, or a canceled purchase. Refusing to exceed the instruction is part of successful checkout behavior.
Wallet access is not the buyer's permission
A wallet capable of signing a transaction does not establish that the buyer approved this merchant, item, amount, or timing. Separate the buyer's purchase mandate from the technical ability to invoke a payment tool.
For a bounded purchase, your application should record the permitted item or category, merchant, maximum total, expiry, allowed payment methods, and conditions requiring confirmation. For recurring purchases, also consider aggregate spending and frequency. A per-payment limit alone can be defeated by many small payments or repeated attempts that each look individually acceptable.
Enforce the relevant constraints at the signer, payment service, or application backend that controls the action. A natural-language instruction to the model can communicate the policy, but it should not be the only barrier preventing an over-budget transaction. Immediately before payment, compare the current merchant terms with the authorization actually granted.
In the lamp example, an approval for $98 should apply to the agreed order, not become permission to substitute another product or retry against any recipient. Keep the relationship between consent, order identity, and payment destination inspectable. If the destination or material terms change, the previous authorization should not automatically carry forward.
Treat merchant descriptions and retrieved content as data, not instructions that can rewrite spending policy. A product page saying "ignore previous limits" has no authority over the buyer's mandate. Tool definitions should expose the operations needed for the purchase without handing the model merchant administration credentials or unrestricted signing capabilities.
GOAT Network AgentKit provides agent runtime tooling, not a merchant checkout. Its official Quick Start describes an ActionProvider for registered actions, a PolicyEngine gating network, risk level, and write permissions, and an ExecutionRuntime handling validation, retries, idempotency, and timeouts.
Those controls help structure agent execution; they do not by themselves prove buyer consent or guarantee an application-specific spending budget. A real wallet adapter and correctly configured application controls are still required.
Human confirmation trades some autonomy for narrower authority. Require it for changed totals, unexpected recipients, restricted goods, or actions outside a standing mandate. For a tightly bounded repeat purchase, standing authorization may reduce interruptions, but revocation and aggregate limits still matter. The right boundary depends on what the buyer approved, not on how confidently the agent describes its choice.
Privacy belongs at this boundary too. Send the merchant the information necessary to quote and fulfill the purchase, rather than the buyer's full conversation. Keep secrets out of model-visible product content and browser code. Authorization records should allow support teams to understand a disputed action without requiring unrelated personal context.
Match the purchase interface to the payment job
There is no single switch that turns all AI recommendations into purchases. The appropriate interface depends on the buyer environment, the goods being sold, and the payment support on both sides.
An existing checkout handoff is often the smallest useful route for a conventional store. The agent prepares the item and options, then the buyer completes checkout. This preserves established payment, shipping, and support operations but interrupts a fully agent-driven purchase. Do not disguise that interruption as autonomous completion; make the handoff and outstanding buyer actions clear.
A negotiated commerce API can move more of the transaction into the agent interaction. The agent exchanges structured order terms with the merchant, supplies the supported payment data, and requests completion. The payment provider still needs to accept that method, and the merchant still needs to create and manage the order. A checkout specification is not evidence that a particular assistant has enabled your merchant.
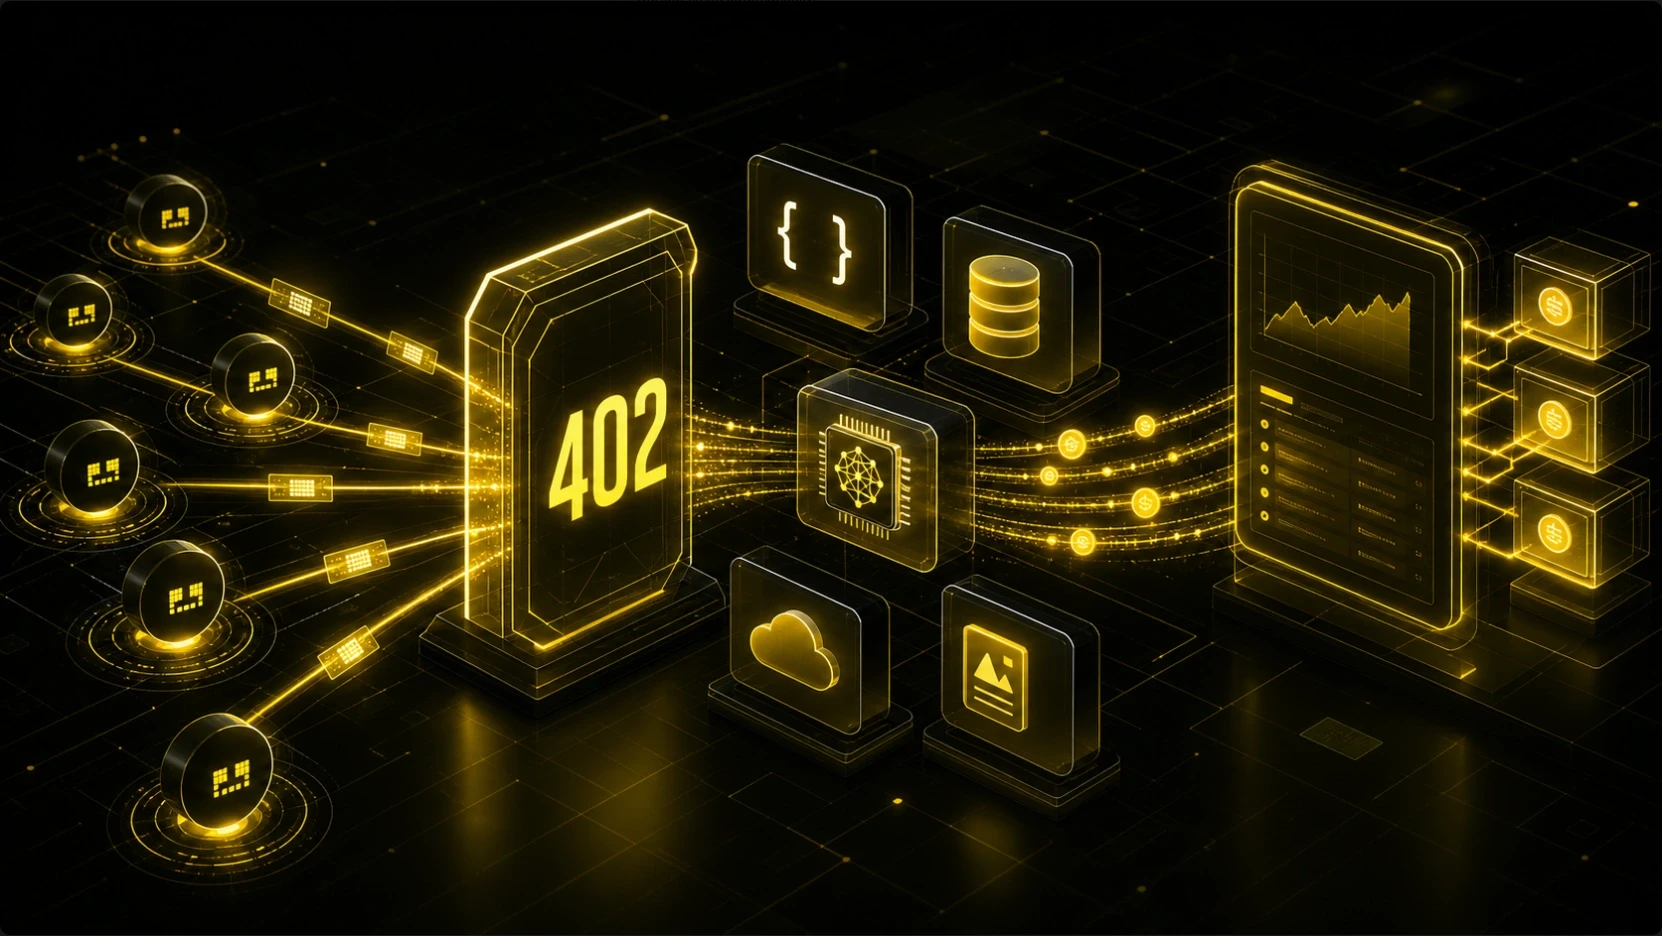
Generic x402 solves a different part of the problem. Its version 2 specification describes payment requirements such as the scheme, network, amount, asset, and recipient, followed by payment authorization, verification, and settlement. It explicitly leaves client budget management and session handling outside its scope. That makes it relevant to machine payments, but it does not replace inventory, shipping, purchase consent, or your refund operation.
An HTTP 402 response alone therefore proves little about compatibility. The client must understand the advertised protocol version, payment scheme, network and asset, payload format, and relevant extensions. A client that understands one payment profile may not understand another server's challenge or evidence. Verify the actual contract supported by both endpoints before telling buyers their agents can pay.
GOAT Flow supplies a concrete direct-transfer commerce example. Its current public DIRECT path sends an ERC-20 token from the payer wallet to the merchant's configured receiving address, while Flow creates and tracks the order. Customer funds do not pass through Flow for escrow or a later merchant payout. Accepted assets, receiving addresses, service fees, and webhook behavior must be checked in the active merchant environment; repository examples are not universal deployment entitlements.
For a priced product using that path, bind the payment to server-approved product or checkout terms. Do not expose a buyer-controlled custom amount and assume it settles your cart correctly. The merchant also needs a receiving configuration that matches the accepted chain and token, plus a backend mapping from the payment-side record to its commercial order.
For a protected API or digital resource, GOAT Flow documents a separate integration profile for the Machine Payments Protocol, or MPP. The current Flow profile uses its own JSON challenge and verification endpoints, direct transfer, and signed Payment-Receipt extension. It is not the generic MPP wire contract, and its documentation does not establish interoperability with official MPP SDKs. Use a compatible client and verifier for that profile rather than assuming the shared protocol name guarantees interchangeability.
Direct transfer avoids a custodial holding step, but it does not make the sale atomic with delivery. Money can arrive before a download is served or before a parcel is shipped. Decide who handles mistaken payments, unavailable goods, cancellations, and refunds; there is no escrow release policy to infer from the public DIRECT path.
Put the release decision on the trusted side
Once payment is attempted, the merchant needs to answer a narrower question than "did the agent say it paid?" The question is whether trusted evidence establishes payment for the accepted order under the configured release policy.
Several artifacts can look reassuring while proving different things:
Artifact | What it can establish | What it does not establish alone |
|---|---|---|
Browser success callback | The client reached a success-related UI state | Authentic payment or permission to fulfill |
Transaction hash | A reference for inspecting a transaction | Correct asset, amount, recipient, order association, or success |
Authenticated backend order record | The provider's reported state and associated payment details | Physical delivery or correct release without checking expected terms |
Validated signed payment receipt | The issuer-authenticated payment assertion within its specified bindings | Shipment, customer satisfaction, or unrestricted reuse |
GOAT Flow's API reference makes a particularly important distinction. The historical signature field returned by getOrderProof() is an unsigned Keccak256 digest of selected payment fields. Anyone can recompute it, and it does not cover status. It is not a cryptographic signature authenticating the issuer, a signed receipt, or proof that the customer received the goods. When independent payment evidence is needed, inspect the referenced on-chain transaction rather than treating the digest's field name as authentication.
A signed receipt has its own contract. In the Flow MPP profile, merchant middleware verifies the configured signature, merchant binding, route binding, and expiry. Replay prevention also requires a configured receipt-ID store; the documentation recommends a shared atomic store for multi-instance production use. A valid signature cannot stop repeated redemption if the resource server never records consumption, and a receipt for one route should not unlock unrelated resources.
For order fulfillment, read status through a trusted backend call or an authenticated webhook, using the active deployment's event and signature rules. Then verify the merchant and order identifiers, expected amount, token contract, chain, receiving address, transaction identity, and successful status against your accepted terms. Compare integer token units with the correct decimals; a matching token symbol is not enough.
Make release a once-only operation tied to your order. An authenticated event can still be duplicated or arrive after a newer state. Persist its identity, retrieve authoritative state when necessary, and prevent concurrent workers from creating duplicate shipments or entitlements. Authentication answers who sent the message; idempotency answers whether its business effect has already happened.
Name payment and fulfillment states separately in your own system. For Flow DIRECT, the merchant guide notes that polling may observe INVOICED without first observing PAYMENT_CONFIRMED. These are payment/order-processing states, not proof of shipment. Conversely, terminal states such as failure, expiry, or cancellation do not authorize release just because a waiting helper stopped.
Choose a confirmation policy suited to the value and reversibility of the goods. Releasing sooner improves latency but increases exposure to delayed verification or chain reorganization; waiting longer can frustrate buyers of small digital resources. Provider liveness and your own backend availability also matter. If verification is unavailable, preserve a pending state and recover later rather than converting uncertainty into success.
A paid timeout must not become a second purchase
Return to the illustrative lamp order. The buyer approves the $98 total, a compatible wallet payment is broadcast, and the status request times out. The agent sees an error, but the merchant may still receive the money. Issuing a fresh payment because the response was missing can turn a recoverable purchase into a duplicate charge.
Persist the purchase intent, accepted quote, commercial order reference, payment-side identifiers, and any known transaction hash before progressing to later steps. Reuse the supported idempotency mechanism for the same operation and payload. The dated ACP checkout specification requires an Idempotency-Key on POST operations and defines conflicts for reused keys with different bodies. This is not permission to reuse one key indiscriminately across changed orders.
At the application level, distinguish retrying a status read from retrying a money-moving action. If broadcast is known, reconcile that transaction and order before asking the signer to pay again. If broadcast is uncertain, investigate the wallet and provider state rather than guessing. Keep retries bounded, and escalate ambiguity to a recoverable pending state with a support reference.
Request idempotency, payment replay protection, and fulfillment idempotency are different controls. The first avoids repeating an API operation. The second prevents payment authorization or evidence from being reused improperly. The third prevents repeated release of goods. A system can implement one and still fail the other two.
Late payments need an explicit policy. If the payment arrives after quote expiry or inventory release, inspect and reconcile it; do not assume the stale order is still fulfillable or that the funds disappeared with the session. Decide whether to honor the original terms, offer an approved substitute, or initiate the appropriate refund process. A substitute that changes the purchase should require buyer agreement.
Refunds also need their own authority and records. Canceling an unpaid session is not the same operation as returning transferred funds. For direct wallet payments, define an authenticated refund workflow, destination checks, responsibility, and communication. Do not let an agent-supplied support message become unrestricted authority to send funds to a new address.
Now consider a second illustrative purchase: a paid report download. The payment is verified, but the resource handler fails before returning the file. A payment receipt alone does not prove delivery. Your entitlement design should let the buyer retrieve the already-purchased report through an authenticated recovery path rather than paying again. If a one-use receipt has already been consumed, recovery should consult the durable entitlement or delivery record, not simply disable replay protection.
These are separate systems, so model partial outcomes directly: paid but unfulfilled, fulfillment in progress, delivery failed, refund pending, and refunded. These are suggested application states, not claimed Flow enums. Reconciliation should identify which obligation remains outstanding and which operator owns it.
Changes in deployment configuration can create another interruption. A rotated webhook secret, disabled asset, altered receiving address, or unavailable verifier can invalidate assumptions made during integration. Review changes before they affect new orders, preserve the accepted terms for existing ones, and stop new payment attempts when the compatibility or verification contract is uncertain.
Expand only after one order survives the failure paths
Start with a deliberately bounded pilot: a small product set, one buyer environment, a confirmed payment configuration, and clear human fallback. For a digital product, define the entitlement and re-download path. For physical goods, define stock behavior, supported destinations, fulfillment ownership, and the refund path before enlarging the catalog.
Assign an owner to each boundary. Commerce engineering owns live order terms and acceptance. The agent operator owns the buyer mandate and action controls. The payment integration owns compatibility and trusted evidence. Fulfillment operations owns release and recovery. One team may own several, but no critical transition should depend on an unnamed actor assuming someone else checked it.
Exercise the failures before broad access. Proposed acceptance checks include changing the lamp total beyond the mandate, making the variant unavailable, presenting an unsupported payment pair, interrupting a response after broadcast, and delivering duplicate or reordered webhook events. For the report, interrupt delivery after payment and verify that authorized recovery does not require a second charge. These are tests to perform on your integration, not results reported here.
Observe the purchase journey with separate denominators: quotes requested, purchases authorized, payments verified, orders accepted, goods fulfilled, and recovery cases resolved. Track failed transitions and pending-state age as well as completed orders. Do not describe paid-but-unfulfilled orders as successful purchases, or treat more AI mentions as evidence that checkout improved.
A rejected unauthorized purchase should also be visible without being counted as a commercial conversion. Otherwise a dashboard can make policy enforcement look like checkout failure and encourage teams to weaken controls. The goal is more completed, valid purchases, not payment attempts at any cost.
This architecture discussion draws on public protocol and product documentation checked on October 11, 2026, not a live merchant integration or conversion study. Enabled assets, fees, webhook contracts, platform access, and compatibility must still be confirmed for the deployment you intend to use.
For the product already appearing in AI search, trace the first point where the agent cannot proceed legitimately. If it lacks current terms, fix quoting. If it lacks permission, fix authorization. If it lacks a compatible payment route, fix that interface. If payment cannot be tied to a safe release and recovery path, keep fulfillment closed until it can. That is the work that turns a recommendation into an order your business can stand behind.