Buyer signup can disappear without removing access controls. Compare accountless API payments and recover paid data results without charging agents twice.
You can sell individual API responses or data lookups without requiring every AI agent to create a vendor account. A compatible client requests a resource, receives machine-readable payment terms, authorizes a bounded payment, and obtains the purchased result through the selected verification flow. x402 middleware, MPP implementations, managed billing products, and GOAT Flow API Payments offer different integration paths. Compatibility, resource permissions, and recovery still need explicit design.
Accountless API payments remove a particular onboarding relationship, not every account or credential involved in commerce. The buyer may still need a wallet or enrolled payment method; the merchant still configures its service. A payment receipt establishes a limited payment fact, not unrestricted access to private data.
The practical goal is one scoped, recoverable purchase. Define what the payment buys, how the current request proves entitlement to it, and how the buyer retrieves that same result if the first response disappears. Solve those questions before advertising a signup-free endpoint.
No Vendor Signup Is a Narrower Promise Than No Identity
An agent can purchase an eligible public resource without opening a billing profile with its seller. That can remove the email verification, subscription, stored card, and per-seller API-key provisioning that a conventional customer might face. It does not make the transaction anonymous or eliminate the systems that authorize money movement.
Separate four relationships. The agent's operator grants spending authority. The payment system authenticates whatever signer, credential, or delegated method the chosen implementation requires. The merchant configures its receiving and payment infrastructure. The resource server decides whether this caller may obtain this particular result. None automatically substitutes for the others.
For GOAT Flow, the Merchant Portal setup requirements include merchant approval and deployment-specific configuration. Paid-route capabilities must be enabled and configured for the chosen merchant and payment path. A buyer not receiving merchant credentials does not mean the merchant has no account, keys, or operational responsibilities.
The distinction is useful for public market data, a document conversion, or a licensed one-off lookup. It is less straightforward for a medical record, a private enterprise document, or another customer's analytics. Payment cannot create access rights the buyer does not possess. Such resources may require authenticated identity and contractual eligibility even if the billing step uses a wallet.
Design a truthful promise: no separate vendor signup for the eligible paid resource, with compatible payment authority and stated access conditions. Do not promise that any agent can pay, that no identity is involved, or that the entire payment-provider relationship disappears.
Sell One Defined Result, Not an Unbounded Route
Consider a hypothetical GET /v1/market-snapshot?asset=BTC purchase priced at 0.05 USDC. The price is an illustrative design assumption, not a GOAT fee or a quote from an existing data provider. The product is one defined snapshot, not permission to call every operation behind /v1/market-snapshot.
Specify the accepted asset, response fields, permitted data use, freshness rule, maximum response size, and error behavior. A historical data export covering hundreds of assets is not the same product as a single-symbol snapshot. If query parameters change cost or licensing, either quote them explicitly through trusted application logic or expose separately priced products/routes that the payment integration can actually represent.
Decide what recovery means before taking money. For a snapshot, retrieving a lost response should normally retrieve the original purchased snapshot, including its original timestamp. It should not silently generate a new current-market result each time. If freshness requires a new result, distinguish that new purchase from recovery of the old one.
Maintain an application-owned purchase association: the normalized request, approved price, accepted payment terms, expected recipient, and eventual result. A purchase identifier can replace some account-based bookkeeping, but possession of a public identifier alone must not unlock a confidential response. Define a secure entitlement or proof-of-control mechanism for retrieval where needed.
These are merchant design fields, not a claimed universal x402 or GOAT receipt schema. They make it possible to answer the later question: does this payment evidence satisfy the purchase currently being requested? Without that association, a valid low-priced receipt can become an accidental pass to a much broader service.
HTTP 402 Starts the Exchange; It Does Not Finish the Sale
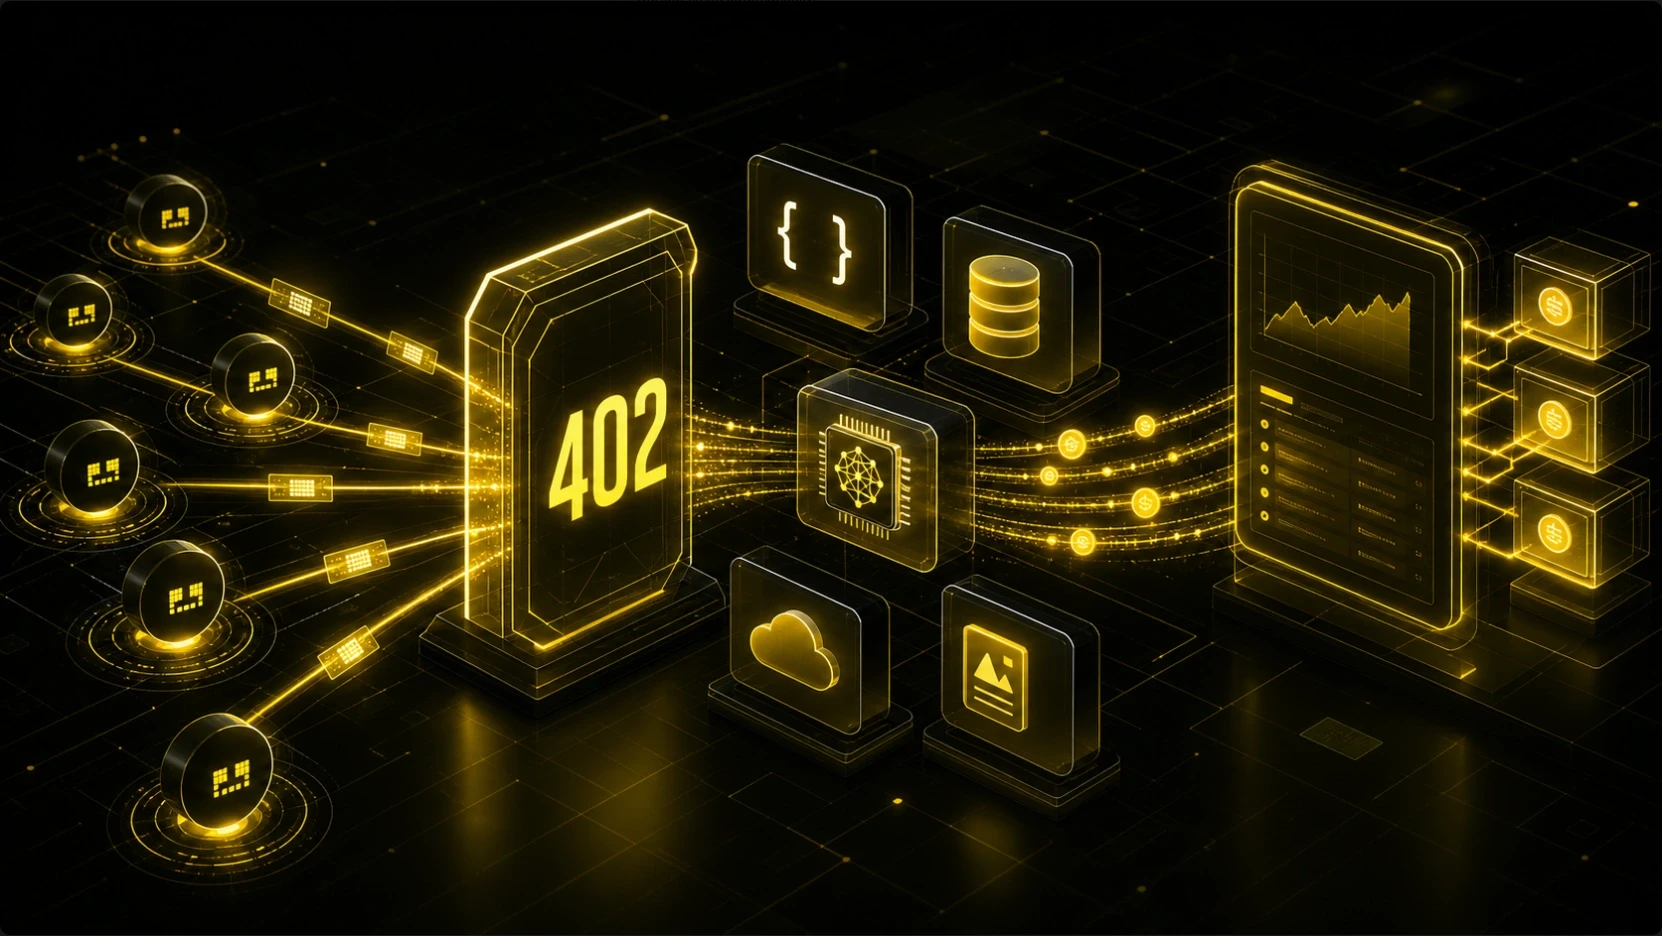
A payment-aware service can respond to a request with HTTP 402 and supported payment conditions. The client interprets the amount, asset, network, recipient, and other required terms for the selected implementation. It must be able to execute that exchange; a general-purpose agent without a compatible payment client does not acquire payment capability by encountering a status code.
Before authorization, the buyer checks the quoted resource and remaining budget through trusted policy. A model's willingness to buy is not the operator's permission to spend. Recipient restrictions, per-purchase limits, aggregate task exposure, and approval requirements belong to the buyer's authorization design, not to a claim of unlimited autonomous payments.
The resource server or its payment infrastructure then validates the submitted payment material. Verification, settlement, and resource execution follow the selected mechanism's ordering. Do not impose one universal settle-before-handler sequence on every implementation. A verified authorization, an observed transfer, an accepted payment, and a delivered result are different states.
The merchant must also define its service response. A priced search result, a downloadable report, and an asynchronous data-enrichment job can all use per-purchase access, but they have different completion and recovery needs. Returning a job identifier can be appropriate for long-running work, provided subsequent access checks preserve the original purchase entitlement rather than requiring another payment for every status read.
Compare the Integration's Buyer Contract, Not Its Label
The following options are not all the same kind of product. x402 and MPP define payment approaches; middleware, gateways, and managed platforms implement particular parts of them. The relevant comparison is what the actual buyer and seller must configure. The statements below reflect official documentation reviewed on October 21, 2026, not executed integrations.
Integration path | What the buyer must support | Seller responsibility and limit |
|---|---|---|
A client, signer, and payment mechanism compatible with the configured resource | Integrate the protected route and verification/settlement path; payment does not automatically supply private-data authorization | |
The payment method and credential exchange accepted by that implementation | Configure the method, price, recipient, and resource; protocol extensibility is not evidence of every payment method or GOAT-profile compatibility | |
The relevant scoped token and configured payment or delegation path | Set up plans and settlement/metering; PAYG and credit bundles differ, and vending an API key is not the same as keyless result access | |
A supported payment exchange and applicable buyer eligibility | Configure eligible edge traffic; reviewed docs specify closed beta and US-based buyers and sellers; origin permissions remain a separate concern | |
GOAT Flow API Payments | A client matched to the selected order or paid-route integration | Configure merchant, payment terms, and enabled routes; enforce result scope and delivery recovery; arbitrary x402/MPP client interoperability is not established |
Nevermined illustrates why an absolute account/credits checklist can mislead. Its technical documentation distinguishes PAYG without credit movement from bundles that burn credits. Payment enrollment, a scoped access token, an API seller's credentials, and a vendor customer login are separate questions. Confirm the specific flow rather than claiming all managed products require a prepaid balance or no setup at all.
MPP likewise should not be reduced to card checkout. Its server documentation provides a concrete charge/credential example with a specified payment configuration. That establishes a possible integration path, not universal support for every rail, identity policy, or client. GOAT Flow's current MPP-labeled profile must be evaluated on its own documented interface.
Choose the simplest compatible approach for the resource. If existing middleware and merchant systems already provide scope, payment correlation, and recovery, another platform is not automatically necessary. If those operational pieces are missing, assess them explicitly instead of judging a solution only by its signup-free headline.
Add a Receipt-Gated Path to the Existing API
GOAT Flow API Payments documents two distinct starting points. Custom Integration leaves authentication, pricing, order creation, and delivery with the merchant backend and uses verified status or authenticated webhooks for the payment result. The paid-route MPP profile instead requires a compatible client to present a verified Payment-Receipt on the protected request.
The latter is relevant to a buyer that should not hold merchant API credentials. However, its JSON challenge/verification endpoints and receipt contract are deployment-specific. Do not substitute generic Foundation middleware or an arbitrary standard MPP SDK and claim the same program works. Confirm the actual client, middleware build, enabled environment, supported chain/token, merchant, and registered route.
For the hypothetical snapshot, the documented Crypto path can be represented as:
This is a documented architecture adapted to an illustrative product, not a running demo. Merchant API secrets stay on the backend. The buyer receives payment terms and the necessary buyer-side evidence, not permission to call administrative merchant APIs.
The verifier must use a trusted configuration for its signature key and merchant/route expectations. A key supplied by the buyer cannot establish that the buyer's own receipt is authentic. The selected contract also determines expiry, replay handling, and any payment-mode restrictions. Keep receipts out of URLs, publicly readable logs, and shared caches; treat their usable access authority as sensitive.
Route setup itself is a prerequisite. Adding middleware to an application does not automatically register or activate the paid route in GOAT Flow. The merchant and operator must enable the applicable capabilities and match the configured identifiers. Public source code or an example package name is not evidence that a compatible production release is available to install.
A Route Receipt Does Not Authorize Every Query
Suppose an agent buys the single-symbol BTC snapshot, then changes the query to request a bulk history export. Both requests may reach the same application handler. A receipt accepted for the route does not necessarily authorize the more expensive data selection. Changing the customer identifier to retrieve someone else's saved report is a more serious version of the same mistake.
GOAT's current route-verification documentation explicitly distinguishes route matching from the current user's identity, URL, query parameters, and body. Its route logic uses exact or colon-delimited prefix matching against configured identifiers; it is not a universal per-field comparison with the paid operation. Do not describe that capability as native signing of arbitrary query parameters unless the actual selected contract supplies and checks them.
The application must validate what is being purchased. Compare the current normalized request against trusted purchase state, including price-affecting inputs and the entitlement being exercised. If an application-owned digest is used to represent those inputs, define its normalization and storage contract; do not invent a native receipt field or assume the middleware checks it for you.
Place checks carefully. Validate request syntax, eligibility, and any required identity or ownership before a single-use receipt is consumed. Apply receipt-dependent business conditions before returning protected data. If consumption must wait for those conditions, integrate verification and reservation with the application's authorization flow instead of assuming a later rejection undoes the earlier consume operation.
That matters even when an adapter supports two-phase processing. GOAT's documentation notes that the framework adapter can commit non-5xx responses, including a business rejection such as HTTP 403. A rejected request is not automatically a released receipt. Test the exact reservation and commit behavior with your business handler.
Payment also does not grant unlimited data rights. Define whether the purchased response may be cached, redistributed, used for a particular task, or accessed only by an eligible principal. State those terms before payment where relevant. A receipt proves neither ownership of the underlying dataset nor permission to disclose another person's records.
Recover Payment and Delivery as Different Operations
The recovery action depends on where the purchase stopped. An unconfirmed transfer needs payment reconciliation. A consumed receipt with a lost HTTP response needs delivery recovery. Treating both as a fresh request can either charge the buyer twice or reopen an access token that was meant to be single-use.
For GOAT's paid-route profile, pending verification responses are not requests to transfer again. Preserve the original challenge and transaction evidence, honor the operation's retry instructions, and reconcile an expired challenge if payment might already have been broadcast. An expired payment window is not proof that the purchase is unpaid.
Recovery windows are bounded. A successful challenge may return a cached receipt while it remains valid, and pending challenges may have a configured verification grace period. Those statements do not guarantee recovery after replay-store eviction. If the payment may have succeeded but the platform can no longer recover the receipt, preserve the evidence and escalate reconciliation rather than entering a new automatic payment loop.
Receipt consumption is a different boundary. The simple store described in the documentation consumes before the business handler runs. A failed handler or missing client response does not automatically make that receipt reusable. A shared, durable consumption store is needed across replicas and restarts; local memory is not a production recovery guarantee. Coordinate result persistence and delivery so duplicate workers or notifications cannot independently grant another purchased unit.
Secure result retrieval need not mean full vendor signup. An application might use a narrowly scoped recovery capability or a fresh proof of control associated with the purchase. These are design options, not claimed GOAT SDK features. The recovery path must authenticate the entitlement, limit its scope and lifetime, and avoid exposing results to anyone who merely guesses a purchase ID.
Keep order and receipt contracts distinct too. The GOAT Flow SDK reference documents operation-specific creation and recovery behavior: repeating an ordinary dappOrderId is not a general lookup returning the old order. Its historical order-proof signature is an unsigned digest, not the signed MPP receipt. Neither a plausible field name nor an ordinary order record should bypass the selected receipt verifier.
Finally, define compensation separately. Cancelling or expiring an order does not reverse an already-broadcast Crypto transfer. If recovery cannot fulfill the original purchase, apply an agreed support or refund process with its own authorization and evidence. Do not present a business error as a guaranteed automatic refund.
Price the Purchased Result, Not Each HTTP Attempt
The merchant should distinguish three operations: buying a new result, checking the status of an existing purchase, and recovering a previously purchased result. Charging every transport retry treats network unreliability as additional demand. It also gives buyers a reason to avoid an otherwise useful service.
For the hypothetical 0.05-USDC snapshot, an interrupted delivery remains the same logical purchase. A request for a different asset, a broader dataset, or a newly generated timestamp can be a new product if its terms say so. Define the boundary clearly enough that an agent can decide whether it is retrying a purchase or accepting a new quote.
The unit economics must include failures, not only successful responses. Consider an illustrative batch of 100 intended purchases at 0.05 USDC each: gross revenue would be 5 USDC. Assume five purchases are refunded under the merchant's own policy, leaving 4.75 USDC. If data/computation costs total 2 USDC, payment/infrastructure overhead totals 0.50 USDC, and recovery/support costs 0.20 USDC, the remaining contribution is 2.05 USDC before other business costs.
Every number in that calculation is hypothetical. It is not a network fee schedule, a measured failure rate, or a promise that a provider processes refunds automatically. Its purpose is to make the decision visible: a small price must cover the economic cost of an intended result, including handling failures and preserving recovery state.
Very cheap operations may not justify a separate economic settlement on each request, depending on the actual payment mechanism and overhead. A session, bundle, or recurring relationship can make sense for predictable high-volume use, although it changes the buyer's original no-credit-balance preference. Conversely, an occasional buyer may value one-off access more than a discounted subscription it will not use. Choose the commercial unit deliberately rather than assuming per-request billing is always cheaper.
Choose One Eligible Route and Prove Its Recovery Contract
Use reference x402 middleware when the buyer supports the chosen exchange and the team wants direct control over the resource server. Consider an independent MPP implementation only with its actual payment method and client requirements. A managed product may suit existing plan, token, delegation, or metering needs. An edge gateway is relevant only within its deployment and eligibility constraints.
GOAT Flow is worth evaluating when a merchant needs its documented paid-route or order/payment workflow, direct Crypto receiving, and a compatible verification path. The receipt profile can keep merchant administrative credentials away from buyers; it does not establish that every agent needs no setup or that private data can be sold without authorization. If the team's buyer cannot complete the selected profile, solve that compatibility gap before promising accountless access.
There is a relevant vendor-published example: GOAT Network's September 10, 2026 StableJack announcement reports 96 market-data endpoints priced at 0.5 USDC per call and describes access without signup. That is evidence of the use case GOAT publicly presents, not an independently reproduced purchase, a current universal price, or proof that this article's hypothetical route works.
Before release, demonstrate one successful eligible purchase and test forged signatures, expired receipts, a different merchant or route, query escalation, insufficient funds or gas, concurrent consumption, and a consumed receipt followed by lost delivery. Also test what happens when verification evidence is outside the recovery window. Persist the actual environment, compatible dependencies, redacted exchange, payment association, delivered result, and rejection/recovery outcomes.
No such runtime tests were performed for this guide. Begin with one eligible fixed-scope resource whose authorization and recovery rules you can explain. Expand only after the team can show that removing buyer signup has not removed spending control, data permission, or a safe way to recover what was already purchased.
FAQ
Is funding an agent wallet the same as buying prepaid API credits?
Not necessarily. Wallet funds may be usable with other compatible recipients, while vendor credits are governed by a specific platform's balance and redemption rules. Both still require budget control; neither means the agent can spend without limits.
Can a buyer recover a paid result without creating a login?
Yes, if the application provides a secure purchase-scoped retrieval mechanism. No-signup recovery is not unauthenticated recovery: possession of the appropriate capability or validated proof must still authorize the particular result. Do not assume that feature exists merely because payment verification succeeded.
Does a payment receipt give the agent ownership of the data?
No. It is payment/access evidence within its defined scope. Ownership, licensing, redistribution, confidentiality, and eligibility remain governed by the purchased terms and the underlying rights. The seller must enforce the relevant restrictions rather than treating a receipt as an unrestricted license.


